Not in the top 1,000 by GitHub stars
YingSuiAI/dirextalk-deployer
History
Review weekly changes to SKILL.md before updating. Dates mark the weeks in which we observed each version; checks apply to the recorded commits.
View weekly changes
SKILL.md
Week of Nov 2, 2026 · +0 / −0 lines
Before Network or broad shell → After Network or broad shell
266c73126202 → 266c73126202
Week of Oct 26, 2026 · Line counts unavailable
Before Not checked yet → After Network or broad shell
First observation → 266c73126202
No earlier version was observed for comparison.
.openclaw/dirextalk-deployer/SKILL.md
Week of Nov 2, 2026 · +0 / −0 lines
Before Network or broad shell → After Network or broad shell
266c73126202 → 266c73126202
Week of Oct 26, 2026 · Line counts unavailable
Before Not checked yet → After Network or broad shell
First observation → 266c73126202
No earlier version was observed for comparison.
Verified commit 266c73126202af0030432c17f079084e619f524d
git clone --filter=blob:none --no-checkout https://github.com/YingSuiAI/dirextalk-deployer.git .hotskills/yingsuiai-dirextalk-deployer && git -C .hotskills/yingsuiai-dirextalk-deployer checkout --detach 266c73126202af0030432c17f079084e619f524d
# Copy each selected skill directory from .hotskills/yingsuiai-dirextalk-deployer into .agents/skills/<skill-name>/Heat
0.4- Star growth, last 7 daysNot available
- Star growth, last 24 hoursNot available
- Rank movement, last 7 daysNot available
- Commits, last 30 daysNot available
- Accounts asking about it through MCP, last 7 daysNot available
- Hot votes this weekNot available
Heat never changes the order by stars, and sponsorship never touches it. How heat works
Stars over time
30-day change not yet available: not enough history.
Individual skills in this repository
- dirextalk-deployer
/ - dirextalk-deployer
.openclaw/dirextalk-deployer
How it works
dirextalk-deployer
When your agent uses it
Deploy, resume, verify, update, recover, reset, or destroy production Dirextalk services and nodes on AWS, and wire local agent runtimes. Use when the user explicitly invokes `$dirextalk-deployer` or asks in natural language to deploy, update, repair, verify, resume, reset, or destroy a Dirextalk service or node.
What it loads into context
Frontmatter
82 tokensAlways available to the agent
SKILL.md
6,444 tokensWhen the skill is activated
Reference documents
56,940 tokensLoaded on request
Token counts are estimates. Scripts run separately; they are not counted as reference context.
The playbook
- Freshness Gate
- Platform Law
- Prerequisites And Confirmation
- Local Runtime Wiring
- Deployment Completion
- Status, Reports, And Delivery
- Update, Reset, And Destroy
- References
Scripts executed separately
bin/dirextalk-deployer.mjspackage.jsonscripts/aws-credentials.shscripts/cloud-init/split/.npmignorescripts/cloud-init/split/Caddyfilescripts/cloud-init/split/advance-split-source-revision.shscripts/cloud-init/split/apply-host-integration.shscripts/cloud-init/split/authorize-split-source-revision.shscripts/cloud-init/split/bootstrap-production.shscripts/cloud-init/split/migrate-message-mcp-token-binding.shscripts/cloud-init/split/production-ops-common.shscripts/cloud-init/split/reconcile-production.shscripts/cloud-init/split/recover-production.shscripts/cloud-init/split/reset-production.shscripts/cloud-init/split/runtime/.gitignorescripts/cloud-init/split/runtime/apparmor.d/dirextalk-runner-usernsscripts/cloud-init/split/runtime/scripts/agent-runtime-local-common.shscripts/cloud-init/split/runtime/scripts/cleanup-local.shscripts/cloud-init/split/runtime/scripts/cleanup-provision-failure.shscripts/cloud-init/split/runtime/scripts/ensure-host-null-device.shscripts/cloud-init/split/runtime/scripts/export-portal-bootstrap.shscripts/cloud-init/split/runtime/scripts/initialize-capability-ca.shscripts/cloud-init/split/runtime/scripts/initialize-message-server.shscripts/cloud-init/split/runtime/scripts/initialize-postgres.shscripts/cloud-init/split/runtime/scripts/manage-runner-apparmor.shscripts/cloud-init/split/runtime/scripts/materialize-agent-secrets.shscripts/cloud-init/split/runtime/scripts/message-server-entrypoint.shscripts/cloud-init/split/runtime/scripts/postgres-entrypoint.shscripts/cloud-init/split/runtime/scripts/prepare-agent-start-local.shscripts/cloud-init/split/runtime/scripts/prepare-host-dependencies.shscripts/cloud-init/split/runtime/scripts/prepare-runner-cgroups.shscripts/cloud-init/split/runtime/scripts/provision-local.shscripts/cloud-init/split/runtime/scripts/recover-starting-cleanup-receipt.shscripts/cloud-init/split/runtime/scripts/refresh-message-mcp-token.shscripts/cloud-init/split/runtime/scripts/restart-agent-local.shscripts/cloud-init/split/runtime/scripts/start-local.shscripts/cloud-init/split/runtime/scripts/stop-agent-local.shscripts/cloud-init/split/runtime/scripts/update-agent-local.shscripts/cloud-init/split/runtime/scripts/update-message-server-local.shscripts/cloud-init/split/runtime/scripts/verify-production-images.shscripts/destroy.shscripts/json.mjsscripts/lib/atomic-write.shscripts/lib/aws.shscripts/lib/connect-agent-adapters.shscripts/lib/connect-daemon-logs.shscripts/lib/domain.shscripts/lib/git-bash.shscripts/lib/http-secrets.shscripts/lib/json-worker.mjsscripts/lib/json.shscripts/lib/local-paths.shscripts/lib/mcp-client-adapters.shscripts/lib/operation_report.shscripts/lib/ops.shscripts/lib/paths.shscripts/lib/private-files.shscripts/lib/production-release-resolver.mjsscripts/lib/region.shscripts/lib/remote-mcp-contract.shscripts/lib/server-release.shscripts/lib/state.shscripts/lib/test-runner.mjsscripts/lib/updater-release.shscripts/orchestrate.shscripts/phases/remote_dns_probe.pyscripts/phases/s0_prereq_aws.shscripts/phases/s1_preflight.shscripts/phases/s2_domain.shscripts/phases/s3_provision.shscripts/phases/s4_bootstrap_stack.shscripts/phases/s5_init_tokens.shscripts/phases/s6_wire_local.shscripts/phases/s7_verify_e2e.shscripts/pricing-estimate.shscripts/render/prepare-production-release.shscripts/render/render-split-bundle.shscripts/render/render-userdata.shscripts/reset-app-data.shscripts/run-tests.mjsscripts/update.shscripts/updater/bootstrap-host.shscripts/updater/install.shscripts/updater/reconcile-host.shscripts/updater/set-desired-state.shtests/atomic_write_test.shtests/aws_credentials_test.shtests/aws_proxy_environment_test.shtests/bootstrap_production_retry_test.shtests/destroy_host_mcp_cleanup_test.shtests/destroy_lightsail_test.shtests/destroy_local_bridge_test.shtests/destroy_root_identity_test.shtests/domain_authoritative_dns_test.shtests/domain_dns_mode_detection_test.shtests/domain_route53_default_test.shtests/eip_preflight_test.shtests/existing_node_update_test.shtests/final_delivery_runtime_gate_test.shtests/fixtures/split-stack-fault-upstream.mjstests/git_bash_windows_contract_test.shtests/host_integration_atomic_test.shtests/json_helper_test.shtests/lib/isolated_home.shtests/lib/json_test.shtests/lib/linux-flock.shtests/lib/linux-install.shtests/lib/run_isolated.shtests/lib/split-release.shtests/lightsail_static_ip_quota_test.shtests/local_paths_test.shtests/mcp_tools_runtime_check_test.shtests/message_mcp_binding_migration_test.shtests/npm_skill_distribution_test.shtests/npm_test_suite.shtests/operation_report_test.shtests/orchestrate_expected_negative_test.shtests/orchestrate_lock_test.shtests/orchestrate_region_env_test.shtests/orchestrate_status_recovery_test.shtests/pricing_estimate_test.shtests/private_file_permissions_test.shtests/production_recovery_test.shtests/production_release_prepare_test.shtests/production_release_resolver_test.mjstests/region_recommendation_test.shtests/release_candidate_rollback_test.shtests/remote_dns_probe_test.shtests/render_userdata_remote_nodes_test.shtests/root_volume_size_test.shtests/route53_zone_required_test.shtests/runtime_summary_check_test.shtests/s1_lightsail_availability_fallback_test.shtests/s3_ec2_updater_upload_test.shtests/s3_lightsail_provision_test.shtests/s3_public_ip_validation_test.shtests/s3_stable_ip_reconcile_test.shtests/s5_init_tokens_test.shtests/s6_run_phase_failure_test.shtests/s6_wire_local_test.shtests/s7_http_mcp_acceptance_test.shtests/server_release_test.shtests/skill_structure_test.shtests/split-runtime/agent-runtime-local.test.shtests/split-runtime/cleanup-local.test.shtests/split-runtime/cleanup-provision-failure.test.shtests/split-runtime/compose-runner-limits.test.shtests/split-runtime/ensure-host-null-device.test.shtests/split-runtime/initialize-capability-ca.test.shtests/split-runtime/initialize-message-server.test.shtests/split-runtime/initialize-postgres.test.shtests/split-runtime/manage-runner-apparmor.test.shtests/split-runtime/message-server-entrypoint.test.shtests/split-runtime/message-server-healthcheck.test.shtests/split-runtime/postgres-entrypoint.docker.test.shtests/split-runtime/prepare-host-dependencies.test.shtests/split-runtime/prepare-runner-cgroups.test.shtests/split-runtime/refresh-message-mcp-token.test.shtests/split-runtime/update-agent-local.docker.test.shtests/split-runtime/update-agent-local.recovery.test.shtests/split-runtime/update-agent-local.test.shtests/split-runtime/update-message-server-local.rollback.test.shtests/split-runtime/update-message-server-local.test.shtests/split-runtime/verify-production-images.test.shtests/split_agent_bundle_test.shtests/split_runtime_contract_test.shtests/split_runtime_docker_test.shtests/split_source_revision_advance_test.shtests/split_stack_fault_gate_test.shtests/static_sites_edge_test.shtests/test_runner_entry_test.mjstests/tracked_text_lf_test.shtests/update_reset_ops_test.shtests/updater_atomic_install_test.shtests/updater_bootstrap_resume_test.shtests/updater_bundle_test.shtests/updater_desired_state_transition_test.shtests/updater_existing_state_transition_test.shtests/updater_platform_contract_test.shtests/updater_release_download_test.shtests/updater_release_pin_test.sh
Files
.editorconfigasset78 bytes.gitattributesasset36 bytes.github/workflows/ci.ymlasset1,611 bytes.gitignoreasset52 bytes.superpowers/sdd/task-3-report.mddoc7,417 bytesAGENTS.mddoc14,463 bytesLICENSEasset1,066 bytesREADME.mddoc21,473 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesSKILL.mdcore28,884 bytesagents/README.mddoc1,809 bytesagents/openai.yamlasset292 bytesassets/dirextalk-platform.pngasset246,461 bytesbin/dirextalk-deployer.mjsruns16,620 bytesdocs/superpowers/plans/2026-06-30-npm-skill-distribution.mddoc5,092 bytesdocs/superpowers/plans/2026-06-30-remove-jq-dependency.mddoc4,082 bytesdocs/superpowers/plans/2026-07-01-cursor-windows-runtime-hardening.mddoc6,759 bytesdocs/superpowers/plans/2026-07-01-mcp-daemon.mddoc2,435 bytesdocs/superpowers/plans/2026-07-03-region-and-lightsail-choice.mddoc10,822 bytesdocs/superpowers/plans/2026-07-10-remote-mcp-connect-contract.mddoc5,202 bytesdocs/superpowers/specs/2026-06-30-npm-skill-distribution-design.mddoc4,465 bytesdocs/superpowers/specs/2026-06-30-remove-jq-dependency-design.mddoc2,766 bytesdocs/superpowers/specs/2026-07-01-mcp-daemon-design.mddoc1,660 bytesdocs/superpowers/specs/2026-07-03-region-and-lightsail-choice-design.mddoc5,600 bytesdocs/superpowers/specs/2026-07-10-remote-mcp-connect-contract.mddoc7,716 bytespackage-lock.jsonasset359 bytespackage.jsonruns1,260 bytesreferences/agent-targets.mddoc13,382 bytesreferences/architecture.mddoc5,832 bytesreferences/bug-history.mddoc7,624 bytesreferences/deployment-lessons.mddoc10,206 bytesreferences/deployment-optimization-audit.mddoc14,601 bytesreferences/deployment-workflow.mddoc19,254 bytesreferences/iam-policy.jsonasset1,444 bytesreferences/runtime-wiring.mddoc15,417 bytesreferences/state-machine.mddoc7,166 bytesreferences/token-refresh.mddoc4,831 bytesreferences/tooling.mddoc3,442 bytesreferences/troubleshooting.mddoc2,023 bytesreferences/user-journey.mddoc4,699 bytesreferences/verification-recovery.mddoc11,396 bytesreferences/voip-turn-runbook.mddoc2,573 bytesreferences/windows-deployment-notes.mddoc8,657 bytesscripts/aws-credentials.shruns5,948 bytesscripts/cloud-init/split/.npmignoreruns9 bytesscripts/cloud-init/split/Caddyfileruns1,861 bytesscripts/cloud-init/split/README.mddoc2,805 bytesscripts/cloud-init/split/advance-split-source-revision.shruns5,320 bytesscripts/cloud-init/split/apply-host-integration.shruns16,184 bytesscripts/cloud-init/split/authorize-split-source-revision.shruns4,221 bytesscripts/cloud-init/split/bootstrap-production.shruns23,696 bytesscripts/cloud-init/split/canonical-bundle.tar.gzasset83,462 bytesscripts/cloud-init/split/canonical-bundle.tar.gz.sha256asset90 bytesscripts/cloud-init/split/dirextalk-split-recovery.serviceasset342 bytesscripts/cloud-init/split/edge-compose.override.yamlasset153 bytesscripts/cloud-init/split/migrate-message-mcp-token-binding.shruns357 bytesscripts/cloud-init/split/production-ops-common.shruns27,325 bytesscripts/cloud-init/split/reconcile-production.shruns5,568 bytesscripts/cloud-init/split/recover-production.shruns7,840 bytesscripts/cloud-init/split/release.envasset545 bytesscripts/cloud-init/split/reset-production.shruns1,059 bytesscripts/cloud-init/split/runtime/.gitignoreruns285 bytesscripts/cloud-init/split/runtime/README.mddoc4,022 bytesscripts/cloud-init/split/runtime/apparmor.d/dirextalk-runner-usernsruns740 bytesscripts/cloud-init/split/runtime/compose.production.yamlasset618 bytesscripts/cloud-init/split/runtime/compose.yamlasset27,242 bytesscripts/cloud-init/split/runtime/edge-compose.yamlasset2,122 bytesscripts/cloud-init/split/runtime/scripts/agent-runtime-local-common.shruns24,028 bytesscripts/cloud-init/split/runtime/scripts/cleanup-local.shruns35,849 bytesscripts/cloud-init/split/runtime/scripts/cleanup-provision-failure.shruns22,890 bytesscripts/cloud-init/split/runtime/scripts/ensure-host-null-device.shruns6,073 bytesscripts/cloud-init/split/runtime/scripts/export-portal-bootstrap.shruns3,627 bytesscripts/cloud-init/split/runtime/scripts/initialize-capability-ca.shruns4,160 bytesscripts/cloud-init/split/runtime/scripts/initialize-message-server.shruns4,703 bytesscripts/cloud-init/split/runtime/scripts/initialize-postgres.shruns2,463 bytesscripts/cloud-init/split/runtime/scripts/manage-runner-apparmor.shruns6,421 bytesscripts/cloud-init/split/runtime/scripts/materialize-agent-secrets.shruns1,299 bytesscripts/cloud-init/split/runtime/scripts/message-server-entrypoint.shruns2,229 bytesscripts/cloud-init/split/runtime/scripts/postgres-entrypoint.shruns3,246 bytesscripts/cloud-init/split/runtime/scripts/prepare-agent-start-local.shruns296 bytesscripts/cloud-init/split/runtime/scripts/prepare-host-dependencies.shruns620 bytesscripts/cloud-init/split/runtime/scripts/prepare-runner-cgroups.shruns34,426 bytesscripts/cloud-init/split/runtime/scripts/provision-local.shruns59,868 bytesscripts/cloud-init/split/runtime/scripts/recover-starting-cleanup-receipt.shruns15,696 bytesscripts/cloud-init/split/runtime/scripts/refresh-message-mcp-token.shruns7,923 bytesscripts/cloud-init/split/runtime/scripts/restart-agent-local.shruns296 bytesscripts/cloud-init/split/runtime/scripts/start-local.shruns62,977 bytesscripts/cloud-init/split/runtime/scripts/stop-agent-local.shruns293 bytesscripts/cloud-init/split/runtime/scripts/update-agent-local.shruns40,524 bytesscripts/cloud-init/split/runtime/scripts/update-message-server-local.shruns9,517 bytesscripts/cloud-init/split/runtime/scripts/verify-production-images.shruns6,251 bytesscripts/cloud-init/split/runtime/systemd/dirextalk-core-runner@.serviceasset488 bytesscripts/cloud-init/split/runtime/systemd/dirextalk-extension-runner@.serviceasset501 bytesscripts/cloud-init/split/runtime/sysusers.d/dirextalk-split-agent.confasset372 bytesscripts/cloud-init/user-data.yamlasset703 bytesscripts/destroy.shruns26,771 bytesscripts/json.mjsruns39,963 bytesscripts/lib/atomic-write.shruns1,052 bytesscripts/lib/aws.shruns2,471 bytesscripts/lib/connect-agent-adapters.shruns11,065 bytesscripts/lib/connect-daemon-logs.shruns1,460 bytesscripts/lib/domain.shruns6,854 bytesscripts/lib/git-bash.shruns2,382 bytesscripts/lib/http-secrets.shruns958 bytesscripts/lib/json-worker.mjsruns3,854 bytesscripts/lib/json.shruns6,214 bytesscripts/lib/local-paths.shruns3,768 bytesscripts/lib/mcp-client-adapters.shruns32,785 bytesscripts/lib/operation_report.shruns1,767 bytesscripts/lib/ops.shruns25,566 bytesscripts/lib/paths.shruns1,368 bytesscripts/lib/private-files.shruns2,367 bytesscripts/lib/production-release-resolver.mjsruns11,409 bytesscripts/lib/region.shruns2,769 bytesscripts/lib/remote-mcp-contract.shruns1,161 bytesscripts/lib/server-release.shruns24,765 bytesscripts/lib/state.shruns4,309 bytesscripts/lib/test-runner.mjsruns14,678 bytesscripts/lib/updater-release.shruns1,446 bytesscripts/orchestrate.shruns51,862 bytesscripts/phases/remote_dns_probe.pyruns4,219 bytesscripts/phases/s0_prereq_aws.shruns3,074 bytesscripts/phases/s1_preflight.shruns12,916 bytesscripts/phases/s2_domain.shruns7,429 bytesscripts/phases/s3_provision.shruns56,186 bytesscripts/phases/s4_bootstrap_stack.shruns2,421 bytesscripts/phases/s5_init_tokens.shruns9,622 bytesscripts/phases/s6_wire_local.shruns58,553 bytesscripts/phases/s7_verify_e2e.shruns5,498 bytesscripts/pricing-estimate.shruns12,030 bytesscripts/render/prepare-production-release.shruns3,486 bytesscripts/render/render-split-bundle.shruns5,166 bytesscripts/render/render-userdata.shruns8,507 bytesscripts/reset-app-data.shruns1,619 bytesscripts/run-tests.mjsruns450 bytesscripts/update.shruns3,012 bytesscripts/updater/bootstrap-host.shruns12,140 bytesscripts/updater/config.jsonasset217 bytesscripts/updater/dirextalk-updater.serviceasset726 bytesscripts/updater/install.shruns3,039 bytesscripts/updater/reconcile-host.shruns20,191 bytesscripts/updater/release.envasset416 bytesscripts/updater/set-desired-state.shruns3,120 bytestests/atomic_write_test.shruns2,203 bytestests/aws_credentials_test.shruns4,860 bytestests/aws_proxy_environment_test.shruns738 bytestests/bootstrap_production_retry_test.shruns16,651 bytestests/destroy_host_mcp_cleanup_test.shruns3,730 bytestests/destroy_lightsail_test.shruns2,594 bytestests/destroy_local_bridge_test.shruns4,616 bytestests/destroy_root_identity_test.shruns3,034 bytestests/domain_authoritative_dns_test.shruns1,276 bytestests/domain_dns_mode_detection_test.shruns3,303 bytestests/domain_route53_default_test.shruns1,373 bytestests/eip_preflight_test.shruns1,814 bytestests/existing_node_update_test.shruns18,044 bytestests/final_delivery_runtime_gate_test.shruns7,836 bytestests/fixtures/split-stack-fault-upstream.mjsruns2,065 bytestests/git_bash_windows_contract_test.shruns5,051 bytestests/host_integration_atomic_test.shruns13,097 bytestests/json_helper_test.shruns4,678 bytestests/lib/isolated_home.shruns2,115 bytestests/lib/json_test.shruns136 bytestests/lib/linux-flock.shruns1,453 bytestests/lib/linux-install.shruns1,621 bytestests/lib/run_isolated.shruns2,128 bytestests/lib/split-release.shruns3,443 bytestests/lightsail_static_ip_quota_test.shruns2,634 bytestests/local_paths_test.shruns8,072 bytestests/mcp_tools_runtime_check_test.shruns3,771 bytestests/message_mcp_binding_migration_test.shruns5,629 bytestests/npm_skill_distribution_test.shruns11,749 bytestests/npm_test_suite.shruns1,470 bytestests/operation_report_test.shruns13,638 bytestests/orchestrate_expected_negative_test.shruns1,860 bytestests/orchestrate_lock_test.shruns2,468 bytestests/orchestrate_region_env_test.shruns809 bytestests/orchestrate_status_recovery_test.shruns5,347 bytestests/pricing_estimate_test.shruns6,136 bytestests/private_file_permissions_test.shruns1,696 bytestests/production_recovery_test.shruns19,902 bytestests/production_release_prepare_test.shruns3,350 bytestests/production_release_resolver_test.mjsruns9,151 bytestests/region_recommendation_test.shruns666 bytestests/release_candidate_rollback_test.shruns1,064 bytestests/remote_dns_probe_test.shruns3,289 bytestests/render_userdata_remote_nodes_test.shruns5,645 bytestests/root_volume_size_test.shruns902 bytestests/route53_zone_required_test.shruns3,755 bytestests/runtime_summary_check_test.shruns7,679 bytestests/s1_lightsail_availability_fallback_test.shruns2,527 bytestests/s3_ec2_updater_upload_test.shruns6,160 bytestests/s3_lightsail_provision_test.shruns14,766 bytestests/s3_public_ip_validation_test.shruns5,602 bytestests/s3_stable_ip_reconcile_test.shruns3,181 bytestests/s5_init_tokens_test.shruns9,360 bytestests/s6_run_phase_failure_test.shruns16,688 bytestests/s6_wire_local_test.shruns62,613 bytestests/s7_http_mcp_acceptance_test.shruns6,481 bytestests/server_release_test.shruns6,354 bytestests/skill_structure_test.shruns25,573 bytestests/split-runtime/agent-runtime-local.test.shruns25,778 bytestests/split-runtime/cleanup-local.test.shruns32,577 bytestests/split-runtime/cleanup-provision-failure.test.shruns13,791 bytestests/split-runtime/compose-runner-limits.test.shruns7,589 bytestests/split-runtime/ensure-host-null-device.test.shruns2,534 bytestests/split-runtime/initialize-capability-ca.test.shruns1,256 bytestests/split-runtime/initialize-message-server.test.shruns3,121 bytestests/split-runtime/initialize-postgres.test.shruns2,417 bytestests/split-runtime/manage-runner-apparmor.test.shruns3,883 bytestests/split-runtime/message-server-entrypoint.test.shruns2,520 bytestests/split-runtime/message-server-healthcheck.test.shruns1,915 bytestests/split-runtime/postgres-entrypoint.docker.test.shruns5,453 bytestests/split-runtime/prepare-host-dependencies.test.shruns1,565 bytestests/split-runtime/prepare-runner-cgroups.test.shruns18,804 bytestests/split-runtime/refresh-message-mcp-token.test.shruns5,077 bytestests/split-runtime/update-agent-local.docker.test.shruns10,127 bytestests/split-runtime/update-agent-local.recovery.test.shruns29,574 bytestests/split-runtime/update-agent-local.test.shruns2,923 bytestests/split-runtime/update-message-server-local.rollback.test.shruns3,644 bytestests/split-runtime/update-message-server-local.test.shruns896 bytestests/split-runtime/verify-production-images.test.shruns2,719 bytestests/split_agent_bundle_test.shruns26,315 bytestests/split_runtime_contract_test.shruns1,468 bytestests/split_runtime_docker_test.shruns684 bytestests/split_source_revision_advance_test.shruns6,535 bytestests/split_stack_fault_gate_test.shruns8,761 bytestests/static_sites_edge_test.shruns3,898 bytestests/test_runner_entry_test.mjsruns4,605 bytestests/tracked_text_lf_test.shruns1,861 bytestests/update_reset_ops_test.shruns18,264 bytestests/updater_atomic_install_test.shruns3,779 bytestests/updater_bootstrap_resume_test.shruns7,636 bytestests/updater_bundle_test.shruns2,340 bytestests/updater_desired_state_transition_test.shruns3,146 bytestests/updater_existing_state_transition_test.shruns18,391 bytestests/updater_platform_contract_test.shruns1,207 bytestests/updater_release_download_test.shruns6,362 bytestests/updater_release_pin_test.shruns1,657 bytes
Read SKILL.md
# Dirextalk Deployer

This skill is the compact agent-facing entrypoint. Treat this repository root
as the execution engine and read the referenced docs only when that phase needs
detail.

Entrypoints:

```text
scripts/orchestrate.sh
scripts/destroy.sh
scripts/update.sh
scripts/reset-app-data.sh
```dirextalk-deployer
When your agent uses it
Deploy, resume, verify, update, recover, reset, or destroy production Dirextalk services and nodes on AWS. Use when the user explicitly invokes `$dirextalk-deployer` or asks in natural language for one of these Dirextalk lifecycle operations.
What it loads into context
Frontmatter
139 tokensAlways available to the agent
SKILL.md
504 tokensWhen the skill is activated
Reference documents
0 tokensLoaded on request
Token counts are estimates. Scripts run separately; they are not counted as reference context.
The playbook
Scripts executed separately
../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh../../scripts/orchestrate.sh
Files
.clawhubignoreasset80 bytesSKILL.mdcore2,167 bytesSKILL.mdcore2,167 bytesSKILL.mdcore2,167 bytesSKILL.mdcore2,167 bytesSKILL.mdcore2,167 bytesSKILL.mdcore2,167 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes../../scripts/orchestrate.shruns51,862 bytes
Read SKILL.md
# Dirextalk Deployer

This is the OpenClaw distribution of `dirextalk-deployer`. It is a thin
bootstrap skill: the executable deployment engine must always come from the
versioned npm package, not from a Git clone or this ClawHub bundle.

Before deployment, repair, verification, update, or teardown, install the
latest package:

```bash
npm install -g dirextalk-deployer@latest
```

Use the installed CLI to refresh the host-level skill when needed:Skills included
- dirextalk-deployer
- dirextalk-deployer
Repository facts
- License
- MIT
- Created
- Jun 24, 2026
- Last pushed
- Sep 2, 2026
- Forks
- 83
- Open issues
- 0
- Project activity
- Slowing
Before you install
Network or broad shellAutomated signals, not a guarantee
Checked Nov 4, 2026
Not fully analyzed: some files were too long, unreadable or missing. This never lowers the level.
Show 56 notes
SKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedSKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzedtests/operation_report_test.sh:34[Credential-related source omitted].openclaw/dirextalk-deployer/SKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzed.openclaw/dirextalk-deployer/SKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzed.openclaw/dirextalk-deployer/SKILL.md:1Analysis incomplete: Referenced executable target unavailable; not analyzed
- No broad tool permissions
- 407 dangerous shell commandsin 131 files: scripts/orchestrate.sh:68 scripts/lib/ops.sh:22 scripts/phases/s3_provision.sh:375 and 128 more
- 810 network referencesin 86 files: tests/s6_wire_local_test.sh:65 tests/s7_http_mcp_acceptance_test.sh:42 tests/production_release_resolver_test.mjs:108 and 83 more
- 10 obfuscation signalsin 7 files: scripts/cloud-init/split/production-ops-common.sh:100 tests/operation_report_test.sh:34 scripts/lib/ops.sh:352 and 4 more
- No instruction overrides
- 216 executable scriptsin 181 files: scripts/orchestrate.sh:1 bin/dirextalk-deployer.mjs:1 package.json:1 and 178 more
- 549 references to secretsin 68 files: scripts/cloud-init/split/production-ops-common.sh:33 tests/split-runtime/update-agent-local.recovery.test.sh:158 scripts/cloud-init/split/runtime/scripts/cleanup-provision-failure.sh:23 and 65 more
- No requests to vote in Hot
Show all 1,992 signals by file
.openclaw/dirextalk-deployer/SKILL.md
- Network accessline 13
bins: - dirextalk-deployer homepage: https://github.com/YingSuiAI/dirextalk-deployer - Network accessline 14
- dirextalk-deployer homepage: https://github.com/YingSuiAI/dirextalk-deployer emoji: "☁<U+FE0F>" - Network accessline 15
homepage: https://github.com/YingSuiAI/dirextalk-deployer - Network accessline 62
Read https://github.com/YingSuiAI/dirextalk-deployer README and follow its npm install rule.
AGENTS.md
- Network accessline 60
- Remote server commands may assume Linux because the EC2 host is Linux. Local commands must not assume Linux. - Production split cloud hosts require Ubuntu 24.04+ on x86_64 with systemd >= 254; bootstrap must verify that host contract befo - Network accessline 61
- Production split cloud hosts require Ubuntu 24.04+ on x86_64 with systemd >= 254; bootstrap must verify that host contract before downloading the pinned updater or starting Compose. - Use `dirextalk_native_tool_path` at every shell-to-nat - Network accessline 62
- Use `dirextalk_native_tool_path` at every shell-to-native file-path boundary and `dirextalk_normalize_local_path` for persisted consumer paths. This includes Node scripts and input files, AWS `file://` arguments, curl output/header files, - Access to secretsline 69
[Credential-related source omitted] - Access to secretsline 81
[Credential-related source omitted]
README.md
- Network accessline 7
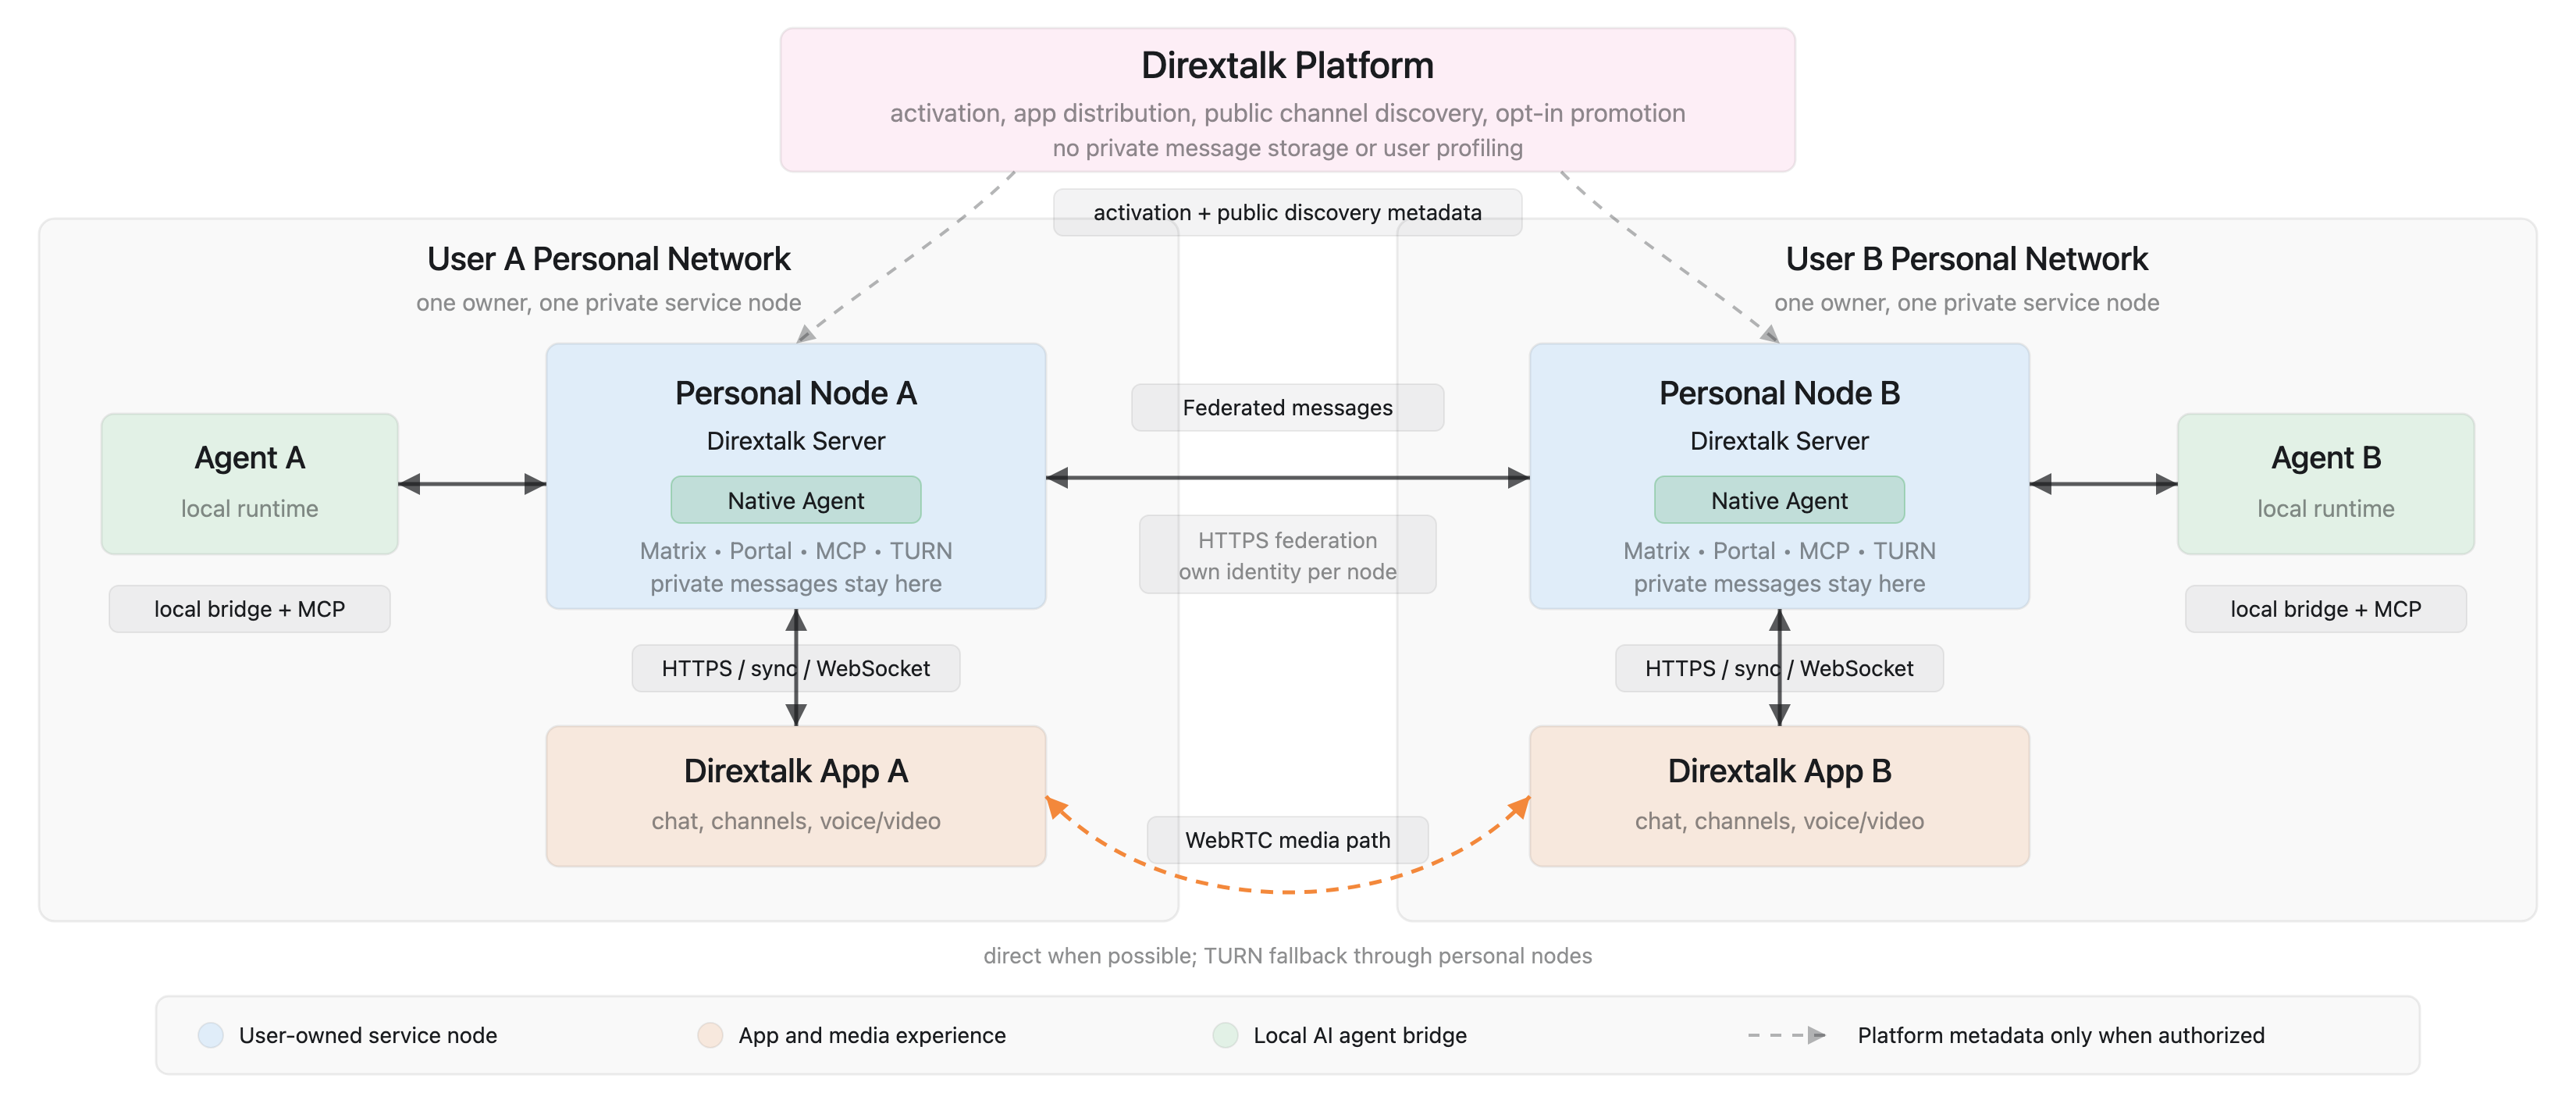 - Network accessline 19
The [Dirextalk web deployment console](https://deployer.dirextalk.ai/) provides a browser workflow for backend-only AWS deployment. It provisions, resumes, verifies, and destroys the cloud message-server resources, but it does **not** insta - Network accessline 21
For local agent-room wiring, use this npm-installed [dirextalk-deployer skill](https://github.com/YingSuiAI/dirextalk-deployer) instead. Visit [dirextalk.ai](https://dirextalk.ai/) for the product website. - Network accessline 44
If it fails, install Git for Windows from <https://git-scm.com/download/win>, - Network accessline 57
Read https://github.com/YingSuiAI/dirextalk-deployer README and follow its npm install rule, then deploy Dirextalk with domain __DOMAIN__. - Network accessline 142
Server container and repair runner cgroup delegation before any Agent-only restart. The target host never clones either source repository. The host updater is a separate [`dirextalk-updater`](https://github.com/YingSuiAI/dirextalk-updater) - Network accessline 143
restart. The target host never clones either source repository. The host updater is a separate [`dirextalk-updater`](https://github.com/YingSuiAI/dirextalk-updater) Release: the supported Ubuntu 24.04+ x86_64 host with systemd >= 254 downlo - Network accessline 144
[`dirextalk-updater`](https://github.com/YingSuiAI/dirextalk-updater) Release: - Network accessline 157
On native Windows, install Git for Windows, open **Git Bash**, and use the same commands as Linux/macOS. Run the Git Bash preflight in **Skill Installation And Updates** before any lifecycle command; if it fails, install Git from `https://g - Access to secretsline 312
[Credential-related source omitted] - Network accessline 317
git clone https://github.com/YingSuiAI/dirextalk-connect.git
SKILL.md
- Network accessline 36
the current shell's `EXEPATH` is under the same Git for Windows installation as `git`, and rejects PowerShell, MSYS2, and Cygwin. Otherwise tell the Windows user to install Git for Windows from `https://git-scm.com/download/win`, reopen - Network accessline 37
`git`, and rejects PowerShell, MSYS2, and Cygwin. Otherwise tell the Windows user to install Git for Windows from `https://git-scm.com/download/win`, reopen Git Bash, and stop. The skill CLI repeats and strengthens the Windows gate - Network accessline 38
user to install Git for Windows from `https://git-scm.com/download/win`, reopen - Network accessline 77
Git for Windows is required: use the exact preflight above before any deployment action. If it fails, tell the user to install Git for Windows from `https://git-scm.com/download/win`, open **Git Bash**, and rerun; do not - Network accessline 78
action. If it fails, tell the user to install Git for Windows from `https://git-scm.com/download/win`, open **Git Bash**, and rerun; do not substitute PowerShell or launch WSL as a command runner for a Windows-owned - Network accessline 79
`https://git-scm.com/download/win`, open **Git Bash**, and rerun; do not - Network accessline 128
- If yes, continue to the access key step. - If no, ask the user to open `https://signin.aws.amazon.com/signup?request_type=register`, register in - Network accessline 129
- If no, ask the user to open `https://signin.aws.amazon.com/signup?request_type=register`, register in their browser, complete payment/phone verification and Basic support - Network accessline 130
`https://signin.aws.amazon.com/signup?request_type=register`, register in - Network accessline 309
The supported local bridge is `dirextalk-connect`, installed from `dirextalk-connect@latest` by default or built from `https://github.com/YingSuiAI/dirextalk-connect.git`. The MCP tool surface is - Network accessline 310
`dirextalk-connect@latest` by default or built from `https://github.com/YingSuiAI/dirextalk-connect.git`. The MCP tool surface is served by the deployed message server's HTTP MCP endpoint. - Network accessline 311
`https://github.com/YingSuiAI/dirextalk-connect.git`. The MCP tool surface is
bin/dirextalk-deployer.mjs
package.json
- Executable scriptline 1
Executable file
references/agent-targets.md
- Network accessline 20
If it fails, install Git for Windows from <https://git-scm.com/download/win>, - Network accessline 27
Read https://github.com/YingSuiAI/dirextalk-deployer README and follow its npm install rule, then deploy Dirextalk with domain __DOMAIN__. - Access to secretsline 96
[Credential-related source omitted]
references/architecture.md
- Network accessline 20
- **message-server**: 每个 fresh deployment 从 Docker Hub `latest` 发现当前版本,核对对应稳定 `vX.Y.Z` 标签、source revision 与 linux/amd64 manifest digest,并在创建基础设施前冻结到 `state.json`;retry/resume 不重新解析。运行时继续使用该稳定版本标签。它承载 Matrix homeserver 和 ProductCore,自身 build - Network accessline 21
- **Agent**: 每个 fresh deployment 通过独立 `latest` 通道完成相同的稳定标签、source revision 与 linux/amd64 manifest digest 校验,并与 Message Server snapshot 原子冻结;existing node 保留已有 receipt。Cloud Worker 的主机区域只来自已验证部署主机的不可变区域,不读取上传凭据的默认区域,也不跨区域 fallback。它与 Message - Access to secretsline 44
[Credential-related source omitted]
references/bug-history.md
- Access to secretsline 44
[Credential-related source omitted] - Access to secretsline 50
[Credential-related source omitted] - Dangerous shell operationline 66
- **宿主机读不到凭据文件**:message-server 在容器内写 `/var/dirextalk-message-server/p2p/bootstrap.json`,宿主机 S5 无法直接读取 Docker named volume。修:compose 把容器 `/var/dirextalk-message-server/p2p` bind 到宿主同路径,S5 用 `ssh ... sudo cat /var/dirextalk-message-server/p2 - Network accessline 66
- **宿主机读不到凭据文件**:message-server 在容器内写 `/var/dirextalk-message-server/p2p/bootstrap.json`,宿主机 S5 无法直接读取 Docker named volume。修:compose 把容器 `/var/dirextalk-message-server/p2p` bind 到宿主同路径,S5 用 `ssh ... sudo cat /var/dirextalk-message-server/p2 - Network accessline 68
- **(client 侧,不在本仓库)** `/_as/auth` 返回容器内网 `http://dendrite:8008`,App 在用户机访问不到 → 前端遇到 `dendrite` 这类内部 host 时回退到用户输入的公网 Portal 地址。
references/deployment-lessons.md
- Network accessline 54
If the Git Bash preflight fails, install Git for Windows from <https://git-scm.com/download/win>, reopen Git Bash, and stop. Do not substitute - Network accessline 55
<https://git-scm.com/download/win>, reopen Git Bash, and stop. Do not substitute - Network accessline 72
- `state.json` stays at `S4_BOOTSTRAP_STACK=polling`. - `https://<domain>/_p2p/health` returns `{"status":"ok"}` from another shell. - A leftover local `curl -skf https://<domain>/_p2p/health` or SSH child process is - Network accessline 73
- `https://<domain>/_p2p/health` returns `{"status":"ok"}` from another shell. - A leftover local `curl -skf https://<domain>/_p2p/health` or SSH child process is still running after the agent/operator interrupted the deployment turn. - Network accessline 74
- A leftover local `curl -skf https://<domain>/_p2p/health` or SSH child process is - Network accessline 86
- S4 health checks use per-attempt curl timeouts: - Dangerous shell operationline 185
sudo docker compose \
references/deployment-workflow.md
- Dangerous shell operationline 296
ssh -i <keyfile> ubuntu@<public-ip> 'stack=$(sudo sed -n "s/^stack_name=//p" /var/dirextalk-message-server/split/.manifest); sudo docker compose --project-name "${stack}-edge" --env-file /var/dirextalk-message-server/edge.env -f /var/dir - Dangerous shell operationline 297
'stack=$(sudo sed -n "s/^stack_name=//p" /var/dirextalk-message-server/split/.manifest); sudo docker compose --project-name "${stack}-edge" --env-file /var/dirextalk-message-server/edge.env -f /var/dirextalk-message-server/deploy/split-agen - Network accessline 307
curl -fsS https://<DOMAIN>/_p2p/health # returns successfully when TLS and the server are ready - Network accessline 329
3. **Force Caddy staging CA** (development only) — Set the environment variable `CADDY_ACME_CA=https://acme-staging-v02.api.letsencrypt.org/directory` - Network accessline 330
variable `CADDY_ACME_CA=https://acme-staging-v02.api.letsencrypt.org/directory` - Access to secretsline 411
[Credential-related source omitted] - Access to secretsline 418
[Credential-related source omitted]
references/runtime-wiring.md
- Access to secretsline 20
[Credential-related source omitted] - Network accessline 22
"agent_room_id": "__ROOM_ID__", "agent_node_id": "__AGENT_NODE_ID__", "mcp_url": "https://__DOMAIN__/mcp" - Network accessline 23
"agent_node_id": "__AGENT_NODE_ID__", "mcp_url": "https://__DOMAIN__/mcp" } - Network accessline 24
"mcp_url": "https://__DOMAIN__/mcp" - Access to secretsline 30
[Credential-related source omitted] - Access to secretsline 92
[Credential-related source omitted] - Access to secretsline 108
[Credential-related source omitted] - Network accessline 134
DIREXTALK_HERMES_ACP_ARGS_TOML=<optional Hermes ACP TOML array> DIREXTALK_CONNECT_NPM_PACKAGE=dirextalk-connect@latest DIREXTALK_CONNECT_REPO=https://github.com/YingSuiAI/dirextalk-connect.git - Network accessline 135
DIREXTALK_CONNECT_NPM_PACKAGE=dirextalk-connect@latest DIREXTALK_CONNECT_REPO=https://github.com/YingSuiAI/dirextalk-connect.git mcp_transport=http - Network accessline 136
DIREXTALK_CONNECT_REPO=https://github.com/YingSuiAI/dirextalk-connect.git - Access to secretsline 140
[Credential-related source omitted] - Access to secretsline 160
[Credential-related source omitted] - Network accessline 186
git clone https://github.com/YingSuiAI/dirextalk-connect.git
references/state-machine.md
- Network accessline 8
- **S1_PREFLIGHT**: 校验 region、Lightsail 套餐和 Lightsail 可用区,然后选择云提供方;不查询 AWS Free Tier 或免费额度使用情况。默认 Lightsail,默认 AZ 是 `<region>a`;如果默认 AZ 不可用则选择同 region 其他可用 Lightsail AZ;如果 Lightsail 当前 region 没有可用套餐或可用区,且用户没有显式强制 Lightsail,则在 S1 记录选择 EC2。EC - Network accessline 9
- **S2_DOMAIN**: 确认正式长期域名和 Matrix `server_name` 不可逆绑定。 - **S3_PROVISION**: 按 S1 记录的 provider 创建资源。fresh deployment 先从 message-server 与 external Agent 的 Docker Hub `latest` 通道发现版本,核对对应稳定 `vX.Y.Z` 标签、source revision 与 linux/amd64 manifest dig - Network accessline 10
- **S3_PROVISION**: 按 S1 记录的 provider 创建资源。fresh deployment 先从 message-server 与 external Agent 的 Docker Hub `latest` 通道发现版本,核对对应稳定 `vX.Y.Z` 标签、source revision 与 linux/amd64 manifest digest,再把两份 application snapshot 原子写入 state;任何 retry/resum - Access to secretsline 12
[Credential-related source omitted]
references/token-refresh.md
- Access to secretsline 3
[Credential-related source omitted] - Access to secretsline 5
[Credential-related source omitted] - Access to secretsline 7
[Credential-related source omitted] - Dangerous shell operationline 9
[Credential-related source omitted] - Access to secretsline 9
[Credential-related source omitted] - Network accessline 18
"owner_user_id": "__OWNER_USER_ID__", "user_id": "__OWNER_USER_ID__", "homeserver": "https://__DOMAIN__", - Network accessline 19
[Credential-related source omitted] - Network accessline 20
"homeserver": "https://__DOMAIN__", - Access to secretsline 21
[Credential-related source omitted] - Dangerous shell operationline 31
ssh -i <key.pem> ubuntu@<ip> 'sudo cat /var/dirextalk-message-server/p2p/bootstrap.json' > bootstrap.json - Access to secretsline 34
[Credential-related source omitted] - Access to secretsline 46
[Credential-related source omitted] - Network accessline 48
"agent_room_id": "__ROOM_ID__", "agent_node_id": "<agent_node_id>", "mcp_url": "https://__DOMAIN__/mcp" - Network accessline 49
"agent_node_id": "<agent_node_id>", "mcp_url": "https://__DOMAIN__/mcp" } - Network accessline 50
"mcp_url": "https://__DOMAIN__/mcp" - Network accessline 87
curl -fsS https://<domain>/_p2p/health && echo OK - Network accessline 88
curl -sk https://<domain>/.well-known/portal/owner.json - Network accessline 89
curl -sk https://<domain>/_matrix/client/versions
references/tooling.md
- Network accessline 10
bash --version command -v node aws ssh curl command -v dig nslookup getent - Network accessline 11
command -v node aws ssh curl command -v dig nslookup getent node --version - Network accessline 22
version, a `MINGW*` shell, and one shared Git for Windows installation root; otherwise tell the user to install Git for Windows from <https://git-scm.com/download/win>, reopen Git Bash, and stop. Do not substitute - Network accessline 23
otherwise tell the user to install Git for Windows from <https://git-scm.com/download/win>, reopen Git Bash, and stop. Do not substitute PowerShell, MSYS2, or Cygwin. Native WSL is supported as a Linux host: run Bash - Network accessline 24
<https://git-scm.com/download/win>, reopen Git Bash, and stop. Do not substitute - Dangerous shell operationline 72
sudo apt-get update && sudo apt-get install -y nodejs awscli openssh-client curl dnsutils - Network accessline 72
sudo apt-get update && sudo apt-get install -y nodejs awscli openssh-client curl dnsutils - Dangerous shell operationline 73
sudo dnf install -y nodejs awscli openssh-clients curl bind-utils - Network accessline 73
sudo dnf install -y nodejs awscli openssh-clients curl bind-utils - Dangerous shell operationline 74
sudo yum install -y nodejs awscli openssh-clients curl bind-utils - Network accessline 74
sudo yum install -y nodejs awscli openssh-clients curl bind-utils - Dangerous shell operationline 75
sudo pacman -Sy --needed nodejs aws-cli openssh curl bind-tools - Network accessline 75
sudo pacman -Sy --needed nodejs aws-cli openssh curl bind-tools - Dangerous shell operationline 76
sudo zypper install -y nodejs aws-cli openssh-clients curl bind-utils - Network accessline 76
sudo zypper install -y nodejs aws-cli openssh-clients curl bind-utils
references/troubleshooting.md
- Network accessline 18
curl -k https://<domain>/_matrix/client/versions
references/user-journey.md
- Network accessline 34
If the Git Bash preflight fails, install Git for Windows from <https://git-scm.com/download/win>, reopen Git Bash, and stop. Do not use - Network accessline 35
<https://git-scm.com/download/win>, reopen Git Bash, and stop. Do not use - Access to secretsline 69
[Credential-related source omitted]
references/verification-recovery.md
- Network accessline 36
curl -fsS https://<DOMAIN>/_p2p/health - Network accessline 37
curl -fsS https://<DOMAIN>/_matrix/client/versions - Network accessline 38
curl -fsS https://<DOMAIN>/.well-known/matrix/server - Network accessline 39
curl -fsS https://<DOMAIN>/.well-known/portal/owner.json - Network accessline 45
curl --resolve <DOMAIN>:443:<PUBLIC_IP> -fsS https://<DOMAIN>/_p2p/health - Network accessline 113
Agent secret volume as UID/GID 65532 mode 0400. Agent YAML contains only `core_message_mcp_enabled: true`, the internal `http://message-server:8008/mcp` endpoint, and - Network accessline 114
`core_message_mcp_enabled: true`, the internal `http://message-server:8008/mcp` endpoint, and `/run/secrets/message_mcp_token`; the bearer value must not appear in YAML, - Network accessline 115
`http://message-server:8008/mcp` endpoint, and - Dangerous shell operationline 126
sudo /var/dirextalk-message-server/production-ops/reconcile-production.sh - Dangerous shell operationline 178
sudo systemctl show dirextalk-split-recovery.service \ - Dangerous shell operationline 183
`sudo /var/dirextalk-message-server/production-ops/recover-production.sh` and
references/voip-turn-runbook.md
- Dangerous shell operationline 39
[Credential-related source omitted] - Access to secretsline 39
[Credential-related source omitted] - Access to secretsline 40
[Credential-related source omitted] - Dangerous shell operationline 43
[Credential-related source omitted] - Access to secretsline 43
[Credential-related source omitted] - Access to secretsline 44
[Credential-related source omitted]
references/windows-deployment-notes.md
- Network accessline 19
If the preflight fails, install Git for Windows from <https://git-scm.com/download/win>, reopen Git Bash, and stop. The preflight - Network accessline 20
<https://git-scm.com/download/win>, reopen Git Bash, and stop. The preflight - Network accessline 27
Path conversion at native-tool boundaries is explicit. The deployer converts Node script/input paths, AWS CLI `file://` paths, curl output/header paths, and - Network accessline 28
Node script/input paths, AWS CLI `file://` paths, curl output/header paths, and - Network accessline 81
curl --resolve __DOMAIN__:443:__EIP__ -fsS https://__DOMAIN__/_p2p/health - Access to secretsline 91
[Credential-related source omitted] - Network accessline 191
curl -sk https://<domain>/_matrix/client/versions
scripts/aws-credentials.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 25
[Credential-related source omitted] - Access to secretsline 29
[Credential-related source omitted] - Access to secretsline 95
[Credential-related source omitted] - Access to secretsline 99
[Credential-related source omitted] - Access to secretsline 137
[Credential-related source omitted] - Access to secretsline 138
[Credential-related source omitted] - Access to secretsline 139
[Credential-related source omitted] - Access to secretsline 152
[Credential-related source omitted] - Access to secretsline 179
[Credential-related source omitted] - Access to secretsline 181
[Credential-related source omitted]
scripts/cloud-init/split/.npmignore
- Executable scriptline 1
Executable file
scripts/cloud-init/split/Caddyfile
- Executable scriptline 1
Executable file - Network accessline 8
header Content-Type application/json header Access-Control-Allow-Origin * respond `{"m.homeserver":{"base_url":"https://__DIREXTALK_PUBLIC_DOMAIN__"}}` 200 - Network accessline 9
header Access-Control-Allow-Origin * respond `{"m.homeserver":{"base_url":"https://__DIREXTALK_PUBLIC_DOMAIN__"}}` 200 } - Network accessline 10
respond `{"m.homeserver":{"base_url":"https://__DIREXTALK_PUBLIC_DOMAIN__"}}` 200
scripts/cloud-init/split/advance-split-source-revision.sh
scripts/cloud-init/split/apply-host-integration.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 42
[Credential-related source omitted] - Access to secretsline 101
[Credential-related source omitted] - Dangerous shell operationline 145
rm -f -- "$host_region_receipt" || status=1 - Dangerous shell operationline 149
rm -rf -- "$base/updater" - Dangerous shell operationline 153
rm -rf -- "$base/production-ops" - Dangerous shell operationline 157
rm -rf -- "$base/deploy/split-agent" - Dangerous shell operationline 167
rm -f -- "$recovery_service" || status=1 - Dangerous shell operationline 174
rm -rf -- "$transaction" - Access to secretsline 344
[Credential-related source omitted] - Access to secretsline 345
[Credential-related source omitted]
scripts/cloud-init/split/authorize-split-source-revision.sh
scripts/cloud-init/split/bootstrap-production.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 12
[Credential-related source omitted] - Access to secretsline 60
[Credential-related source omitted] - Access to secretsline 100
[Credential-related source omitted] - Access to secretsline 106
[Credential-related source omitted] - Access to secretsline 108
[Credential-related source omitted] - Access to secretsline 118
[Credential-related source omitted] - Access to secretsline 119
[Credential-related source omitted] - Access to secretsline 121
[Credential-related source omitted] - Dangerous shell operationline 163
rm -f -- "$preparation" || { - Dangerous shell operationline 171
rm -rf -- "$run_dir" || { - Access to secretsline 198
[Credential-related source omitted] - Access to secretsline 237
[Credential-related source omitted] - Access to secretsline 238
[Credential-related source omitted] - Access to secretsline 240
[Credential-related source omitted] - Access to secretsline 241
[Credential-related source omitted] - Access to secretsline 242
[Credential-related source omitted] - Access to secretsline 243
[Credential-related source omitted] - Access to secretsline 244
[Credential-related source omitted] - Access to secretsline 245
[Credential-related source omitted] - Network accessline 252
agent_revision=$(read_env AGENT_SOURCE_REVISION) fi [ "$release_catalog_origin" = https://imadmin.dirextalk.ai ] \ - Network accessline 253
fi [ "$release_catalog_origin" = https://imadmin.dirextalk.ai ] \ || { echo "protected release catalog origin is invalid" >&2; exit 1; } - Network accessline 254
[ "$release_catalog_origin" = https://imadmin.dirextalk.ai ] \ - Access to secretsline 398
[Credential-related source omitted] - Access to secretsline 424
[Credential-related source omitted] - Access to secretsline 443
[Credential-related source omitted] - Access to secretsline 445
[Credential-related source omitted] - Access to secretsline 458
[Credential-related source omitted] - Dangerous shell operationline 463
cleanup_caddy_tmp() { rm -f -- "$caddy_tmp"; } - Dangerous shell operationline 469
rm -f -- "$caddy_tmp" - Dangerous shell operationline 513
rm -f "$refresh_dir/bootstrap.json"
scripts/cloud-init/split/migrate-message-mcp-token-binding.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/cloud-init/split/production-ops-common.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 33
[Credential-related source omitted] - Access to secretsline 46
[Credential-related source omitted] - Access to secretsline 63
[Credential-related source omitted] - Access to secretsline 79
[Credential-related source omitted] - Access to secretsline 86
[Credential-related source omitted] - Possible obfuscationline 100
[Credential-related source omitted] - Access to secretsline 100
[Credential-related source omitted] - Access to secretsline 101
[Credential-related source omitted] - Access to secretsline 104
[Credential-related source omitted] - Access to secretsline 107
[Credential-related source omitted] - Access to secretsline 149
[Credential-related source omitted] - Access to secretsline 151
[Credential-related source omitted] - Dangerous shell operationline 154
[ "$(stat -c '%d:%i:%u:%g:%a' -- "$token_file" 2>/dev/null || true)" = "$candidate_token_identity" ] && rm -f -- "$token_file" || rollback_status=1 - Dangerous shell operationline 155
&& rm -f -- "$token_file" || rollback_status=1 - Dangerous shell operationline 160
[Credential-related source omitted] - Access to secretsline 160
[Credential-related source omitted] - Access to secretsline 172
[Credential-related source omitted] - Access to secretsline 173
[Credential-related source omitted] - Access to secretsline 182
[Credential-related source omitted] - Access to secretsline 183
[Credential-related source omitted] - Access to secretsline 184
[Credential-related source omitted] - Access to secretsline 203
[Credential-related source omitted] - Access to secretsline 206
[Credential-related source omitted] - Access to secretsline 217
[Credential-related source omitted] - Access to secretsline 221
[Credential-related source omitted] - Access to secretsline 223
[Credential-related source omitted] - Access to secretsline 227
[Credential-related source omitted] - Access to secretsline 228
[Credential-related source omitted] - Access to secretsline 231
[Credential-related source omitted] - Access to secretsline 243
[Credential-related source omitted] - Possible obfuscationline 246
[Credential-related source omitted] - Access to secretsline 246
[Credential-related source omitted] - Access to secretsline 248
[Credential-related source omitted] - Possible obfuscationline 262
[Credential-related source omitted] - Access to secretsline 262
[Credential-related source omitted] - Access to secretsline 264
[Credential-related source omitted] - Access to secretsline 293
[Credential-related source omitted] - Access to secretsline 300
[Credential-related source omitted] - Access to secretsline 312
[Credential-related source omitted] - Access to secretsline 348
[Credential-related source omitted]
scripts/cloud-init/split/reconcile-production.sh
scripts/cloud-init/split/recover-production.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/cloud-init/split/release.env
- Network accessline 1
DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai
scripts/cloud-init/split/reset-production.sh
scripts/cloud-init/split/runtime/.gitignore
- Executable scriptline 1
Executable file
scripts/cloud-init/split/runtime/apparmor.d/dirextalk-runner-userns
- Executable scriptline 1
Executable file
scripts/cloud-init/split/runtime/compose.yaml
- Network accessline 102
x-message-capability-environment: &message-capability-environment P2P_PLUGIN_DOCKER_ENABLED: "false" P2P_PLUGIN_BACKEND_BASE_URL: http://message-server:8008 - Network accessline 103
P2P_PLUGIN_DOCKER_ENABLED: "false" P2P_PLUGIN_BACKEND_BASE_URL: http://message-server:8008 P2P_AGENT_VERSION_URL: http://agent:8082/agent/v1/health - Network accessline 104
P2P_PLUGIN_BACKEND_BASE_URL: http://message-server:8008 - Network accessline 105
P2P_AGENT_VERSION_URL: http://agent:8082/agent/v1/health - Network accessline 106
P2P_AGENT_VOICE_CALLBACK_URL: ${DIREXTALK_AGENT_VOICE_CALLBACK_URL:-https://agent:8444} - Network accessline 543
condition: service_completed_successfully healthcheck: test: ["CMD", "wget", "-Y", "off", "-q", "-O", "-", "http://127.0.0.1:8008/_p2p/health"] - Network accessline 544
healthcheck: test: ["CMD", "wget", "-Y", "off", "-q", "-O", "-", "http://127.0.0.1:8008/_p2p/health"] interval: 10s - Network accessline 545
test: ["CMD", "wget", "-Y", "off", "-q", "-O", "-", "http://127.0.0.1:8008/_p2p/health"]
scripts/cloud-init/split/runtime/edge-compose.yaml
- Network accessline 45
- message_public healthcheck: test: ["CMD-SHELL", "wget -Y off -q -O - http://127.0.0.1:2019/config/ >/dev/null 2>&1"] - Network accessline 46
healthcheck: test: ["CMD-SHELL", "wget -Y off -q -O - http://127.0.0.1:2019/config/ >/dev/null 2>&1"] interval: 5s - Network accessline 47
test: ["CMD-SHELL", "wget -Y off -q -O - http://127.0.0.1:2019/config/ >/dev/null 2>&1"]
scripts/cloud-init/split/runtime/scripts/agent-runtime-local-common.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 55
[Credential-related source omitted] - Dangerous shell operationline 184
rm -f -- "$preparation_tmp" - Dangerous shell operationline 188
rm -f -- "$preparation_tmp" - Dangerous shell operationline 192
rm -f -- "$preparation_tmp" - Access to secretsline 377
[Credential-related source omitted] - Access to secretsline 380
[Credential-related source omitted] - Access to secretsline 389
[Credential-related source omitted] - Access to secretsline 398
[Credential-related source omitted] - Access to secretsline 400
[Credential-related source omitted] - Access to secretsline 420
[Credential-related source omitted] - Access to secretsline 421
[Credential-related source omitted]
scripts/cloud-init/split/runtime/scripts/cleanup-local.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 33
[Credential-related source omitted] - Access to secretsline 36
[Credential-related source omitted] - Network accessline 60
die "$tls_mode manifest server-name validation infrastructure failure (grep status $status)" fi [ "$client_base_url" = "https://$server_name" ] || die "$tls_mode manifest client URL is not bound to its server name" - Network accessline 61
fi [ "$client_base_url" = "https://$server_name" ] || die "$tls_mode manifest client URL is not bound to its server name" } - Network accessline 62
[ "$client_base_url" = "https://$server_name" ] || die "$tls_mode manifest client URL is not bound to its server name" - Access to secretsline 121
[Credential-related source omitted] - Access to secretsline 123
[Credential-related source omitted] - Access to secretsline 135
[Credential-related source omitted] - Access to secretsline 136
[Credential-related source omitted] - Access to secretsline 137
[Credential-related source omitted] - Access to secretsline 138
[Credential-related source omitted] - Access to secretsline 139
[Credential-related source omitted] - Access to secretsline 140
[Credential-related source omitted] - Access to secretsline 141
[Credential-related source omitted] - Access to secretsline 142
[Credential-related source omitted] - Access to secretsline 143
[Credential-related source omitted] - Access to secretsline 144
[Credential-related source omitted] - Access to secretsline 145
[Credential-related source omitted] - Access to secretsline 146
[Credential-related source omitted] - Access to secretsline 147
[Credential-related source omitted] - Access to secretsline 148
[Credential-related source omitted] - Access to secretsline 185
[Credential-related source omitted] - Access to secretsline 188
[Credential-related source omitted] - Access to secretsline 189
[Credential-related source omitted] - Access to secretsline 190
[Credential-related source omitted] - Access to secretsline 193
[Credential-related source omitted] - Dangerous shell operationline 335
rm -f -- "$inspection_error_file" - Access to secretsline 344
[Credential-related source omitted] - Access to secretsline 346
[Credential-related source omitted] - Dangerous shell operationline 599
docker container rm -f "${container_ids[index]}" >/dev/null || die "exact container removal failed: ${container_names[index]}" - Dangerous shell operationline 635
docker network rm "${network_ids[index]}" >/dev/null || die "exact network removal failed: ${network_receipt_names[index]}" - Dangerous shell operationline 644
docker volume rm "${volume_names[index]}" >/dev/null || die "exact volume purge failed: ${volume_names[index]}"
scripts/cloud-init/split/runtime/scripts/cleanup-provision-failure.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 23
[Credential-related source omitted] - Access to secretsline 25
[Credential-related source omitted] - Access to secretsline 30
[Credential-related source omitted] - Access to secretsline 32
[Credential-related source omitted] - Access to secretsline 36
[Credential-related source omitted] - Access to secretsline 38
[Credential-related source omitted] - Access to secretsline 71
[Credential-related source omitted] - Access to secretsline 72
[Credential-related source omitted] - Access to secretsline 73
[Credential-related source omitted] - Access to secretsline 74
[Credential-related source omitted] - Access to secretsline 75
[Credential-related source omitted] - Access to secretsline 76
[Credential-related source omitted] - Access to secretsline 77
[Credential-related source omitted] - Access to secretsline 98
[Credential-related source omitted] - Access to secretsline 99
[Credential-related source omitted] - Access to secretsline 100
[Credential-related source omitted] - Access to secretsline 101
[Credential-related source omitted] - Access to secretsline 102
[Credential-related source omitted] - Access to secretsline 103
[Credential-related source omitted] - Access to secretsline 104
[Credential-related source omitted] - Access to secretsline 105
[Credential-related source omitted] - Access to secretsline 110
[Credential-related source omitted] - Access to secretsline 111
[Credential-related source omitted] - Access to secretsline 112
[Credential-related source omitted] - Access to secretsline 114
[Credential-related source omitted] - Access to secretsline 115
[Credential-related source omitted] - Access to secretsline 116
[Credential-related source omitted] - Access to secretsline 117
[Credential-related source omitted] - Access to secretsline 135
[Credential-related source omitted] - Access to secretsline 136
[Credential-related source omitted] - Dangerous shell operationline 190
rm -f -- "$err" - Dangerous shell operationline 199
rm -f -- "$err" - Dangerous shell operationline 205
rm -f -- "$err" - Dangerous shell operationline 213
rm -f -- "$err"
scripts/cloud-init/split/runtime/scripts/ensure-host-null-device.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/cloud-init/split/runtime/scripts/export-portal-bootstrap.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 26
[Credential-related source omitted] - Access to secretsline 28
[Credential-related source omitted] - Access to secretsline 41
[Credential-related source omitted] - Access to secretsline 42
[Credential-related source omitted] - Dangerous shell operationline 58
rm -f "$tmp_file" - Access to secretsline 63
[Credential-related source omitted] - Access to secretsline 70
[Credential-related source omitted]
scripts/cloud-init/split/runtime/scripts/initialize-capability-ca.sh
scripts/cloud-init/split/runtime/scripts/initialize-message-server.sh
- Executable scriptline 1
#!/bin/sh - Dangerous shell operationline 29
rm -f "$config_dir/server.crt" "$config_dir/server.key" - Access to secretsline 39
[Credential-related source omitted] - Access to secretsline 61
[Credential-related source omitted] - Access to secretsline 76
[Credential-related source omitted] - Access to secretsline 77
[Credential-related source omitted]
scripts/cloud-init/split/runtime/scripts/initialize-postgres.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/cloud-init/split/runtime/scripts/manage-runner-apparmor.sh
scripts/cloud-init/split/runtime/scripts/materialize-agent-secrets.sh
- Executable scriptline 1
#!/bin/sh
scripts/cloud-init/split/runtime/scripts/message-server-entrypoint.sh
- Executable scriptline 1
#!/bin/sh
scripts/cloud-init/split/runtime/scripts/postgres-entrypoint.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/cloud-init/split/runtime/scripts/prepare-agent-start-local.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/cloud-init/split/runtime/scripts/prepare-host-dependencies.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/cloud-init/split/runtime/scripts/prepare-runner-cgroups.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 189
for command_name in awk cat chmod chown cmp cp docker getent grep id install ln mktemp readlink rm sha256sum sleep stat tee tr - Dangerous shell operationline 190
awk cat chmod chown cmp cp docker getent grep id install ln mktemp readlink rm sha256sum sleep stat tee tr \ - Dangerous shell operationline 371
rm -f -- "$tmp" - Dangerous shell operationline 377
rm -f -- "$tmp" - Dangerous shell operationline 382
rm -f -- "$tmp"
scripts/cloud-init/split/runtime/scripts/provision-local.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 276
[ "$core_extension_enabled" = true ] || die "production requires DIREXTALK_CORE_EXTENSION_ENABLED=true" [ "$core_workload_enabled" = true ] || die "production requires DIREXTALK_CORE_WORKLOAD_ENABLED=true" release_catalog_origin=https://ima - Network accessline 277
[ "$core_workload_enabled" = true ] || die "production requires DIREXTALK_CORE_WORKLOAD_ENABLED=true" release_catalog_origin=https://imadmin.dirextalk.ai if [ "$runner_fixture_mode" = true ] && [ "${DIREXTALK_SPLIT_TEST_MODE:-false}" != tru - Network accessline 278
release_catalog_origin=https://imadmin.dirextalk.ai - Network accessline 289
[ -n "$message_server_name" ] || die "DIREXTALK_MESSAGE_SERVER_NAME is required" validate_server_name DIREXTALK_MESSAGE_SERVER_NAME "$message_server_name" message_client_base_url=https://$message_server_name - Network accessline 290
validate_server_name DIREXTALK_MESSAGE_SERVER_NAME "$message_server_name" message_client_base_url=https://$message_server_name [ -z "${DIREXTALK_MESSAGE_TLS_CERT_SOURCE_FILE:-}" ] || \ - Network accessline 291
message_client_base_url=https://$message_server_name - Network accessline 296
if [ -n "${DIREXTALK_MESSAGE_CLIENT_BASE_URL:-}" ]; then validate_safe_value DIREXTALK_MESSAGE_CLIENT_BASE_URL "$DIREXTALK_MESSAGE_CLIENT_BASE_URL" '^https?://[A-Za-z0-9._:-]+$' [ "$DIREXTALK_MESSAGE_CLIENT_BASE_URL" = "$message_client_ - Network accessline 297
validate_safe_value DIREXTALK_MESSAGE_CLIENT_BASE_URL "$DIREXTALK_MESSAGE_CLIENT_BASE_URL" '^https?://[A-Za-z0-9._:-]+$' [ "$DIREXTALK_MESSAGE_CLIENT_BASE_URL" = "$message_client_base_url" ] || \ die "DIREXTALK_MESSAGE_CLIENT_BASE_URL - Network accessline 298
[ "$DIREXTALK_MESSAGE_CLIENT_BASE_URL" = "$message_client_base_url" ] || \ - Network accessline 299
die "DIREXTALK_MESSAGE_CLIENT_BASE_URL must be derived from DIREXTALK_MESSAGE_HTTP_BIND ($message_client_base_url)" - Access to secretsline 869
[Credential-related source omitted] - Access to secretsline 870
[Credential-related source omitted] - Access to secretsline 881
[Credential-related source omitted] - Network accessline 934
core_extension_runner_uid: $extension_runner_uid core_message_mcp_enabled: true core_message_mcp_endpoint: http://message-server:8008/mcp - Network accessline 935
core_message_mcp_enabled: true core_message_mcp_endpoint: http://message-server:8008/mcp core_message_mcp_token_file: /run/secrets/message_mcp_token - Network accessline 936
core_message_mcp_endpoint: http://message-server:8008/mcp - Network accessline 938
core_static_sites_enabled: true core_static_sites_root: /var/lib/dirextalk-agent/static-sites core_static_sites_public_origin: $message_client_base_url - Network accessline 939
core_static_sites_root: /var/lib/dirextalk-agent/static-sites core_static_sites_public_origin: $message_client_base_url core_workload_enabled: $core_workload_enabled - Network accessline 940
core_static_sites_public_origin: $message_client_base_url - Access to secretsline 961
[Credential-related source omitted] - Network accessline 980
DIREXTALK_AGENT_INSTANCE_ID=$agent_instance_id DIREXTALK_ACCOUNT_GENERATION=$account_generation DIREXTALK_RELEASE_CATALOG_ORIGIN=$release_catalog_origin - Network accessline 981
DIREXTALK_ACCOUNT_GENERATION=$account_generation DIREXTALK_RELEASE_CATALOG_ORIGIN=$release_catalog_origin DIREXTALK_AGENT_TLS_SERVER_NAME=dirextalk-agent - Network accessline 982
DIREXTALK_RELEASE_CATALOG_ORIGIN=$release_catalog_origin - Network accessline 983
DIREXTALK_AGENT_TLS_SERVER_NAME=dirextalk-agent DIREXTALK_MESSAGE_SERVER_NAME=$message_server_name DIREXTALK_MESSAGE_CLIENT_BASE_URL=$message_client_base_url - Network accessline 984
DIREXTALK_MESSAGE_SERVER_NAME=$message_server_name DIREXTALK_MESSAGE_CLIENT_BASE_URL=$message_client_base_url DIREXTALK_MESSAGE_TLS_MODE=$message_tls_mode - Network accessline 985
DIREXTALK_MESSAGE_CLIENT_BASE_URL=$message_client_base_url - Access to secretsline 1068
[Credential-related source omitted] - Access to secretsline 1077
[Credential-related source omitted] - Network accessline 1091
core_secret_master_key_uid=$core_secret_master_key_uid message_http_bind=$message_http_bind message_client_base_url=$message_client_base_url - Network accessline 1092
message_http_bind=$message_http_bind message_client_base_url=$message_client_base_url message_tls_mode=$message_tls_mode - Network accessline 1093
message_client_base_url=$message_client_base_url
scripts/cloud-init/split/runtime/scripts/recover-starting-cleanup-receipt.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 13
[Credential-related source omitted] - Access to secretsline 16
[Credential-related source omitted] - Access to secretsline 48
[Credential-related source omitted] - Access to secretsline 50
[Credential-related source omitted] - Access to secretsline 93
[Credential-related source omitted] - Access to secretsline 95
[Credential-related source omitted] - Dangerous shell operationline 133
cleanup_tmp() { rm -f -- "$inspect_error" ${tmp_receipt:+"$tmp_receipt"}; }
scripts/cloud-init/split/runtime/scripts/refresh-message-mcp-token.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 30
[Credential-related source omitted] - Access to secretsline 49
[Credential-related source omitted] - Access to secretsline 56
[Credential-related source omitted] - Access to secretsline 60
[Credential-related source omitted] - Access to secretsline 62
[Credential-related source omitted] - Access to secretsline 63
[Credential-related source omitted] - Access to secretsline 66
[Credential-related source omitted] - Access to secretsline 67
[Credential-related source omitted] - Access to secretsline 73
[Credential-related source omitted] - Access to secretsline 74
[Credential-related source omitted] - Access to secretsline 76
[Credential-related source omitted] - Access to secretsline 77
[Credential-related source omitted] - Dangerous shell operationline 113
rm -f -- "$bootstrap_tmp" - Dangerous shell operationline 117
[ -z "${bootstrap_tmp:-}" ] || rm -f -- "$bootstrap_tmp" - Dangerous shell operationline 118
[ -z "${token_tmp:-}" ] || rm -f -- "$token_tmp"
scripts/cloud-init/split/runtime/scripts/restart-agent-local.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/cloud-init/split/runtime/scripts/start-local.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 39
[Credential-related source omitted] - Access to secretsline 41
[Credential-related source omitted] - Access to secretsline 43
[Credential-related source omitted] - Access to secretsline 45
[Credential-related source omitted] - Access to secretsline 78
[Credential-related source omitted] - Access to secretsline 79
[Credential-related source omitted] - Access to secretsline 80
[Credential-related source omitted] - Access to secretsline 81
[Credential-related source omitted] - Access to secretsline 82
[Credential-related source omitted] - Access to secretsline 83
[Credential-related source omitted] - Access to secretsline 86
[Credential-related source omitted] - Access to secretsline 87
[Credential-related source omitted] - Access to secretsline 88
[Credential-related source omitted] - Access to secretsline 89
[Credential-related source omitted] - Access to secretsline 109
[Credential-related source omitted] - Access to secretsline 110
[Credential-related source omitted] - Access to secretsline 111
[Credential-related source omitted] - Access to secretsline 112
[Credential-related source omitted] - Access to secretsline 113
[Credential-related source omitted] - Access to secretsline 114
[Credential-related source omitted] - Access to secretsline 115
[Credential-related source omitted] - Access to secretsline 116
[Credential-related source omitted] - Access to secretsline 154
[Credential-related source omitted] - Access to secretsline 157
[Credential-related source omitted] - Access to secretsline 158
[Credential-related source omitted] - Access to secretsline 159
[Credential-related source omitted] - Access to secretsline 162
[Credential-related source omitted] - Access to secretsline 550
[Credential-related source omitted] - Dangerous shell operationline 606
} >"$tmp" || { rm -f -- "$tmp"; die "cannot write cleanup journal"; } - Dangerous shell operationline 607
chmod 400 -- "$tmp" || { rm -f -- "$tmp"; die "cannot protect cleanup journal"; } - Dangerous shell operationline 609
rm -f -- "$tmp" - Dangerous shell operationline 612
rm -f -- "$tmp" - Dangerous shell operationline 722
rm -f -- "$tmp" - Dangerous shell operationline 725
chmod 400 -- "$tmp" || { rm -f -- "$tmp"; return 1; } - Dangerous shell operationline 726
[ "$(stat -c '%d:%i:%u' "$receipt")" = "$journal_identity" ] || { rm -f -- "$tmp"; return 1; } - Dangerous shell operationline 727
mv -- "$tmp" "$receipt" || { rm -f -- "$tmp"; return 1; } - Dangerous shell operationline 1007
rm -f -- "$tmp" - Dangerous shell operationline 1010
chmod 400 -- "$tmp" || { rm -f -- "$tmp"; die "cannot protect cleanup receipt"; } - Dangerous shell operationline 1012
rm -f -- "$tmp"
scripts/cloud-init/split/runtime/scripts/stop-agent-local.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/cloud-init/split/runtime/scripts/update-agent-local.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 25
[Credential-related source omitted] - Access to secretsline 40
[Credential-related source omitted] - Access to secretsline 41
[Credential-related source omitted] - Access to secretsline 48
[Credential-related source omitted] - Access to secretsline 50
[Credential-related source omitted] - Dangerous shell operationline 239
cleanup_repair() { local status=$?; [ -z "$repair_env" ] || rm -f -- "$repair_env"; [ -z "$repair_receipt" ] || rm -f -- "$repair_receipt"; return "$status"; } - Access to secretsline 248
[Credential-related source omitted] - Dangerous shell operationline 306
rm -rf -- "$config_transaction" - Dangerous shell operationline 344
rm -rf -- "$config_transaction" - Dangerous shell operationline 397
rm -rf -- "$config_stage" - Dangerous shell operationline 500
rm -rf -- "$config_transaction" || return 1 - Access to secretsline 567
[Credential-related source omitted] - Dangerous shell operationline 577
rm -rf -- "$config_transaction" - Dangerous shell operationline 584
if [ "$old_image_id" != "$target_image_id" ] && ! docker ps -aq --filter "ancestor=$old_image_id" | grep -q .; then docker image rm "$old_image_id" >/dev/null 2>&1 || true; fi
scripts/cloud-init/split/runtime/scripts/update-message-server-local.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 32
[Credential-related source omitted] - Access to secretsline 44
[Credential-related source omitted] - Access to secretsline 45
[Credential-related source omitted] - Access to secretsline 80
[Credential-related source omitted] - Access to secretsline 132
[Credential-related source omitted] - Access to secretsline 143
[Credential-related source omitted] - Dangerous shell operationline 147
if [ "$old_image_id" != "$target_image_id" ] && ! docker ps -aq --filter "ancestor=$old_image_id" | grep -q .; then docker image rm "$old_image_id" >/dev/null 2>&1 || true; fi
scripts/cloud-init/split/runtime/scripts/verify-production-images.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/cloud-init/user-data.yaml
- Access to secretsline 11
[Credential-related source omitted] - Network accessline 19
- | if ! command -v docker >/dev/null 2>&1; then curl -fsSL https://get.docker.com | sh - Network accessline 20
if ! command -v docker >/dev/null 2>&1; then curl -fsSL https://get.docker.com | sh fi - Dangerous shell operationline 21
curl -fsSL https://get.docker.com | sh - Network accessline 21
curl -fsSL https://get.docker.com | sh
scripts/destroy.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 333
change_file_aws=$(dirextalk_native_tool_path "$change_file") || { rm -f "$change_file"; return 1; } - Dangerous shell operationline 339
rm -f "$change_file" - Dangerous shell operationline 503
cleanup_desired_helper() { rm -f "$desired_helper_tmp"; } - Dangerous shell operationline 506
sudo install -d -m 0755 /var/dirextalk-message-server/updater - Dangerous shell operationline 507
sudo install -m 0755 "$desired_helper_tmp" /var/dirextalk-message-server/updater/set-desired-state.sh - Dangerous shell operationline 508
rm -f "$desired_helper_tmp" - Dangerous shell operationline 510
sudo /var/dirextalk-message-server/updater/set-desired-state.sh deprovisioned - Dangerous shell operationline 515
if ssh -T -i "$key_file" -o StrictHostKeyChecking=accept-new -o ConnectTimeout=5 ubuntu@"$public_ip" "sudo bash -lc $remote_q" >/dev/null 2>&1; then - Dangerous shell operationline 516
ubuntu@"$public_ip" "sudo bash -lc $remote_q" >/dev/null 2>&1; then - Dangerous shell operationline 560
rm -rf -- "$src_real" - Access to secretsline 564
[Credential-related source omitted] - Dangerous shell operationline 635
[ -n "${KEY_FILE:-}" ] && [ -f "$KEY_FILE" ] && rm -f "$KEY_FILE" - Dangerous shell operationline 678
[ -n "${KEY_FILE:-}" ] && [ -f "$KEY_FILE" ] && rm -f "$KEY_FILE"
scripts/json.mjs
- Executable scriptline 1
#!/usr/bin/env node - Access to secretsline 235
[Credential-related source omitted] - Access to secretsline 255
[Credential-related source omitted] - Access to secretsline 256
[Credential-related source omitted] - Access to secretsline 436
[Credential-related source omitted] - Access to secretsline 450
[Credential-related source omitted] - Access to secretsline 473
[Credential-related source omitted] - Access to secretsline 548
[Credential-related source omitted] - Network accessline 1004
function normalizeBootstrap(file, domain) { const src = readJsonFile(file); const asUrl = `https://${domain}`; - Network accessline 1005
const src = readJsonFile(file); const asUrl = `https://${domain}`; return { - Network accessline 1006
const asUrl = `https://${domain}`; - Access to secretsline 1014
[Credential-related source omitted]
scripts/lib/atomic-write.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 23
rm -f "$temporary" 2>/dev/null || true - Dangerous shell operationline 27
rm -f "$temporary" 2>/dev/null || true - Dangerous shell operationline 31
rm -f "$temporary" 2>/dev/null || true - Dangerous shell operationline 35
rm -f "$temporary" 2>/dev/null || true
scripts/lib/aws.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/lib/connect-agent-adapters.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 63
[Credential-related source omitted] - Dangerous shell operationline 164
rm -rf "$dist_dir" 2>/dev/null || true - Network accessline 177
if [ ! -f "$dist_dir/node.exe" ]; then warn "Cursor Agent CLI is installed but dist-package/node.exe is missing." warn "Reinstall with: irm 'https://cursor.com/install?win32=true' | iex" - Network accessline 178
warn "Cursor Agent CLI is installed but dist-package/node.exe is missing." warn "Reinstall with: irm 'https://cursor.com/install?win32=true' | iex" return 1 - Network accessline 179
warn "Reinstall with: irm 'https://cursor.com/install?win32=true' | iex"
scripts/lib/connect-daemon-logs.sh
- Executable scriptline 1
Executable file
scripts/lib/domain.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/lib/git-bash.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 39
case "$(uname -s 2>/dev/null || printf unknown)" in *MSYS*|*CYGWIN*) printf '%s\n' "Dirextalk on Windows uses Git Bash only. Install Git for Windows from https://git-scm.com/download/win, open Git Bash, and rerun this command." >& - Network accessline 40
*MSYS*|*CYGWIN*) printf '%s\n' "Dirextalk on Windows uses Git Bash only. Install Git for Windows from https://git-scm.com/download/win, open Git Bash, and rerun this command." >&2 return 1 - Network accessline 41
printf '%s\n' "Dirextalk on Windows uses Git Bash only. Install Git for Windows from https://git-scm.com/download/win, open Git Bash, and rerun this command." >&2 - Network accessline 44
*MINGW*) if ! dirextalk_git_bash_tools_available; then printf '%s\n' "Git for Windows is required for Dirextalk on Windows. Install it from https://git-scm.com/download/win, open Git Bash, and rerun this command." >&2 - Network accessline 45
if ! dirextalk_git_bash_tools_available; then printf '%s\n' "Git for Windows is required for Dirextalk on Windows. Install it from https://git-scm.com/download/win, open Git Bash, and rerun this command." >&2 return 1 - Network accessline 46
printf '%s\n' "Git for Windows is required for Dirextalk on Windows. Install it from https://git-scm.com/download/win, open Git Bash, and rerun this command." >&2
scripts/lib/http-secrets.sh
scripts/lib/json-worker.mjs
- Executable scriptline 1
#!/usr/bin/env node
scripts/lib/json.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 80
json_worker_disconnect || return 1 fi socket_path="/dev/tcp/127.0.0.1/${DIREXTALK_JSON_WORKER_PORT}" - Network accessline 81
fi socket_path="/dev/tcp/127.0.0.1/${DIREXTALK_JSON_WORKER_PORT}" candidate=10 - Dangerous shell operationline 82
socket_path="/dev/tcp/127.0.0.1/${DIREXTALK_JSON_WORKER_PORT}" - Network accessline 82
socket_path="/dev/tcp/127.0.0.1/${DIREXTALK_JSON_WORKER_PORT}" - Network accessline 87
continue fi if eval "exec $candidate<>\"\$socket_path\""; then - Network accessline 88
fi if eval "exec $candidate<>\"\$socket_path\""; then DIREXTALK_JSON_WORKER_SOCKET=$candidate - Dangerous shell operationline 89
if eval "exec $candidate<>\"\$socket_path\""; then - Network accessline 89
if eval "exec $candidate<>\"\$socket_path\""; then - Access to secretsline 122
[Credential-related source omitted] - Access to secretsline 123
[Credential-related source omitted] - Access to secretsline 141
[Credential-related source omitted] - Access to secretsline 143
[Credential-related source omitted] - Access to secretsline 241
[Credential-related source omitted] - Access to secretsline 243
[Credential-related source omitted]
scripts/lib/local-paths.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/lib/mcp-client-adapters.sh
- Executable scriptline 1
Executable file - Network accessline 177
_mcp_doctor_command() { local service_url=$1 credentials_file=${2:-} node_id=${3:-} service_dir=${4:-} local domain=${service_url#https://} - Network accessline 178
local service_url=$1 credentials_file=${2:-} node_id=${3:-} service_dir=${4:-} local domain=${service_url#https://} domain=${domain#http://} - Network accessline 179
local domain=${service_url#https://} - Network accessline 180
domain=${domain#http://} - Access to secretsline 431
[Credential-related source omitted] - Access to secretsline 432
[Credential-related source omitted] - Access to secretsline 433
[Credential-related source omitted] - Access to secretsline 453
[Credential-related source omitted] - Access to secretsline 469
[Credential-related source omitted] - Access to secretsline 470
[Credential-related source omitted] - Network accessline 487
endpoint=$(_mcp_credentials_value "$credentials_file" mcp_url) || return 1 env_key=$(_mcp_host_token_env_key "$server_name") || return 1 case "$endpoint" in https://*/mcp) ;; *) return 1 ;; esac - Network accessline 488
[Credential-related source omitted] - Access to secretsline 488
[Credential-related source omitted] - Network accessline 489
case "$endpoint" in https://*/mcp) ;; *) return 1 ;; esac - Access to secretsline 493
[Credential-related source omitted] - Access to secretsline 498
[Credential-related source omitted] - Access to secretsline 516
[Credential-related source omitted] - Access to secretsline 520
[Credential-related source omitted] - Dangerous shell operationline 610
rm -f "$legacy_json_config" "$legacy_hermes_json" "$mcp_dir/openclaw-server.json" "$mcp_dir/openclaw.mcp.json" "$mcp_dir/env" || return 1 - Dangerous shell operationline 612
codex) rm -f "$cursor_config" "$openclaw_config" "$hermes_config" || return 1 ;; - Dangerous shell operationline 613
cursor) rm -f "$codex_config" "$openclaw_config" "$hermes_config" || return 1 ;; - Dangerous shell operationline 614
openclaw) rm -f "$codex_config" "$cursor_config" "$hermes_config" || return 1 ;; - Dangerous shell operationline 615
hermes) rm -f "$codex_config" "$cursor_config" "$openclaw_config" || return 1 ;; - Dangerous shell operationline 616
none) rm -f "$codex_config" "$cursor_config" "$openclaw_config" "$hermes_config" || return 1 ;;
scripts/lib/operation_report.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/lib/ops.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 22
cleanup_desired_helper() { rm -f "$desired_helper_tmp"; } - Dangerous shell operationline 25
sudo install -d -m 0755 /var/dirextalk-message-server/updater - Dangerous shell operationline 26
sudo install -m 0755 "$desired_helper_tmp" /var/dirextalk-message-server/updater/set-desired-state.sh - Dangerous shell operationline 27
rm -f "$desired_helper_tmp" - Dangerous shell operationline 46
sudo install -d -o root -g root -m 0700 /var/dirextalk-message-server/production-ops - Dangerous shell operationline 48
cleanup_production_helper() { [ -z "$helper_tmp" ] || rm -f "$helper_tmp"; } - Dangerous shell operationline 61
sudo install -o root -g root -m 0755 "$helper_tmp" "/var/dirextalk-message-server/production-ops/$helper" - Dangerous shell operationline 62
rm -f "$helper_tmp" - Dangerous shell operationline 67
sudo install -o root -g root -m 0644 "$helper_tmp" /etc/systemd/system/dirextalk-split-recovery.service - Dangerous shell operationline 68
rm -f "$helper_tmp" - Dangerous shell operationline 70
sudo systemctl daemon-reload - Dangerous shell operationline 71
sudo systemctl enable dirextalk-split-recovery.service >/dev/null - Dangerous shell operationline 231
actual_host=$(ops_ssh "$state" "set -eu; printf '%s\\t' \"\$(cat /etc/machine-id)\"; sudo docker info --format '{{.ID}}'") || return 1 - Dangerous shell operationline 249
[ "\$(sudo docker info --format '{{.ID}}')" = "\$expected_docker" ] - Access to secretsline 250
[Credential-related source omitted] - Access to secretsline 251
[Credential-related source omitted] - Dangerous shell operationline 252
[ "\$(sudo stat -c '%u:%g:%a' "\$file")" = 0:0:400 ] - Dangerous shell operationline 253
receipt_identity=\$(sudo stat -c '%d:%i:%u:%g:%a' "\$file") - Dangerous shell operationline 254
[Credential-related source omitted] - Access to secretsline 254
[Credential-related source omitted] - Dangerous shell operationline 256
count=\$(sudo awk -F= -v wanted="\$1" '\$1 == wanted {n++} END {print n+0}' "\$file") - Dangerous shell operationline 258
[Credential-related source omitted] - Access to secretsline 258
[Credential-related source omitted] - Dangerous shell operationline 311
trap 'rm -f "$integration_bundle"' EXIT - Dangerous shell operationline 340
remote_receipt_check="receipt=/var/dirextalk-message-server/split/.env; [ -f \"\$receipt\" ] && [ ! -L \"\$receipt\" ] && [ \"\$(sudo stat -c '%u:%g:%a' \"\$receipt\")\" = 0:0:400 ]; [ \"\$(sudo stat -c '%d:%i:%u:%g:%a' \"\$receipt\")\" = $ - Dangerous shell operationline 343
remote_release_command+="sudo docker pull $(ops_sh_quote "$DIREXTALK_UPDATE_MESSAGE_IMAGE_REF") >/dev/null; message_identity=\$(sudo docker image inspect $(ops_sh_quote "$DIREXTALK_UPDATE_MESSAGE_IMAGE_REF") --format '{{index .Config.Labels - Dangerous shell operationline 346
remote_release_command+="sudo docker pull $(ops_sh_quote "$DIREXTALK_UPDATE_AGENT_IMAGE_REF") >/dev/null; agent_identity=\$(sudo docker image inspect $(ops_sh_quote "$DIREXTALK_UPDATE_AGENT_IMAGE_REF") --format '{{index .Config.Labels \"org - Dangerous shell operationline 349
remote_release_command+="sudo /var/dirextalk-message-server/production-ops/reconcile-production.sh; " - Dangerous shell operationline 350
remote_release_command="release_lock=/var/dirextalk-message-server/.direct-release-update.lock; sudo install -o root -g root -m 0600 /dev/null \"\$release_lock\"; sudo flock -n \"\$release_lock\" sh -c $(ops_sh_quote "$remote_release_comman - Dangerous shell operationline 352
[Credential-related source omitted] - Possible obfuscationline 352
[Credential-related source omitted] - Access to secretsline 352
[Credential-related source omitted] - Dangerous shell operationline 448
sudo /var/dirextalk-message-server/updater/set-desired-state.sh maintenance - Dangerous shell operationline 449
sudo /var/dirextalk-message-server/production-ops/reset-production.sh - Dangerous shell operationline 450
sudo /var/dirextalk-message-server/updater/set-desired-state.sh running - Dangerous shell operationline 453
printf 'sudo sh -lc %s\n' "$(ops_sh_quote "$remote_script")"
scripts/lib/paths.sh
scripts/lib/private-files.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/lib/production-release-resolver.mjs
scripts/lib/region.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/lib/remote-mcp-contract.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 5
local service_url=${1:-} authority host= port= label case "$service_url" in https://*) ;; - Network accessline 6
case "$service_url" in https://*) ;; *) return 1 ;; - Network accessline 7
https://*) ;; - Network accessline 9
esac service_url=${service_url%/} authority=${service_url#https://} - Network accessline 10
service_url=${service_url%/} authority=${service_url#https://} [ -n "$authority" ] || return 1 - Network accessline 11
authority=${service_url#https://} - Network accessline 12
[ -n "$authority" ] || return 1 - Network accessline 13
case "$authority" in *[/?#@]*) return 1 ;; esac - Network accessline 14
if [[ "$authority" =~ ^\[[0-9A-Fa-f:]+\](:[0-9]+)?$ ]]; then - Network accessline 15
case "$authority" in - Network accessline 16
*]:*) port=${authority##*]:} ;; esac elif [[ "$authority" =~ ^[A-Za-z0-9.-]+(:[0-9]+)?$ ]]; then - Network accessline 17
esac elif [[ "$authority" =~ ^[A-Za-z0-9.-]+(:[0-9]+)?$ ]]; then host=${authority%%:*} - Network accessline 18
elif [[ "$authority" =~ ^[A-Za-z0-9.-]+(:[0-9]+)?$ ]]; then - Network accessline 19
host=${authority%%:*} case "$authority" in *:*) port=${authority##*:} ;; esac case "$host" in .*|*..*|*.) return 1 ;; esac - Network accessline 20
case "$authority" in *:*) port=${authority##*:} ;; esac
scripts/lib/server-release.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 39
return 1 fi [ "$DIREXTALK_RELEASE_CATALOG_ORIGIN" = https://imadmin.dirextalk.ai ] || return 1 - Network accessline 40
fi [ "$DIREXTALK_RELEASE_CATALOG_ORIGIN" = https://imadmin.dirextalk.ai ] || return 1 [ "$DIREXTALK_POSTGRES_IMAGE_IMMUTABLE" = "docker.io/pgvector/pgvector:pg18@${DIREXTALK_POSTGRES_IMAGE_IMMUTABLE##*@}" ] || return 1 - Network accessline 41
[ "$DIREXTALK_RELEASE_CATALOG_ORIGIN" = https://imadmin.dirextalk.ai ] || return 1
scripts/lib/state.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/lib/test-runner.mjs
- Executable scriptline 1
Executable file - Network accessline 247
if (exists(candidate)) return candidate; } throw new Error("Git for Windows Bash is required to run Dirextalk deployer tests on Windows. Install Git for Windows from https://git-scm.com/download/win or set DIREXTALK_GIT_BASH to its bash - Network accessline 248
} throw new Error("Git for Windows Bash is required to run Dirextalk deployer tests on Windows. Install Git for Windows from https://git-scm.com/download/win or set DIREXTALK_GIT_BASH to its bash.exe path."); } - Network accessline 249
throw new Error("Git for Windows Bash is required to run Dirextalk deployer tests on Windows. Install Git for Windows from https://git-scm.com/download/win or set DIREXTALK_GIT_BASH to its bash.exe path.");
scripts/lib/updater-release.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 12
[ "$UPDATER_PIN_ASSET" = dirextalk-updater-linux-amd64 ] || return 1 [ "$UPDATER_PIN_OS" = linux ] && [ "$UPDATER_PIN_ARCH" = amd64 ] && [ "$UPDATER_PIN_UBUNTU_VERSION" = 24.04 ] || return 1 [ "$UPDATER_PIN_URL" = "https://github.com/Yi - Network accessline 13
[ "$UPDATER_PIN_OS" = linux ] && [ "$UPDATER_PIN_ARCH" = amd64 ] && [ "$UPDATER_PIN_UBUNTU_VERSION" = 24.04 ] || return 1 [ "$UPDATER_PIN_URL" = "https://github.com/YingSuiAI/dirextalk-updater/releases/download/$UPDATER_PIN_VERSION/$UPDAT - Network accessline 14
[ "$UPDATER_PIN_URL" = "https://github.com/YingSuiAI/dirextalk-updater/releases/download/$UPDATER_PIN_VERSION/$UPDATER_PIN_ASSET" ] || return 1
scripts/orchestrate.sh
- Executable scriptline 1
#!/usr/bin/env bash - Executable scriptline 1
#!/usr/bin/env bash - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Executable scriptline 1
Executable file; content unavailable - Dangerous shell operationline 68
rm -f -- "$owner_file" 2>/dev/null || true - Dangerous shell operationline 68
rm -f -- "$owner_file" 2>/dev/null || true - Dangerous shell operationline 121
rm -f -- "$owner_file" 2>/dev/null || return 2 - Dangerous shell operationline 121
rm -f -- "$owner_file" 2>/dev/null || return 2 - Dangerous shell operationline 135
rm -f -- "$owner_file" 2>/dev/null || return 2 - Dangerous shell operationline 135
rm -f -- "$owner_file" 2>/dev/null || return 2 - Dangerous shell operationline 153
rm -f -- "$owner_file" 2>/dev/null || true - Dangerous shell operationline 153
rm -f -- "$owner_file" 2>/dev/null || true - Dangerous shell operationline 160
rm -f -- "$owner_file" 2>/dev/null || true - Dangerous shell operationline 160
rm -f -- "$owner_file" 2>/dev/null || true - Dangerous shell operationline 167
rm -f -- "$owner_file" 2>/dev/null || true - Dangerous shell operationline 167
rm -f -- "$owner_file" 2>/dev/null || true - Network accessline 215
*" aws "*) warn "Install AWS CLI v2 and configure credentials first:" warn " macOS: curl 'https://awscli.amazonaws.com/AWSCLIV2.pkg' -o AWSCLIV2.pkg && sudo installer -pkg ./AWSCLIV2.pkg -target /" - Network accessline 215
*" aws "*) warn "Install AWS CLI v2 and configure credentials first:" warn " macOS: curl 'https://awscli.amazonaws.com/AWSCLIV2.pkg' -o AWSCLIV2.pkg && sudo installer -pkg ./AWSCLIV2.pkg -target /" - Network accessline 216
warn "Install AWS CLI v2 and configure credentials first:" warn " macOS: curl 'https://awscli.amazonaws.com/AWSCLIV2.pkg' -o AWSCLIV2.pkg && sudo installer -pkg ./AWSCLIV2.pkg -target /" warn " Linux x86_64: curl 'https://awsc - Network accessline 216
warn "Install AWS CLI v2 and configure credentials first:" warn " macOS: curl 'https://awscli.amazonaws.com/AWSCLIV2.pkg' -o AWSCLIV2.pkg && sudo installer -pkg ./AWSCLIV2.pkg -target /" warn " Linux x86_64: curl 'https://awsc - Dangerous shell operationline 217
warn " macOS: curl 'https://awscli.amazonaws.com/AWSCLIV2.pkg' -o AWSCLIV2.pkg && sudo installer -pkg ./AWSCLIV2.pkg -target /" - Dangerous shell operationline 217
warn " macOS: curl 'https://awscli.amazonaws.com/AWSCLIV2.pkg' -o AWSCLIV2.pkg && sudo installer -pkg ./AWSCLIV2.pkg -target /" - Network accessline 217
warn " macOS: curl 'https://awscli.amazonaws.com/AWSCLIV2.pkg' -o AWSCLIV2.pkg && sudo installer -pkg ./AWSCLIV2.pkg -target /" - Network accessline 217
warn " macOS: curl 'https://awscli.amazonaws.com/AWSCLIV2.pkg' -o AWSCLIV2.pkg && sudo installer -pkg ./AWSCLIV2.pkg -target /" - Dangerous shell operationline 218
warn " Linux x86_64: curl 'https://awscli.amazonaws.com/awscli-exe-linux-x86_64.zip' -o awscliv2.zip && unzip awscliv2.zip && sudo ./aws/install" - Dangerous shell operationline 218
warn " Linux x86_64: curl 'https://awscli.amazonaws.com/awscli-exe-linux-x86_64.zip' -o awscliv2.zip && unzip awscliv2.zip && sudo ./aws/install" - Network accessline 218
warn " Linux x86_64: curl 'https://awscli.amazonaws.com/awscli-exe-linux-x86_64.zip' -o awscliv2.zip && unzip awscliv2.zip && sudo ./aws/install" - Network accessline 218
warn " Linux x86_64: curl 'https://awscli.amazonaws.com/awscli-exe-linux-x86_64.zip' -o awscliv2.zip && unzip awscliv2.zip && sudo ./aws/install" - Access to secretsline 530
[Credential-related source omitted] - Access to secretsline 530
[Credential-related source omitted] - Network accessline 531
echo " agent room : ${agent_room_id:-written to credentials.json}" echo " dirextalk-connect : package=${cc_pkg:-dirextalk-connect@latest} config=${cc_config:-not recorded} command=${cc_binary:-dirextalk-connect}" echo " MCP - Network accessline 531
echo " agent room : ${agent_room_id:-written to credentials.json}" echo " dirextalk-connect : package=${cc_pkg:-dirextalk-connect@latest} config=${cc_config:-not recorded} command=${cc_binary:-dirextalk-connect}" echo " MCP - Network accessline 532
echo " dirextalk-connect : package=${cc_pkg:-dirextalk-connect@latest} config=${cc_config:-not recorded} command=${cc_binary:-dirextalk-connect}" echo " MCP : transport=http endpoint=${mcp_endpoint:-https://$domain/mcp}" ec - Network accessline 532
echo " dirextalk-connect : package=${cc_pkg:-dirextalk-connect@latest} config=${cc_config:-not recorded} command=${cc_binary:-dirextalk-connect}" echo " MCP : transport=http endpoint=${mcp_endpoint:-https://$domain/mcp}" ec - Network accessline 533
echo " MCP : transport=http endpoint=${mcp_endpoint:-https://$domain/mcp}" - Network accessline 533
echo " MCP : transport=http endpoint=${mcp_endpoint:-https://$domain/mcp}" - Dangerous shell operationline 873
out_curl=$(dirextalk_native_tool_path "$out") || { rm -f "$headers" "$out"; return 1; } - Dangerous shell operationline 873
out_curl=$(dirextalk_native_tool_path "$out") || { rm -f "$headers" "$out"; return 1; } - Dangerous shell operationline 874
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$out"; return 1; } - Dangerous shell operationline 874
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$out"; return 1; } - Network accessline 874
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$out"; return 1; } payload=$(json_build mcp-jsonrpc-initialize) code=$(curl -sk -o "$out_curl" -w '%{http_code}' \ - Network accessline 874
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$out"; return 1; } payload=$(json_build mcp-jsonrpc-initialize) code=$(curl -sk -o "$out_curl" -w '%{http_code}' \ - Network accessline 875
payload=$(json_build mcp-jsonrpc-initialize) code=$(curl -sk -o "$out_curl" -w '%{http_code}' \ -X POST "$endpoint" \ - Network accessline 875
payload=$(json_build mcp-jsonrpc-initialize) code=$(curl -sk -o "$out_curl" -w '%{http_code}' \ -X POST "$endpoint" \ - Network accessline 876
code=$(curl -sk -o "$out_curl" -w '%{http_code}' \ - Network accessline 876
code=$(curl -sk -o "$out_curl" -w '%{http_code}' \ - Dangerous shell operationline 883
rm -f "$headers" - Dangerous shell operationline 883
rm -f "$headers" - Dangerous shell operationline 886
rm -f "$out" - Dangerous shell operationline 886
rm -f "$out" - Dangerous shell operationline 901
rm -f "$out" - Dangerous shell operationline 901
rm -f "$out" - Dangerous shell operationline 923
body_curl=$(dirextalk_native_tool_path "$body") || { rm -f "$headers" "$body"; return 1; } - Dangerous shell operationline 923
body_curl=$(dirextalk_native_tool_path "$body") || { rm -f "$headers" "$body"; return 1; } - Dangerous shell operationline 924
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$body"; return 1; } - Dangerous shell operationline 924
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$body"; return 1; } - Network accessline 924
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$body"; return 1; } payload=$(json_build mcp-jsonrpc-messages-list-call "$room_id") code=$(curl -sk -o "$body_curl" -w '%{http_code}' \ - Network accessline 924
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$body"; return 1; } payload=$(json_build mcp-jsonrpc-messages-list-call "$room_id") code=$(curl -sk -o "$body_curl" -w '%{http_code}' \ - Network accessline 925
payload=$(json_build mcp-jsonrpc-messages-list-call "$room_id") code=$(curl -sk -o "$body_curl" -w '%{http_code}' \ -X POST "$endpoint" \ - Network accessline 925
payload=$(json_build mcp-jsonrpc-messages-list-call "$room_id") code=$(curl -sk -o "$body_curl" -w '%{http_code}' \ -X POST "$endpoint" \ - Network accessline 926
code=$(curl -sk -o "$body_curl" -w '%{http_code}' \ - Network accessline 926
code=$(curl -sk -o "$body_curl" -w '%{http_code}' \ - Dangerous shell operationline 933
rm -f "$headers" - Dangerous shell operationline 933
rm -f "$headers" - Dangerous shell operationline 944
rm -f "$body" - Dangerous shell operationline 944
rm -f "$body" - Dangerous shell operationline 957
rm -f "$body" - Dangerous shell operationline 957
rm -f "$body" - Dangerous shell operationline 978
out_curl=$(dirextalk_native_tool_path "$out") || { rm -f "$headers" "$out"; return 1; } - Dangerous shell operationline 978
out_curl=$(dirextalk_native_tool_path "$out") || { rm -f "$headers" "$out"; return 1; } - Dangerous shell operationline 979
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$out"; return 1; } - Dangerous shell operationline 979
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$out"; return 1; } - Network accessline 979
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$out"; return 1; } payload=$(json_build mcp-jsonrpc-tools-list) code=$(curl -sk -o "$out_curl" -w '%{http_code}' \ - Network accessline 979
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$out"; return 1; } payload=$(json_build mcp-jsonrpc-tools-list) code=$(curl -sk -o "$out_curl" -w '%{http_code}' \ - Network accessline 980
payload=$(json_build mcp-jsonrpc-tools-list) code=$(curl -sk -o "$out_curl" -w '%{http_code}' \ -X POST "$endpoint" \ - Network accessline 980
payload=$(json_build mcp-jsonrpc-tools-list) code=$(curl -sk -o "$out_curl" -w '%{http_code}' \ -X POST "$endpoint" \ - Network accessline 981
code=$(curl -sk -o "$out_curl" -w '%{http_code}' \ - Network accessline 981
code=$(curl -sk -o "$out_curl" -w '%{http_code}' \ - Dangerous shell operationline 988
rm -f "$headers" - Dangerous shell operationline 988
rm -f "$headers" - Dangerous shell operationline 992
rm -f "$out" - Dangerous shell operationline 992
rm -f "$out" - Dangerous shell operationline 1002
rm -f "$out" - Dangerous shell operationline 1002
rm -f "$out" - Network accessline 1014
if [ -z "$service_url" ]; then domain=$(json_get "$STATE_JSON" domain) [ -n "$domain" ] && service_url="https://$domain" - Network accessline 1014
if [ -z "$service_url" ]; then domain=$(json_get "$STATE_JSON" domain) [ -n "$domain" ] && service_url="https://$domain" - Network accessline 1015
domain=$(json_get "$STATE_JSON" domain) [ -n "$domain" ] && service_url="https://$domain" fi - Network accessline 1015
domain=$(json_get "$STATE_JSON" domain) [ -n "$domain" ] && service_url="https://$domain" fi - Network accessline 1016
[ -n "$domain" ] && service_url="https://$domain" - Network accessline 1016
[ -n "$domain" ] && service_url="https://$domain"
scripts/phases/remote_dns_probe.py
- Executable scriptline 1
#!/usr/bin/env python3 - Network accessline 40
packet = struct.pack("!HHHHHH", ident, 0x0100, 1, 0, 0, 0) + question + struct.pack("!HH", qtype, 1) try: sock = socket.socket(socket.AF_INET, socket.SOCK_DGRAM) - Network accessline 41
try: sock = socket.socket(socket.AF_INET, socket.SOCK_DGRAM) sock.settimeout(3) - Network accessline 42
sock = socket.socket(socket.AF_INET, socket.SOCK_DGRAM)
scripts/phases/s0_prereq_aws.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 8
warn "First question: do you already have an AWS account with an access-key CSV or configured AWS profile?" warn " If no AWS account exists yet:" warn " 1. Open https://aws.amazon.com/ and create an account with email, phone verific - Network accessline 9
warn " If no AWS account exists yet:" warn " 1. Open https://aws.amazon.com/ and create an account with email, phone verification, billing card, and the Basic support plan." warn " 2. Wait until the account is fully activated, th - Network accessline 10
warn " 1. Open https://aws.amazon.com/ and create an account with email, phone verification, billing card, and the Basic support plan."
scripts/phases/s1_preflight.sh
scripts/phases/s2_domain.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/phases/s3_provision.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 108
} done [ "$DIREXTALK_RELEASE_CATALOG_ORIGIN" = https://imadmin.dirextalk.ai ] || { - Network accessline 109
done [ "$DIREXTALK_RELEASE_CATALOG_ORIGIN" = https://imadmin.dirextalk.ai ] || { warn "Production split deployment requires the pinned production release catalog origin." - Network accessline 110
[ "$DIREXTALK_RELEASE_CATALOG_ORIGIN" = https://imadmin.dirextalk.ai ] || { - Dangerous shell operationline 375
rm -f "$keyfile" - Dangerous shell operationline 526
host_read=$(ssh -T -i "$keyfile" -o BatchMode=yes -o ConnectTimeout=10 -o StrictHostKeyChecking=yes -o "UserKnownHostsFile=$known_hosts" ubuntu@"$public_ip" "set -eu; printf '%s\\t' \"\$(cat /etc/machine-id)\"; sudo docker info -- - Dangerous shell operationline 528
"set -eu; printf '%s\\t' \"\$(cat /etc/machine-id)\"; sudo docker info --format '{{.ID}}'") || return 1 - Dangerous shell operationline 610
rm -f -- "$path" || return 1 - Dangerous shell operationline 647
rm -f -- "$integration_bundle" "$split_bundle" - Dangerous shell operationline 651
rm -f -- "$integration_bundle" "$split_bundle" - Dangerous shell operationline 656
rm -f -- "$integration_bundle" "$split_bundle" - Dangerous shell operationline 684
rm -f "$integration_bundle" - Dangerous shell operationline 685
[ -z "$split_bundle" ] || rm -f "$split_bundle" - Dangerous shell operationline 692
remote_command="stage=\$(sudo mktemp -d /tmp/dirextalk-updater-integration.XXXXXX) && trap 'sudo rm -rf \"\$stage\"' EXIT && sudo chmod 0700 \"\$stage\" && sudo tar --no-same-owner -xzf - -C \"\$stage\" && sudo bash \"\$stage/updater/bootst - Dangerous shell operationline 694
*) rm -f "$integration_bundle" "$split_bundle"; warn "Host bootstrap requires the supported Ubuntu SSH user."; return 1 ;; - Dangerous shell operationline 707
rm -f "$integration_bundle" - Dangerous shell operationline 708
[ -z "$split_bundle" ] || rm -f "$split_bundle" - Dangerous shell operationline 720
rm -f "$integration_bundle" "$split_bundle" - Dangerous shell operationline 729
rm -f "$integration_bundle" - Dangerous shell operationline 730
[ -z "$split_bundle" ] || rm -f "$split_bundle" - Dangerous shell operationline 825
rm -f "$tmp" - Dangerous shell operationline 832
rm -f "$tmp" - Dangerous shell operationline 861
rm -f "$tmp" - Dangerous shell operationline 865
rm -f "$tmp" - Dangerous shell operationline 868
rm -f "$tmp" - Dangerous shell operationline 988
change_file_aws=$(dirextalk_native_tool_path "$change_file") || { rm -f "$change_file"; return 1; } - Dangerous shell operationline 993
rm -f "$change_file" - Dangerous shell operationline 997
rm -f "$change_file"
scripts/phases/s4_bootstrap_stack.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 14
log "Waiting for bootstrap (install Docker -> start postgres/message-server/caddy/coturn -> issue Let's Encrypt certificate)..." log "First image pull and certificate issuance usually take 5-10 minutes. Checking https://$domain/_p2p/healt - Network accessline 15
log "First image pull and certificate issuance usually take 5-10 minutes. Checking https://$domain/_p2p/health every ${HEALTH_POLL_INTERVAL:-10}s (curl connect timeout ${curl_connect_timeout}s, max ${curl_max_time}s) ..." - Network accessline 17
if poll_until "health check https://$domain/_p2p/health == 200" \ - Network accessline 18
"${HEALTH_POLL_INTERVAL:-10}" "${HEALTH_POLL_MAX:-90}" _server_health_ok "$domain"; then phase_set S4_BOOTSTRAP_STACK done "_p2p/health 200 @ https://$domain" return 0 - Network accessline 19
phase_set S4_BOOTSTRAP_STACK done "_p2p/health 200 @ https://$domain" - Dangerous shell operationline 25
[Credential-related source omitted] - Access to secretsline 25
[Credential-related source omitted] - Dangerous shell operationline 27
warn " ssh -i $keyfile ubuntu@$pubip 'sudo tail -n 80 /var/log/cloud-init-output.log; $split_diagnostics'" - Network accessline 35
curl_args=(-skf --connect-timeout "${HEALTH_CURL_CONNECT_TIMEOUT:-10}" --max-time "${HEALTH_CURL_MAX_TIME:-20}") if [ -n "$pubip" ]; then curl "${curl_args[@]}" --resolve "$domain:443:$pubip" "https://$domain/_p2p/health" >/dev/null 2 - Network accessline 36
if [ -n "$pubip" ]; then curl "${curl_args[@]}" --resolve "$domain:443:$pubip" "https://$domain/_p2p/health" >/dev/null 2>&1 && return 0 fi - Network accessline 37
curl "${curl_args[@]}" --resolve "$domain:443:$pubip" "https://$domain/_p2p/health" >/dev/null 2>&1 && return 0 - Network accessline 38
fi curl "${curl_args[@]}" "https://$domain/_p2p/health" >/dev/null 2>&1 } - Network accessline 39
curl "${curl_args[@]}" "https://$domain/_p2p/health" >/dev/null 2>&1
scripts/phases/s5_init_tokens.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 18
trap 'rm -f "${raw:-}"; trap - RETURN' RETURN - Dangerous shell operationline 25
[Credential-related source omitted] - Access to secretsline 25
[Credential-related source omitted] - Access to secretsline 43
[Credential-related source omitted] - Access to secretsline 44
[Credential-related source omitted] - Network accessline 46
[Credential-related source omitted] - Access to secretsline 46
[Credential-related source omitted] - Network accessline 47
fi asurl=$(json_get "$out" as_url "https://$domain") if ! asurl=$(dirextalk_service_origin "$asurl"); then - Network accessline 48
asurl=$(json_get "$out" as_url "https://$domain") - Dangerous shell operationline 64
rm -f "$owner_session" - Dangerous shell operationline 73
rm -f "$owner_session" - Dangerous shell operationline 79
rm -f "$owner_session" - Access to secretsline 86
[Credential-related source omitted] - Access to secretsline 87
[Credential-related source omitted] - Dangerous shell operationline 91
rm -f "$owner_session" - Access to secretsline 94
[Credential-related source omitted] - Access to secretsline 104
[Credential-related source omitted] - Dangerous shell operationline 119
rm -f "$request" - Dangerous shell operationline 123
rm -f "$request" "$response" - Dangerous shell operationline 126
request_curl=$(dirextalk_native_tool_path "$request") || { rm -f "$request" "$response"; return 1; } - Dangerous shell operationline 127
response_curl=$(dirextalk_native_tool_path "$response") || { rm -f "$request" "$response"; return 1; } - Network accessline 128
request_arg="@$request_curl" curl_status=0 code=$(curl -sS \ - Network accessline 129
curl_status=0 code=$(curl -sS \ --connect-timeout "${DIREXTALK_PORTAL_AUTH_CURL_CONNECT_TIMEOUT:-10}" \ - Network accessline 130
code=$(curl -sS \ - Network accessline 134
--output "$response_curl" --write-out '%{http_code}' \ --request POST --header 'Content-Type: application/json' \ --data-binary "$request_arg" "https://$domain/_p2p/command" 2>/dev/null) || curl_status=$? - Network accessline 135
--request POST --header 'Content-Type: application/json' \ --data-binary "$request_arg" "https://$domain/_p2p/command" 2>/dev/null) || curl_status=$? rm -f "$request" - Network accessline 136
--data-binary "$request_arg" "https://$domain/_p2p/command" 2>/dev/null) || curl_status=$? - Dangerous shell operationline 137
rm -f "$request" - Dangerous shell operationline 139
rm -f "$response" - Access to secretsline 144
[Credential-related source omitted] - Dangerous shell operationline 150
rm -f "$response" - Dangerous shell operationline 156
rm -f "$response" - Dangerous shell operationline 160
rm -f "$response" - Access to secretsline 167
[Credential-related source omitted] - Access to secretsline 171
[Credential-related source omitted] - Access to secretsline 172
[Credential-related source omitted] - Access to secretsline 174
[Credential-related source omitted] - Dangerous shell operationline 188
cmd=(ssh "${ssh_args[@]}" ubuntu@"$pubip" "sudo test -s '${DIREXTALK_REMOTE_BOOTSTRAP_FILE}' && sudo cat '${DIREXTALK_REMOTE_BOOTSTRAP_FILE}'") - Dangerous shell operationline 202
rm -f "$tmp" - Network accessline 212
null_device=$(dirextalk_native_null_device) || return 1 [ -n "$pubip" ] && args=(--resolve "$domain:443:$pubip") [ "$(curl -sk "${args[@]}" -o "$null_device" -w '%{http_code}' "https://$domain/.well-known/portal/owner.json" 2>/dev/null) - Network accessline 213
[ -n "$pubip" ] && args=(--resolve "$domain:443:$pubip") [ "$(curl -sk "${args[@]}" -o "$null_device" -w '%{http_code}' "https://$domain/.well-known/portal/owner.json" 2>/dev/null)" = "200" ] } - Network accessline 214
[ "$(curl -sk "${args[@]}" -o "$null_device" -w '%{http_code}' "https://$domain/.well-known/portal/owner.json" 2>/dev/null)" = "200" ]
scripts/phases/s6_wire_local.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 456
_connect_repo() { printf '%s\n' "${DIREXTALK_CONNECT_REPO:-https://github.com/YingSuiAI/dirextalk-connect.git}" - Network accessline 457
printf '%s\n' "${DIREXTALK_CONNECT_REPO:-https://github.com/YingSuiAI/dirextalk-connect.git}" - Access to secretsline 577
[Credential-related source omitted] - Access to secretsline 578
[Credential-related source omitted] - Access to secretsline 590
[Credential-related source omitted] - Access to secretsline 595
[Credential-related source omitted] - Access to secretsline 599
[Credential-related source omitted] - Access to secretsline 604
[Credential-related source omitted] - Access to secretsline 609
[Credential-related source omitted] - Access to secretsline 615
[Credential-related source omitted] - Access to secretsline 625
[Credential-related source omitted] - Access to secretsline 649
[Credential-related source omitted] - Dangerous shell operationline 661
rm -f "$http_body" 2>/dev/null || true - Access to secretsline 664
[Credential-related source omitted] - Dangerous shell operationline 665
rm -f "$http_body" 2>/dev/null || true - Dangerous shell operationline 668
http_body_curl=$(dirextalk_native_tool_path "$http_body") || { rm -f "$headers" "$http_body"; return 1; } - Network accessline 668
http_body_curl=$(dirextalk_native_tool_path "$http_body") || { rm -f "$headers" "$http_body"; return 1; } headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$http_body"; return 1; } code=$(curl -sk \ - Dangerous shell operationline 669
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$http_body"; return 1; } - Network accessline 669
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers" "$http_body"; return 1; } code=$(curl -sk \ --connect-timeout "${DIREXTALK_MATRIX_SESSION_CURL_CONNECT_TIMEOUT:-10}" \ - Network accessline 670
code=$(curl -sk \ - Dangerous shell operationline 677
rm -f "$headers" - Dangerous shell operationline 681
rm -f "$http_body" - Dangerous shell operationline 685
rm -f "$http_body" 2>/dev/null || true - Dangerous shell operationline 691
rm -f "$http_body" - Access to secretsline 750
[Credential-related source omitted] - Access to secretsline 757
[Credential-related source omitted] - Access to secretsline 789
[Credential-related source omitted] - Access to secretsline 812
[Credential-related source omitted] - Network accessline 1129
local runtime=$1 domain=$2 room=$3 explicit host digest raw explicit=${DIREXTALK_AGENT_NODE_ID:-} host=${domain#http://} - Network accessline 1130
explicit=${DIREXTALK_AGENT_NODE_ID:-} host=${domain#http://} host=${host#https://} - Network accessline 1131
host=${domain#http://} - Network accessline 1132
host=${host#https://} - Access to secretsline 1156
[Credential-related source omitted] - Access to secretsline 1157
[Credential-related source omitted] - Access to secretsline 1207
[Credential-related source omitted] - Access to secretsline 1217
[Credential-related source omitted] - Access to secretsline 1221
[Credential-related source omitted] - Dangerous shell operationline 1265
if ! rm -f "$service_dir/env"; then - Access to secretsline 1295
[Credential-related source omitted] - Access to secretsline 1354
[Credential-related source omitted] - Access to secretsline 1389
[Credential-related source omitted]
scripts/phases/s7_verify_e2e.sh
- Executable scriptline 1
#!/usr/bin/env bash - Access to secretsline 16
[Credential-related source omitted] - Access to secretsline 18
[Credential-related source omitted] - Network accessline 21
_check "message-server health" "https://$domain/_p2p/health" "" 200 || fails=$((fails+1)) - Network accessline 22
_check "matrix versions" "https://$domain/_matrix/client/versions" "" 200 || fails=$((fails+1)) - Access to secretsline 26
[Credential-related source omitted] - Dangerous shell operationline 57
tmp_curl=$(dirextalk_native_tool_path "$tmp") || { rm -f "$tmp"; return 1; } - Dangerous shell operationline 58
null_device=$(dirextalk_native_null_device) || { rm -f "$tmp"; return 1; } - Network accessline 59
local args=() while IFS= read -r arg; do args+=("$arg"); done < <(curl_resolve_args "$domain") code=$(curl -sk "${args[@]}" -o "$null_device" -D "$tmp_curl" -w '%{http_code}' \ - Network accessline 60
while IFS= read -r arg; do args+=("$arg"); done < <(curl_resolve_args "$domain") code=$(curl -sk "${args[@]}" -o "$null_device" -D "$tmp_curl" -w '%{http_code}' \ -H 'Origin: http://127.0.0.1:51820' \ - Network accessline 61
code=$(curl -sk "${args[@]}" -o "$null_device" -D "$tmp_curl" -w '%{http_code}' \ - Network accessline 62
-H 'Origin: http://127.0.0.1:51820' \ - Network accessline 63
"https://$domain/.well-known/portal/owner.json" 2>/dev/null) - Dangerous shell operationline 65
rm -f "$tmp" - Network accessline 67
if [ "$code" = "200" ] && printf '%s' "$cors" | grep -Eiq 'Access-Control-Allow-Origin:[[:space:]]*(\*|http://127\.0\.0\.1:51820)$'; then - Network accessline 77
local args=() while IFS= read -r arg; do args+=("$arg"); done < <(curl_resolve_args "$domain") body=$(curl -sk "${args[@]}" "https://$domain/.well-known/matrix/server" 2>/dev/null) - Network accessline 78
while IFS= read -r arg; do args+=("$arg"); done < <(curl_resolve_args "$domain") body=$(curl -sk "${args[@]}" "https://$domain/.well-known/matrix/server" 2>/dev/null) if printf '%s' "$body" | json_stdin_assert well-known-server "$domain - Network accessline 79
body=$(curl -sk "${args[@]}" "https://$domain/.well-known/matrix/server" 2>/dev/null) - Network accessline 94
headers=$(dirextalk_curl_secret_headers "${TMPDIR:-/tmp}" "$tok") || return 1 headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers"; return 1; } code=$(curl -sk "${args[@]}" -o "$null_device" -w '%{http_code} - Dangerous shell operationline 95
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers"; return 1; } - Network accessline 95
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers"; return 1; } code=$(curl -sk "${args[@]}" -o "$null_device" -w '%{http_code}' -H "$headers_arg" "$url" 2>/dev/null) rm -f "$headers" - Network accessline 96
code=$(curl -sk "${args[@]}" -o "$null_device" -w '%{http_code}' -H "$headers_arg" "$url" 2>/dev/null) - Dangerous shell operationline 97
rm -f "$headers" - Network accessline 97
rm -f "$headers" else code=$(curl -sk "${args[@]}" -o "$null_device" -w '%{http_code}' "$url" 2>/dev/null) - Network accessline 98
else code=$(curl -sk "${args[@]}" -o "$null_device" -w '%{http_code}' "$url" 2>/dev/null) fi - Network accessline 99
code=$(curl -sk "${args[@]}" -o "$null_device" -w '%{http_code}' "$url" 2>/dev/null) - Access to secretsline 111
[Credential-related source omitted] - Network accessline 112
headers=$(dirextalk_curl_secret_headers "${TMPDIR:-/tmp}" "$at") || return 1 headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers"; return 1; } turn=$(curl -sk "${args[@]}" "https://$domain/_matrix/client/v3/voip - Dangerous shell operationline 113
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers"; return 1; } - Network accessline 113
headers_arg=$(dirextalk_native_tool_at_path "$headers") || { rm -f "$headers"; return 1; } turn=$(curl -sk "${args[@]}" "https://$domain/_matrix/client/v3/voip/turnServer" \ -H "$headers_arg" 2>/dev/null) - Network accessline 114
turn=$(curl -sk "${args[@]}" "https://$domain/_matrix/client/v3/voip/turnServer" \ - Dangerous shell operationline 116
rm -f "$headers"
scripts/pricing-estimate.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/render/prepare-production-release.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 58
release_catalog_origin=$(read_unique_pair "$release_pin" DIREXTALK_RELEASE_CATALOG_ORIGIN) \ || die 'existing release catalog origin is invalid' [ "$release_catalog_origin" = https://imadmin.dirextalk.ai ] \ - Network accessline 59
|| die 'existing release catalog origin is invalid' [ "$release_catalog_origin" = https://imadmin.dirextalk.ai ] \ || die 'production release catalog origin must be https://imadmin.dirextalk.ai' - Network accessline 60
[ "$release_catalog_origin" = https://imadmin.dirextalk.ai ] \ - Network accessline 61
|| die 'production release catalog origin must be https://imadmin.dirextalk.ai' - Dangerous shell operationline 64
trap 'rm -rf "$work"' EXIT HUP INT TERM
scripts/render/render-split-bundle.sh
scripts/render/render-userdata.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 86
} done [ "$RELEASE_CATALOG_ORIGIN" = https://imadmin.dirextalk.ai ] || { - Network accessline 87
done [ "$RELEASE_CATALOG_ORIGIN" = https://imadmin.dirextalk.ai ] || { echo "--release-catalog-origin must be https://imadmin.dirextalk.ai" >&2 - Network accessline 88
[ "$RELEASE_CATALOG_ORIGIN" = https://imadmin.dirextalk.ai ] || { - Network accessline 89
echo "--release-catalog-origin must be https://imadmin.dirextalk.ai" >&2 - Dangerous shell operationline 98
trap 'rm -rf "$WORK"' EXIT - Dangerous shell operationline 105
find "$WORK" -name '._*' -delete - Access to secretsline 120
[Credential-related source omitted] - Access to secretsline 126
[Credential-related source omitted] - Access to secretsline 127
[Credential-related source omitted] - Network accessline 136
if ! command -v docker >/dev/null 2>&1; then curl -fsSL https://get.docker.com | sh - Dangerous shell operationline 137
curl -fsSL https://get.docker.com | sh - Network accessline 137
curl -fsSL https://get.docker.com | sh - Dangerous shell operationline 148
EXTRA_WF=$(mktemp); trap 'rm -rf "$WORK" "$EXTRA_WF"' EXIT
scripts/reset-app-data.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/run-tests.mjs
- Executable scriptline 1
#!/usr/bin/env node
scripts/update.sh
- Executable scriptline 1
#!/usr/bin/env bash
scripts/updater/bootstrap-host.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 46
rm -f "$stage_tmp" 2>/dev/null || true - Dangerous shell operationline 90
rm -f "$temporary" 2>/dev/null || true - Access to secretsline 110
[Credential-related source omitted] - Access to secretsline 155
[Credential-related source omitted] - Access to secretsline 156
[Credential-related source omitted] - Network accessline 234
[ "$UPDATER_PIN_OS/$UPDATER_PIN_ARCH/$UPDATER_PIN_UBUNTU_VERSION" = linux/amd64/24.04 ] || { echo "unsupported updater platform pin" >&2; exit 1; } [ "$UPDATER_PIN_ASSET" = dirextalk-updater-linux-amd64 ] || { echo "invalid updater asset pi - Network accessline 236
[ "$UPDATER_PIN_URL" = "https://github.com/YingSuiAI/dirextalk-updater/releases/download/$UPDATER_PIN_VERSION/$UPDATER_PIN_ASSET" ] || { echo "invalid updater URL pin" >&2; exit 1; } - Dangerous shell operationline 245
cleanup_updater_tmp() { rm -f "$updater_tmp"; } - Network accessline 245
cleanup_updater_tmp() { rm -f "$updater_tmp"; } trap cleanup_updater_tmp EXIT curl --fail --silent --show-error --location --proto '=https' --tlsv1.2 \ - Network accessline 246
trap cleanup_updater_tmp EXIT curl --fail --silent --show-error --location --proto '=https' --tlsv1.2 \ --output "$updater_tmp" "$UPDATER_PIN_URL" - Network accessline 247
curl --fail --silent --show-error --location --proto '=https' --tlsv1.2 \
scripts/updater/install.sh
scripts/updater/reconcile-host.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 69
rm -rf -- "$transition_dir" - Network accessline 104
[Credential-related source omitted] - Network accessline 105
[Credential-related source omitted] - Network accessline 106
| curl --silent --show-error --config - \ - Network accessline 108
--header 'Content-Type: application/json' \ --data "$body" --output "$output" --write-out '%{http_code}' \ http://localhost/_dirextalk/updater/v1/control/status); then - Network accessline 109
--data "$body" --output "$output" --write-out '%{http_code}' \ http://localhost/_dirextalk/updater/v1/control/status); then : - Network accessline 110
http://localhost/_dirextalk/updater/v1/control/status); then - Network accessline 127
[Credential-related source omitted] - Network accessline 128
[Credential-related source omitted] - Network accessline 129
| curl --silent --show-error --config - \ - Network accessline 131
--header 'Content-Type: application/json' \ --data "{\"desired_state\":\"$desired\"}" --output "$output" --write-out '%{http_code}' \ http://localhost/_dirextalk/updater/v1/control/desired-state); then - Network accessline 132
--data "{\"desired_state\":\"$desired\"}" --output "$output" --write-out '%{http_code}' \ http://localhost/_dirextalk/updater/v1/control/desired-state); then : - Network accessline 133
http://localhost/_dirextalk/updater/v1/control/desired-state); then - Dangerous shell operationline 258
rm -f -- "$quarantine" || die 'could not remove obsolete updater state quarantine' - Dangerous shell operationline 482
rm -f "$integration_dir/dirextalk-updater-discovery.service" \
scripts/updater/release.env
- Network accessline 1
UPDATER_PIN_VERSION=v1.0.19 UPDATER_PIN_COMMIT=1e71b9d53c599e8fb9227050b8c9643ce723acc5 UPDATER_PIN_URL=https://github.com/YingSuiAI/dirextalk-updater/releases/download/v1.0.19/dirextalk-updater-linux-amd64 - Network accessline 2
UPDATER_PIN_COMMIT=1e71b9d53c599e8fb9227050b8c9643ce723acc5 UPDATER_PIN_URL=https://github.com/YingSuiAI/dirextalk-updater/releases/download/v1.0.19/dirextalk-updater-linux-amd64 UPDATER_PIN_ASSET=dirextalk-updater-linux-amd64 - Network accessline 3
UPDATER_PIN_URL=https://github.com/YingSuiAI/dirextalk-updater/releases/download/v1.0.19/dirextalk-updater-linux-amd64
scripts/updater/set-desired-state.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 15
trap 'rm -f -- "$response_file"' EXIT - Network accessline 44
[Credential-related source omitted] - Network accessline 45
[Credential-related source omitted] - Network accessline 46
| curl --silent --show-error --config - \ - Network accessline 49
--data "{\"desired_state\":\"$desired\"}" \ --output "$response_file" --write-out '%{http_code}' \ http://localhost/_dirextalk/updater/v1/control/desired-state); then - Network accessline 50
--output "$response_file" --write-out '%{http_code}' \ http://localhost/_dirextalk/updater/v1/control/desired-state); then : - Network accessline 51
http://localhost/_dirextalk/updater/v1/control/desired-state); then
tests/atomic_write_test.sh
tests/aws_credentials_test.sh
tests/aws_proxy_environment_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 6
export AWS_DEFAULT_REGION=ap-northeast-2 export HTTP_PROXY=http://127.0.0.1:7897 - Network accessline 7
export HTTP_PROXY=http://127.0.0.1:7897 - Network accessline 8
export HTTPS_PROXY=http://127.0.0.1:7897 - Network accessline 9
export http_proxy=http://127.0.0.1:7897 - Network accessline 10
export https_proxy=http://127.0.0.1:7897 - Network accessline 18
[ "$HTTP_PROXY" = "http://127.0.0.1:7897" ] - Network accessline 19
[ "$HTTPS_PROXY" = "http://127.0.0.1:7897" ] - Network accessline 20
[ "$http_proxy" = "http://127.0.0.1:7897" ] - Network accessline 21
[ "$https_proxy" = "http://127.0.0.1:7897" ]
tests/bootstrap_production_retry_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 6
trap 'rm -rf "$tmp"' EXIT - Access to secretsline 45
[Credential-related source omitted] - Access to secretsline 46
[Credential-related source omitted] - Access to secretsline 47
[Credential-related source omitted] - Access to secretsline 48
[Credential-related source omitted] - Access to secretsline 49
[Credential-related source omitted] - Access to secretsline 50
[Credential-related source omitted] - Access to secretsline 51
[Credential-related source omitted] - Access to secretsline 52
[Credential-related source omitted] - Access to secretsline 54
[Credential-related source omitted] - Dangerous shell operationline 91
rm -f "$DIREXTALK_TEST_RESOURCE" - Dangerous shell operationline 92
rm -f "$DIREXTALK_TEST_RUNNER_INTEGRATION" - Access to secretsline 128
[Credential-related source omitted] - Network accessline 139
AGENT_SOURCE_REVISION=bbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbb DIREXTALK_CLOUD_WORKER_HOST_REGION=ap-east-1 DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Network accessline 140
DIREXTALK_CLOUD_WORKER_HOST_REGION=ap-east-1 DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai EOF - Network accessline 141
DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Access to secretsline 143
[Credential-related source omitted] - Access to secretsline 150
[Credential-related source omitted] - Access to secretsline 151
[Credential-related source omitted] - Access to secretsline 266
[Credential-related source omitted] - Access to secretsline 270
[Credential-related source omitted] - Access to secretsline 271
[Credential-related source omitted] - Access to secretsline 276
[Credential-related source omitted] - Access to secretsline 277
[Credential-related source omitted]
tests/destroy_host_mcp_cleanup_test.sh
tests/destroy_lightsail_test.sh
tests/destroy_local_bridge_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 8
trap 'rm -rf "$tmp"' EXIT - Network accessline 66
json_build object region=us-east-1 domain_mode=user "domain=$domain" "as_url=https://$domain" - Network accessline 68
domain_mode=user \ "domain=$domain" \ "as_url=https://$domain" \ - Network accessline 69
"domain=$domain" \ "as_url=https://$domain" \ "agent_service_dir=$service_dir" \ - Network accessline 70
"as_url=https://$domain" \
tests/destroy_root_identity_test.sh
tests/domain_authoritative_dns_test.sh
tests/domain_dns_mode_detection_test.sh
tests/domain_route53_default_test.sh
tests/eip_preflight_test.sh
tests/existing_node_update_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 6
trap 'rm -rf "$tmp"' EXIT - Access to secretsline 105
[Credential-related source omitted] - Dangerous shell operationline 198
grep -Fq 'sudo flock -n "$release_lock" sh -c' "$REMOTE_COMMAND" - Dangerous shell operationline 206
*"ensure-host-null-device.sh"*"sudo docker pull"*) ;; - Access to secretsline 213
[Credential-related source omitted]
tests/final_delivery_runtime_gate_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 12
trap 'rm -rf "$tmp"' EXIT - Network accessline 45
cat > "$fakebin/curl" <<'EOF' - Network accessline 62
case "$args" in *"https://final-delivery.example.test/mcp"*) - Network accessline 63
*"https://final-delivery.example.test/mcp"*) - Network accessline 69
;; esac case "$args" in *AGENT_TOKEN_FINAL*) echo "token leaked into curl argv" >&2; exit 1 ;; esac - Network accessline 70
esac case "$args" in *AGENT_TOKEN_FINAL*) echo "token leaked into curl argv" >&2; exit 1 ;; esac case "$args" in - Network accessline 71
case "$args" in *AGENT_TOKEN_FINAL*) echo "token leaked into curl argv" >&2; exit 1 ;; esac - Network accessline 87
;; *) echo "unexpected curl URL: $args" >&2 - Network accessline 88
*) echo "unexpected curl URL: $args" >&2 exit 1 - Network accessline 89
echo "unexpected curl URL: $args" >&2 - Network accessline 106
[Credential-related source omitted] - Possible obfuscationline 106
[Credential-related source omitted] - Access to secretsline 106
[Credential-related source omitted] - Network accessline 111
domain=final-delivery.example.test \ domain_confirmed_irreversible=true \ as_url=https://final-delivery.example.test \ - Network accessline 112
domain_confirmed_irreversible=true \ as_url=https://final-delivery.example.test \ mcp_endpoint_url=https://final-delivery.example.test/mcp \ - Network accessline 113
as_url=https://final-delivery.example.test \ - Network accessline 114
mcp_endpoint_url=https://final-delivery.example.test/mcp \ - Access to secretsline 116
[Credential-related source omitted]
tests/fixtures/split-stack-fault-upstream.mjs
- Executable scriptline 1
Executable file
tests/git_bash_windows_contract_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 38
source scripts/lib/git-bash.sh printf '%s\n' "$missing_git_output" | grep -q 'https://git-scm.com/download/win' || { - Network accessline 39
printf '%s\n' "$missing_git_output" | grep -q 'https://git-scm.com/download/win' || { - Dangerous shell operationline 125
trap 'rm -rf "$tmp"' EXIT
tests/host_integration_atomic_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 7
trap 'rm -rf "$tmp"' EXIT - Network accessline 94
printf '[Unit]\nDescription=fixture\n' >"$stage/cloud-init/split/dirextalk-split-recovery.service" cat >"$stage/cloud-init/split/release.env" <<EOF DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Network accessline 95
cat >"$stage/cloud-init/split/release.env" <<EOF DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai DIREXTALK_MESSAGE_SERVER_IMAGE=$message_image - Network accessline 96
DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Access to secretsline 124
[Credential-related source omitted] - Dangerous shell operationline 147
rm -f "$SYSTEMCTL_ACTIVE" - Dangerous shell operationline 150
rm -rf "$base" - Network accessline 159
EOF cat >"$base/.env" <<EOF DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Network accessline 160
[Credential-related source omitted] - Access to secretsline 160
[Credential-related source omitted] - Network accessline 161
DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Access to secretsline 173
[Credential-related source omitted] - Dangerous shell operationline 179
rm -rf "$base" - Network accessline 181
printf 'user-data-updater\n' >"$base/updater/sentinel" cat >"$base/.env" <<EOF DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Network accessline 182
[Credential-related source omitted] - Access to secretsline 182
[Credential-related source omitted] - Network accessline 183
DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Access to secretsline 194
[Credential-related source omitted] - Access to secretsline 209
[Credential-related source omitted] - Access to secretsline 223
[Credential-related source omitted] - Access to secretsline 235
[Credential-related source omitted] - Access to secretsline 248
[Credential-related source omitted] - Access to secretsline 261
[Credential-related source omitted] - Access to secretsline 275
[Credential-related source omitted] - Access to secretsline 304
[Credential-related source omitted]
tests/json_helper_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 13
trap 'rm -rf "$tmp"' EXIT - Network accessline 114
exit 1 fi if $JSON build mcp-http-json-config server https://service.example.test/mcp token > "$tmp/legacy-mcp-config.json" 2>/dev/null; then - Network accessline 115
fi if $JSON build mcp-http-json-config server https://service.example.test/mcp token > "$tmp/legacy-mcp-config.json" 2>/dev/null; then echo "retired token-bearing standalone MCP config action must not be generated" >&2 - Network accessline 116
if $JSON build mcp-http-json-config server https://service.example.test/mcp token > "$tmp/legacy-mcp-config.json" 2>/dev/null; then
tests/lib/isolated_home.sh
- Executable scriptline 1
#!/usr/bin/env bash
tests/lib/json_test.sh
- Executable scriptline 1
#!/usr/bin/env bash
tests/lib/linux-flock.sh
tests/lib/linux-install.sh
- Executable scriptline 1
#!/usr/bin/env bash
tests/lib/run_isolated.sh
tests/lib/split-release.sh
- Executable scriptline 1
#!/usr/bin/env bash
tests/lightsail_static_ip_quota_test.sh
tests/local_paths_test.sh
tests/mcp_tools_runtime_check_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 8
trap 'rm -rf "$tmp"' EXIT - Network accessline 14
fakebin="$tmp/bin" mkdir -p "$fakebin" cat > "$fakebin/curl" <<'EOF' - Network accessline 15
mkdir -p "$fakebin" cat > "$fakebin/curl" <<'EOF' #!/usr/bin/env bash - Network accessline 16
cat > "$fakebin/curl" <<'EOF' - Network accessline 22
want_url="https://mcp-tools.example.test/mcp" - Network accessline 23
case " $* " in *" $want_url "*|*" $want_url") ;; - Network accessline 24
*" $want_url "*|*" $want_url") - Network accessline 25
;; *) echo "unexpected curl URL: $*" >&2 - Network accessline 26
*) echo "unexpected curl URL: $*" >&2 exit 1 - Network accessline 27
echo "unexpected curl URL: $*" >&2 - Network accessline 32
case " $* " in *AGENT_TOKEN_TOOLS*) echo "token leaked into curl argv" >&2; exit 1 ;; esac - Network accessline 85
json_build object run_id=mcp-tools-test region=ap-northeast-1 domain_mode=user domain=mcp-tools.example.test as_url=https://mcp-tools.example.test - Network accessline 88
domain_mode=user \ domain=mcp-tools.example.test \ as_url=https://mcp-tools.example.test \ - Network accessline 89
domain=mcp-tools.example.test \ as_url=https://mcp-tools.example.test \ agent_service_id=mcp-tools.example.test \ - Network accessline 90
as_url=https://mcp-tools.example.test \ - Network accessline 93
"agent_credentials_file=$credentials" \ "mcp_credentials_file=$credentials" \ mcp_endpoint_url=https://mcp-tools.example.test/mcp \ - Network accessline 94
[Credential-related source omitted] - Network accessline 95
mcp_endpoint_url=https://mcp-tools.example.test/mcp \ - Network accessline 106
json_test_check "$state" "data.runtime_checks.mcp_tools.status === 'passed' && data.runtime_checks.mcp_tools.endpoint === 'https://mcp-tools.example.test/mcp' && data.runtime_checks.mcp_tools.tool_count === 3 && data.runtime_checks.mcp_tool
tests/message_mcp_binding_migration_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 6
trap 'rm -rf "$tmp"' EXIT - Access to secretsline 15
[Credential-related source omitted] - Access to secretsline 24
[Credential-related source omitted] - Access to secretsline 25
[Credential-related source omitted] - Access to secretsline 27
[Credential-related source omitted] - Access to secretsline 55
[Credential-related source omitted] - Access to secretsline 73
[Credential-related source omitted] - Access to secretsline 75
[Credential-related source omitted] - Access to secretsline 79
[Credential-related source omitted] - Access to secretsline 80
[Credential-related source omitted] - Access to secretsline 83
[Credential-related source omitted] - Access to secretsline 84
[Credential-related source omitted] - Access to secretsline 116
[Credential-related source omitted] - Access to secretsline 117
[Credential-related source omitted] - Access to secretsline 118
[Credential-related source omitted] - Access to secretsline 119
[Credential-related source omitted] - Access to secretsline 120
[Credential-related source omitted] - Access to secretsline 121
[Credential-related source omitted]
tests/npm_skill_distribution_test.sh
tests/npm_test_suite.sh
- Executable scriptline 1
#!/usr/bin/env bash
tests/operation_report_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 8
trap 'rm -rf "$tmp"' EXIT - Network accessline 34
[Credential-related source omitted] - Possible obfuscationline 34
[Credential-related source omitted] - Access to secretsline 34
[Credential-related source omitted] - Network accessline 37
domain_mode=route53 \ domain=report.example.test \ as_url=https://report.example.test \ - Network accessline 38
domain=report.example.test \ as_url=https://report.example.test \ instance_type=t3.small \ - Network accessline 39
as_url=https://report.example.test \ - Access to secretsline 42
[Credential-related source omitted] - Network accessline 52
connect_npm_package=dirextalk-connect@latest \ 'server_release={"source":"production_split","version":"v1.1.3","image":"docker.io/dirextalk/message-server:v1.1.3","digest":"sha256:15501d438db03986c9ef045dbff6a184c2a0951963c969a7c2d324ef4d - Network accessline 53
'server_release={"source":"production_split","version":"v1.1.3","image":"docker.io/dirextalk/message-server:v1.1.3","digest":"sha256:15501d438db03986c9ef045dbff6a184c2a0951963c969a7c2d324ef4d59f387","image_ref":"docker.io/dirextalk/message- - Network accessline 54
'split_release={"release_catalog_origin":"https://imadmin.dirextalk.ai","message_version":"v1.1.3","message_image":"docker.io/dirextalk/message-server@sha256:15501d438db03986c9ef045dbff6a184c2a0951963c969a7c2d324ef4d59f387","message_source_ - Network accessline 58
mcp_install_status=host_probe_passed \ mcp_host_probe_status=passed \ mcp_endpoint_url=https://report.example.test/mcp \ - Network accessline 59
mcp_host_probe_status=passed \ mcp_endpoint_url=https://report.example.test/mcp \ mcp_server_name=dirextalk-report-example-test \ - Network accessline 60
mcp_endpoint_url=https://report.example.test/mcp \ - Network accessline 79
json_test_check "$report_path" "data.operation_type === 'new_deploy' && data.status === 'deployment_complete' && data.domain === 'report.example.test' && data.delivery.app_domain === 'report.example.test' && !('service_url' in data.delivery - Possible obfuscationline 79
json_test_check "$report_path" "data.operation_type === 'new_deploy' && data.status === 'deployment_complete' && data.domain === 'report.example.test' && data.delivery.app_domain === 'report.example.test' && !('service_url' in data.delivery
tests/orchestrate_expected_negative_test.sh
tests/orchestrate_lock_test.sh
tests/orchestrate_region_env_test.sh
tests/orchestrate_status_recovery_test.sh
tests/pricing_estimate_test.sh
tests/private_file_permissions_test.sh
tests/production_recovery_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 8
trap 'rm -rf "$tmp"' EXIT - Access to secretsline 38
[Credential-related source omitted] - Access to secretsline 58
[Credential-related source omitted] - Access to secretsline 60
[Credential-related source omitted] - Access to secretsline 61
[Credential-related source omitted] - Access to secretsline 63
[Credential-related source omitted] - Dangerous shell operationline 255
rm -rf "$1.counts" - Dangerous shell operationline 444
cat >"$tmp/fakebin/sudo" <<'EOF' - Dangerous shell operationline 471
*) echo "unexpected sudo consumer command: $command" >&2; exit 90 ;;
tests/production_release_prepare_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 6
trap 'rm -rf "$tmp"' EXIT - Network accessline 32
bundle_sha=$bundle.sha256 cat >"$pin" <<EOF DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Network accessline 33
cat >"$pin" <<EOF DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai DIREXTALK_SPLIT_SOURCE_REVISION=1111111111111111111111111111111111111111 - Network accessline 34
DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Network accessline 58
run_prepare >"$tmp/success.out" grep -Fqx "DIREXTALK_SPLIT_SOURCE_REVISION=$split_revision" "$pin" grep -Fqx 'DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai' "$pin" - Network accessline 59
grep -Fqx "DIREXTALK_SPLIT_SOURCE_REVISION=$split_revision" "$pin" grep -Fqx 'DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai' "$pin" if grep -Eq '^DIREXTALK_(MESSAGE_SERVER|MESSAGE_SOURCE|AGENT_)' "$pin"; then - Network accessline 60
grep -Fqx 'DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai' "$pin" - Network accessline 70
cp "$pin" "$tmp/preserved.env" sed -i 's#https://imadmin.dirextalk.ai#https://invalid.test#' "$pin" - Network accessline 71
sed -i 's#https://imadmin.dirextalk.ai#https://invalid.test#' "$pin"
tests/production_release_resolver_test.mjs
- Executable scriptline 1
Executable file - Network accessline 108
const result = await resolveRepositoryVersion("dirextalk/message-server", good.version, { fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", - Network accessline 109
fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", registryUrl: "https://registry.test", - Network accessline 110
authUrl: "https://auth.test/token", - Network accessline 111
registryUrl: "https://registry.test", - Network accessline 121
const result = await resolveRepository("dirextalk/message-server", { fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", - Network accessline 122
fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", registryUrl: "https://registry.test", - Network accessline 123
authUrl: "https://auth.test/token", - Network accessline 124
registryUrl: "https://registry.test", - Network accessline 161
const result = await resolveProductionRelease({ fetchImpl, authUrl: "https://auth.test/token", - Network accessline 162
fetchImpl, authUrl: "https://auth.test/token", registryUrl: "https://registry.test", - Network accessline 163
authUrl: "https://auth.test/token", - Network accessline 164
registryUrl: "https://registry.test", - Network accessline 178
await assert.rejects(() => resolveRepository("dirextalk/message-server", { fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", - Network accessline 179
fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", registryUrl: "https://registry.test", - Network accessline 180
authUrl: "https://auth.test/token", - Network accessline 181
registryUrl: "https://registry.test", - Network accessline 187
await assert.rejects(() => resolveRepository("dirextalk/message-server", { fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", - Network accessline 188
fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", registryUrl: "https://registry.test", - Network accessline 189
authUrl: "https://auth.test/token", - Network accessline 190
registryUrl: "https://registry.test", - Network accessline 196
await assert.rejects(() => resolveRepository("dirextalk/message-server", { fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", - Network accessline 197
fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", registryUrl: "https://registry.test", - Network accessline 198
authUrl: "https://auth.test/token", - Network accessline 199
registryUrl: "https://registry.test", - Network accessline 206
await assert.rejects(() => resolveRepository("dirextalk/message-server", { fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", - Network accessline 207
fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", registryUrl: "https://registry.test", - Network accessline 208
authUrl: "https://auth.test/token", - Network accessline 209
registryUrl: "https://registry.test", - Network accessline 216
await assert.rejects(() => resolveRepository("dirextalk/message-server", { fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", - Network accessline 217
fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", registryUrl: "https://registry.test", - Network accessline 218
authUrl: "https://auth.test/token", - Network accessline 219
registryUrl: "https://registry.test", - Network accessline 226
const result = await resolveRepository("dirextalk/message-server", { fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", - Network accessline 227
fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", registryUrl: "https://registry.test", - Network accessline 228
authUrl: "https://auth.test/token", - Network accessline 229
registryUrl: "https://registry.test", - Network accessline 237
await assert.rejects(() => resolveRepository("dirextalk/message-server", { fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", - Network accessline 238
fetchImpl: fixture.fetchImpl, authUrl: "https://auth.test/token", registryUrl: "https://registry.test", - Network accessline 239
authUrl: "https://auth.test/token", - Network accessline 240
registryUrl: "https://registry.test",
tests/region_recommendation_test.sh
- Executable scriptline 1
#!/usr/bin/env bash
tests/release_candidate_rollback_test.sh
tests/remote_dns_probe_test.sh
tests/render_userdata_remote_nodes_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 6
trap 'rm -rf "$tmp"' EXIT - Network accessline 28
--split-source-revision "$split_revision" --agent-source-revision "$agent_revision" --release-catalog-origin https://imadmin.dirextalk.ai - Network accessline 29
--agent-source-revision "$agent_revision" --release-catalog-origin https://imadmin.dirextalk.ai ) - Network accessline 30
--release-catalog-origin https://imadmin.dirextalk.ai - Access to secretsline 40
[Credential-related source omitted] - Access to secretsline 41
[Credential-related source omitted] - Network accessline 56
grep -Fq "SPLIT_SOURCE_REVISION=$split_revision" "$rendered" grep -Fq "AGENT_SOURCE_REVISION=$agent_revision" "$rendered" grep -Fq 'DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai' "$rendered" - Network accessline 57
[Credential-related source omitted] - Network accessline 58
grep -Fq 'DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai' "$rendered" - Network accessline 109
if bash "$ROOT/scripts/render/render-userdata.sh" --region ap-east-1 --domain service.example.test --message-server-image dirextalk/message-server:v1.2.3 --agent-image "$agent" --postgres-image "$postgres" --caddy-image "$ - Network accessline 120
--split-source-revision "$split_revision" \ --agent-source-revision "$agent_revision" \ --release-catalog-origin https://imadmin.dirextalk.ai >/dev/null 2>&1; then - Network accessline 121
--agent-source-revision "$agent_revision" \ --release-catalog-origin https://imadmin.dirextalk.ai >/dev/null 2>&1; then echo "split renderer accepted a message-server image that differs from its version" >&2 - Network accessline 122
--release-catalog-origin https://imadmin.dirextalk.ai >/dev/null 2>&1; then - Network accessline 127
if bash "$ROOT/scripts/render/render-userdata.sh" \ "${common[@]}" \ --release-catalog-origin https://example.invalid >/dev/null 2>&1; then - Network accessline 128
"${common[@]}" \ --release-catalog-origin https://example.invalid >/dev/null 2>&1; then echo "split renderer accepted an arbitrary release catalog origin" >&2 - Network accessline 129
--release-catalog-origin https://example.invalid >/dev/null 2>&1; then
tests/root_volume_size_test.sh
tests/route53_zone_required_test.sh
tests/runtime_summary_check_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 8
trap 'rm -rf "$tmp"' EXIT - Network accessline 40
cat > "$fakebin/curl" <<'EOF' - Network accessline 64
case "$args" in *"https://runtime-summary.example.test/mcp"*) - Network accessline 65
*"https://runtime-summary.example.test/mcp"*) - Network accessline 78
;; esac case "$args" in *AGENT_TOKEN_RUNTIME*) echo "token leaked into curl argv" >&2; exit 1 ;; esac - Network accessline 79
esac case "$args" in *AGENT_TOKEN_RUNTIME*) echo "token leaked into curl argv" >&2; exit 1 ;; esac case "$args" in - Network accessline 80
case "$args" in *AGENT_TOKEN_RUNTIME*) echo "token leaked into curl argv" >&2; exit 1 ;; esac - Network accessline 96
;; *) echo "unexpected curl URL: $args" >&2 - Network accessline 97
*) echo "unexpected curl URL: $args" >&2 exit 1 - Network accessline 98
echo "unexpected curl URL: $args" >&2 - Network accessline 119
json_build object run_id=runtime-summary-test region=ap-northeast-1 domain_mode=user domain=runtime-summary.example.test as_url=https://runtime-summary.example.test - Network accessline 122
domain_mode=user \ domain=runtime-summary.example.test \ as_url=https://runtime-summary.example.test \ - Network accessline 123
domain=runtime-summary.example.test \ as_url=https://runtime-summary.example.test \ agent_service_id=runtime-summary.example.test \ - Network accessline 124
as_url=https://runtime-summary.example.test \ - Network accessline 127
"agent_credentials_file=$credentials" \ "mcp_credentials_file=$credentials" \ mcp_endpoint_url=https://runtime-summary.example.test/mcp \ - Network accessline 128
[Credential-related source omitted] - Network accessline 129
mcp_endpoint_url=https://runtime-summary.example.test/mcp \
tests/s1_lightsail_availability_fallback_test.sh
tests/s3_ec2_updater_upload_test.sh
tests/s3_lightsail_provision_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 10
trap 'rm -rf "$tmp"' EXIT - Possible obfuscationline 130
json_test_check "$STATE_JSON" "data.deployment_layout === 'split-agent' && data.cloud_provider === 'lightsail' && data.phases.S3_PROVISION.status === 'done' && data.resources.lightsail_bundle_id === 'medium_3_0' && data.resources.lightsail_ - Network accessline 261
[Credential-related source omitted] - Network accessline 262
[Credential-related source omitted] - Network accessline 263
[Credential-related source omitted]
tests/s3_public_ip_validation_test.sh
tests/s3_stable_ip_reconcile_test.sh
tests/s5_init_tokens_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 8
trap 'rm -rf "$tmp"' EXIT - Network accessline 27
[Credential-related source omitted] - Network accessline 28
[Credential-related source omitted] - Network accessline 29
[Credential-related source omitted] - Access to secretsline 29
[Credential-related source omitted] - Network accessline 30
JSON EOF cat > "$tmp/bin/curl" <<'EOF' - Network accessline 31
EOF cat > "$tmp/bin/curl" <<'EOF' #!/usr/bin/env bash - Network accessline 32
cat > "$tmp/bin/curl" <<'EOF' - Network accessline 40
--data-binary) data=$2; shift 2 ;; --resolve) resolve=$2; shift 2 ;; https://*) url=$1; shift ;; - Network accessline 41
--resolve) resolve=$2; shift 2 ;; https://*) url=$1; shift ;; *) shift ;; - Network accessline 42
https://*) url=$1; shift ;; - Network accessline 46
printf '%s\n' "${args[*]}" >> "$PORTAL_CURL_LOG" case "$url" in https://resume.example.test/.well-known/portal/owner.json) - Network accessline 47
case "$url" in https://resume.example.test/.well-known/portal/owner.json) printf '200' - Network accessline 48
https://resume.example.test/.well-known/portal/owner.json) - Network accessline 49
printf '200' ;; https://resume.example.test/_p2p/command) - Network accessline 50
;; https://resume.example.test/_p2p/command) [ "$resolve" = "resume.example.test:443:203.0.113.10" ] - Network accessline 51
https://resume.example.test/_p2p/command) - Network accessline 57
[Credential-related source omitted] - Network accessline 58
[Credential-related source omitted] - Network accessline 59
[Credential-related source omitted] - Access to secretsline 59
[Credential-related source omitted] - Access to secretsline 89
[Credential-related source omitted] - Network accessline 93
grep -q -- '--data-binary @' "$PORTAL_CURL_LOG" if grep -Eq '12345678|matrix-owner-test|bootstrap-p2p-test|agent-test' "$PORTAL_CURL_LOG"; then echo "S5 portal authentication leaked a credential into curl argv" >&2 - Network accessline 94
if grep -Eq '12345678|matrix-owner-test|bootstrap-p2p-test|agent-test' "$PORTAL_CURL_LOG"; then echo "S5 portal authentication leaked a credential into curl argv" >&2 exit 1 - Network accessline 95
echo "S5 portal authentication leaked a credential into curl argv" >&2 - Access to secretsline 111
[Credential-related source omitted] - Access to secretsline 123
[Credential-related source omitted] - Network accessline 132
cat > "$tmp/bin/curl" <<'EOF' - Access to secretsline 141
[Credential-related source omitted] - Network accessline 149
exec "$@" EOF chmod 700 "$tmp/bin/curl" "$tmp/bin/ssh" "$tmp/bin/timeout" - Network accessline 150
EOF chmod 700 "$tmp/bin/curl" "$tmp/bin/ssh" "$tmp/bin/timeout" hash -r - Network accessline 151
chmod 700 "$tmp/bin/curl" "$tmp/bin/ssh" "$tmp/bin/timeout" - Dangerous shell operationline 178
if grep -q '/opt/p2p/bootstrap.json\|elif sudo test -s' "$SSH_LOG"; then - Access to secretsline 183
[Credential-related source omitted] - Access to secretsline 185
[Credential-related source omitted] - Access to secretsline 186
[Credential-related source omitted] - Access to secretsline 188
[Credential-related source omitted] - Access to secretsline 193
[Credential-related source omitted] - Access to secretsline 213
[Credential-related source omitted] - Access to secretsline 214
[Credential-related source omitted] - Dangerous shell operationline 215
if grep -Fq 'cd /var/dirextalk-message-server && sudo docker compose' "$WARN_LOG"; then - Access to secretsline 229
[Credential-related source omitted] - Access to secretsline 230
[Credential-related source omitted] - Dangerous shell operationline 231
if grep -Fq "sudo cat $DIREXTALK_REMOTE_BOOTSTRAP_FILE" "$WARN_LOG"; then
tests/s6_run_phase_failure_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 16
trap 'rm -rf "$tmp"' EXIT - Network accessline 31
case "$1" in domain) printf 'service.example.test\n' ;; as_url) printf 'https://service.example.test\n' ;; - Network accessline 32
domain) printf 'service.example.test\n' ;; as_url) printf 'https://service.example.test\n' ;; agent_token) printf 'agent-token\n' ;; - Network accessline 33
as_url) printf 'https://service.example.test\n' ;; - Access to secretsline 35
[Credential-related source omitted] - Access to secretsline 47
[Credential-related source omitted] - Network accessline 53
[Credential-related source omitted] - Network accessline 54
[Credential-related source omitted] - Network accessline 55
[Credential-related source omitted] - Access to secretsline 55
[Credential-related source omitted] - Access to secretsline 76
[Credential-related source omitted] - Network accessline 77
device_id) printf 'DEVICE\n' ;; user_id) printf '@agent:service.example.test\n' ;; homeserver) printf 'https://service.example.test\n' ;; - Network accessline 78
user_id) printf '@agent:service.example.test\n' ;; homeserver) printf 'https://service.example.test\n' ;; *) return 1 ;; - Network accessline 79
homeserver) printf 'https://service.example.test\n' ;; - Access to secretsline 163
[Credential-related source omitted] - Network accessline 233
[Credential-related source omitted] - Access to secretsline 233
[Credential-related source omitted] - Network accessline 238
mcp_daemon_install_command=legacy-command \ mcp_daemon_status_command=legacy-status \ mcp_daemon_url=http://127.0.0.1:7331 \ - Network accessline 239
mcp_daemon_status_command=legacy-status \ mcp_daemon_url=http://127.0.0.1:7331 \ mcp_daemon_proxy_command=legacy-proxy \ - Network accessline 240
mcp_daemon_url=http://127.0.0.1:7331 \ - Access to secretsline 246
[Credential-related source omitted] - Network accessline 337
fi if [ "$expect_connect_mcp" = "true" ]; then grep -q '^mcp_url = "https://service.example.test/mcp"' "$config_path" - Network accessline 338
if [ "$expect_connect_mcp" = "true" ]; then grep -q '^mcp_url = "https://service.example.test/mcp"' "$config_path" grep -q "^mcp_capability = \"$expected_capability\"" "$config_path" - Network accessline 339
grep -q '^mcp_url = "https://service.example.test/mcp"' "$config_path" - Access to secretsline 442
[Credential-related source omitted]
tests/s6_wire_local_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 10
trap 'rm -rf "$tmp"' EXIT - Access to secretsline 51
[Credential-related source omitted] - Network accessline 65
[ "$(_dirextalk_home)" = "$HOME/.dirextalk" ] [ "$(DIREXTALK_HOME="$tmp/custom-dirextalk" _dirextalk_home)" = "$tmp/custom-dirextalk" ] [ "$(_dirextalk_service_id "https://Service.Example.test:8443/_p2p")" = "service.example.test-8443" ] - Network accessline 66
[ "$(DIREXTALK_HOME="$tmp/custom-dirextalk" _dirextalk_home)" = "$tmp/custom-dirextalk" ] [ "$(_dirextalk_service_id "https://Service.Example.test:8443/_p2p")" = "service.example.test-8443" ] [ "$(_dirextalk_service_dir "https://Service.Exa - Network accessline 67
[ "$(_dirextalk_service_id "https://Service.Example.test:8443/_p2p")" = "service.example.test-8443" ] - Network accessline 68
[ "$(_dirextalk_service_dir "https://Service.Example.test:8443/_p2p")" = "$HOME/.dirextalk/nodes/service.example.test-8443" ] - Network accessline 72
credentials_file="$tmp/canonical-credentials.json" _write_credentials_file "$credentials_file" service.example.test https://service.example.test agent-token 12345678 access-token '!agents-real:service.example.test' codex-service-example - Network accessline 73
_write_credentials_file "$credentials_file" service.example.test https://service.example.test agent-token 12345678 access-token '!agents-real:service.example.test' codex-service-example - Network accessline 74
[Credential-related source omitted] - Access to secretsline 75
[Credential-related source omitted] - Access to secretsline 141
[Credential-related source omitted] - Network accessline 159
matrix_retry_dir="$tmp/matrix-retry" mkdir -p "$matrix_retry_dir/bin" cat > "$matrix_retry_dir/bin/curl" <<'EOF' - Network accessline 160
mkdir -p "$matrix_retry_dir/bin" cat > "$matrix_retry_dir/bin/curl" <<'EOF' #!/usr/bin/env bash - Network accessline 161
cat > "$matrix_retry_dir/bin/curl" <<'EOF' - Network accessline 191
[Credential-related source omitted] - Network accessline 192
[Credential-related source omitted] - Network accessline 193
[Credential-related source omitted] - Access to secretsline 193
[Credential-related source omitted] - Network accessline 196
EOF chmod 700 "$matrix_retry_dir/bin/curl" MATRIX_RETRY_COUNT="$matrix_retry_dir/count" \ - Network accessline 197
chmod 700 "$matrix_retry_dir/bin/curl" MATRIX_RETRY_COUNT="$matrix_retry_dir/count" \ DIREXTALK_MATRIX_SESSION_CREATE_MAX=2 \ - Network accessline 198
MATRIX_RETRY_COUNT="$matrix_retry_dir/count" DIREXTALK_MATRIX_SESSION_CREATE_MAX=2 DIREXTALK_MATRIX_SESSION_RETRY_INTERVAL=0 PATH="$matrix_retry_dir/bin:$PATH" _create_connect_matrix_session "https://service.example.test" "agent-token - Network accessline 200
DIREXTALK_MATRIX_SESSION_RETRY_INTERVAL=0 \ PATH="$matrix_retry_dir/bin:$PATH" \ _create_connect_matrix_session "https://service.example.test" "agent-token" "DEVICE" "$matrix_retry_dir/session.json" - Network accessline 201
PATH="$matrix_retry_dir/bin:$PATH" \ _create_connect_matrix_session "https://service.example.test" "agent-token" "DEVICE" "$matrix_retry_dir/session.json" [ "$(cat "$matrix_retry_dir/count")" = "2" ] - Network accessline 202
_create_connect_matrix_session "https://service.example.test" "agent-token" "DEVICE" "$matrix_retry_dir/session.json" - Access to secretsline 204
[Credential-related source omitted] - Dangerous shell operationline 206
rm -f "$matrix_retry_dir/count" "$matrix_retry_dir/session.json" - Network accessline 207
MATRIX_RETRY_COUNT="$matrix_retry_dir/count" MATRIX_SUCCESS_AFTER=6 DIREXTALK_MATRIX_SESSION_RETRY_INTERVAL=0 PATH="$matrix_retry_dir/bin:$PATH" _create_connect_matrix_session "https://service.example.test" "agent-token" "DEVICE" "$ma - Network accessline 209
DIREXTALK_MATRIX_SESSION_RETRY_INTERVAL=0 \ PATH="$matrix_retry_dir/bin:$PATH" \ _create_connect_matrix_session "https://service.example.test" "agent-token" "DEVICE" "$matrix_retry_dir/session.json" - Network accessline 210
PATH="$matrix_retry_dir/bin:$PATH" \ _create_connect_matrix_session "https://service.example.test" "agent-token" "DEVICE" "$matrix_retry_dir/session.json" [ "$(cat "$matrix_retry_dir/count")" = "6" ] - Network accessline 211
_create_connect_matrix_session "https://service.example.test" "agent-token" "DEVICE" "$matrix_retry_dir/session.json" - Access to secretsline 213
[Credential-related source omitted] - Network accessline 293
windows_mcp_doctor_command=$(DIREXTALK_LOCAL_PATH_STYLE=windows _mcp_doctor_command "https://service.example.test" "C:/Users/alice/.dirextalk/nodes/im/credentials.json" node-id "C:/Users/alice/.dirextalk/nodes/im") - Network accessline 297
posix_mcp_doctor_command=$(DIREXTALK_LOCAL_PATH_STYLE=posix _mcp_doctor_command "https://service.example.test" "/home/alice/.dirextalk/nodes/im/credentials.json" node-id "/home/alice/.dirextalk/nodes/im") - Network accessline 303
mcp_service_dir="$tmp/mcp-service" mcp_credentials="$mcp_service_dir/credentials.json" expected_mcp_endpoint="https://service.example.test/mcp" - Network accessline 304
mcp_credentials="$mcp_service_dir/credentials.json" expected_mcp_endpoint="https://service.example.test/mcp" for invalid_mcp_origin in http://service.example.test https://service.example.test/mcp 'https://service.example.test?x=1' 'https:// - Network accessline 305
expected_mcp_endpoint="https://service.example.test/mcp" - Network accessline 306
for invalid_mcp_origin in http://service.example.test https://service.example.test/mcp 'https://service.example.test?x=1' 'https://service.example.test#fragment' 'https://user@service.example.test' 'https://bad_host.example.test' 'https://- - Network accessline 323
printf 'stale bearer AGENT_TOKEN_TEST\n' > "$mcp_service_dir/mcp/codex.toml" printf 'stale bearer AGENT_TOKEN_TEST\n' > "$mcp_service_dir/mcp/cursor.mcp.json" _write_mcp_config_artifacts "service.example.test" "$mcp_service_dir" "https://se - Network accessline 324
printf 'stale bearer AGENT_TOKEN_TEST\n' > "$mcp_service_dir/mcp/cursor.mcp.json" _write_mcp_config_artifacts "service.example.test" "$mcp_service_dir" "https://service.example.test" "AGENT_TOKEN_TEST" "$mcp_credentials" "codex-service-exam - Network accessline 325
_write_mcp_config_artifacts "service.example.test" "$mcp_service_dir" "https://service.example.test" "AGENT_TOKEN_TEST" "$mcp_credentials" "codex-service-example" codex - Network accessline 418
mkdir -p "$generic_service_dir" : > "$generic_credentials" _write_mcp_config_artifacts "generic.example.test" "$generic_service_dir" "https://generic.example.test" "GENERIC_TOKEN" "$generic_credentials" "gemini-generic-example" gemini - Network accessline 419
: > "$generic_credentials" _write_mcp_config_artifacts "generic.example.test" "$generic_service_dir" "https://generic.example.test" "GENERIC_TOKEN" "$generic_credentials" "gemini-generic-example" gemini [ ! -e "$generic_service_dir/mcp/mcp- - Network accessline 420
_write_mcp_config_artifacts "generic.example.test" "$generic_service_dir" "https://generic.example.test" "GENERIC_TOKEN" "$generic_credentials" "gemini-generic-example" gemini - Network accessline 429
openclaw_credentials="$openclaw_service_dir/credentials.json" mkdir -p "$openclaw_service_dir" _write_credentials_file "$openclaw_credentials" openclaw.example.test https://openclaw.example.test OPENCLAW_TOKEN 12345678 owner-token '!agents- - Network accessline 430
mkdir -p "$openclaw_service_dir" _write_credentials_file "$openclaw_credentials" openclaw.example.test https://openclaw.example.test OPENCLAW_TOKEN 12345678 owner-token '!agents-real:openclaw.example.test' openclaw-node _write_mcp_config_ar - Network accessline 431
_write_credentials_file "$openclaw_credentials" openclaw.example.test https://openclaw.example.test OPENCLAW_TOKEN 12345678 owner-token '!agents-real:openclaw.example.test' openclaw-node - Network accessline 432
_write_mcp_config_artifacts "openclaw.example.test" "$openclaw_service_dir" "https://openclaw.example.test" "OPENCLAW_TOKEN" "$openclaw_credentials" "openclaw-node" openclaw - Network accessline 435
[ ! -e "$openclaw_service_dir/mcp/mcp-servers.json" ] grep -q 'host-managed' "$openclaw_service_dir/mcp/openclaw.md" grep -q 'https://openclaw.example.test/mcp' "$openclaw_service_dir/mcp/openclaw.md" - Network accessline 436
grep -q 'host-managed' "$openclaw_service_dir/mcp/openclaw.md" grep -q 'https://openclaw.example.test/mcp' "$openclaw_service_dir/mcp/openclaw.md" grep -Fq "$openclaw_credentials" "$openclaw_service_dir/mcp/openclaw.md" - Network accessline 437
grep -q 'https://openclaw.example.test/mcp' "$openclaw_service_dir/mcp/openclaw.md" - Network accessline 444
[ "$(HERMES_HOME="$hermes_service_dir/hermes" DIREXTALK_HERMES_MCP_HOME="$hermes_service_dir/hermes" _mcp_hermes_home "$hermes_service_dir")" = "$hermes_service_dir/hermes" ] [ "$(DIREXTALK_LOCAL_PATH_STYLE=windows LOCALAPPDATA='C:/Users/al - Network accessline 445
[ "$(DIREXTALK_LOCAL_PATH_STYLE=windows LOCALAPPDATA='C:/Users/alice/AppData/Local' HERMES_HOME='C:/Users/alice/.dirextalk/nodes/im/hermes' _mcp_hermes_home 'C:/Users/alice/.dirextalk/nodes/im')" = 'C:/Users/alice/AppData/Local/hermes' ] _w - Network accessline 446
_write_credentials_file "$hermes_credentials" hermes.example.test https://hermes.example.test HERMES_TOKEN 12345678 owner-token '!agents-real:hermes.example.test' hermes-node - Network accessline 447
_write_mcp_config_artifacts "hermes.example.test" "$hermes_service_dir" "https://hermes.example.test" "HERMES_TOKEN" "$hermes_credentials" "hermes-node" hermes host-managed - Access to secretsline 484
[Credential-related source omitted] - Access to secretsline 552
[Credential-related source omitted] - Access to secretsline 553
[Credential-related source omitted] - Dangerous shell operationline 564
rm -f "$tmp/hermes-confirmed-calls.log" - Network accessline 621
fi grep -q 'mcp_install_status=unsupported' "$tmp/unsupported-state-calls.log" mcp_install_command=$(_mcp_install_command "https://service.example.test" "$mcp_service_dir") - Network accessline 622
grep -q 'mcp_install_status=unsupported' "$tmp/unsupported-state-calls.log" mcp_install_command=$(_mcp_install_command "https://service.example.test" "$mcp_service_dir") [[ "$mcp_install_command" == *"No local MCP CLI install is needed"* ]] - Network accessline 623
mcp_install_command=$(_mcp_install_command "https://service.example.test" "$mcp_service_dir") - Network accessline 624
[[ "$mcp_install_command" == *"No local MCP CLI install is needed"* ]] [[ "$mcp_install_command" == *"https://service.example.test/mcp"* ]] mcp_doctor_command=$(_mcp_doctor_command "https://service.example.test" "$mcp_credentials" "codex-se - Network accessline 625
[[ "$mcp_install_command" == *"https://service.example.test/mcp"* ]] - Network accessline 626
mcp_doctor_command=$(_mcp_doctor_command "https://service.example.test" "$mcp_credentials" "codex-service-example" "$mcp_service_dir") - Network accessline 637
config_path="$tmp/dirextalk-connect/config.toml" _write_connect_config "$config_path" "$tmp/dirextalk-connect/data" "codex-node" "codex" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!agents-r - Network accessline 638
_write_connect_config "$config_path" "$tmp/dirextalk-connect/data" "codex-node" "codex" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!agents-real:service.example.test" "@owner:service.example - Network accessline 659
codex_mcp_connect_config_path="$tmp/dirextalk-connect/config-with-codex-mcp.toml" _write_connect_config "$codex_mcp_connect_config_path" "$tmp/dirextalk-connect/data-codex-mcp" "codex-node" "codex" "$tmp/workspace" "https://service.example. - Network accessline 660
_write_connect_config "$codex_mcp_connect_config_path" "$tmp/dirextalk-connect/data-codex-mcp" "codex-node" "codex" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!agents-real:service.example.t - Network accessline 661
grep -q 'mcp_url = "https://service.example.test/mcp"' "$codex_mcp_connect_config_path" - Network accessline 667
generic_mcp_connect_config_path="$tmp/dirextalk-connect/config-with-generic-mcp.toml" _write_connect_config "$generic_mcp_connect_config_path" "$tmp/dirextalk-connect/data-generic-mcp" "gemini-node" "gemini" "$tmp/workspace" "https://servic - Network accessline 668
_write_connect_config "$generic_mcp_connect_config_path" "$tmp/dirextalk-connect/data-generic-mcp" "gemini-node" "gemini" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!agents-real:service.exa - Network accessline 669
[Credential-related source omitted] - Network accessline 670
grep -q 'mcp_url = "https://service.example.test/mcp"' "$generic_mcp_connect_config_path" - Network accessline 674
openclaw_mcp_connect_config_path="$tmp/dirextalk-connect/config-with-openclaw-mcp.toml" _write_connect_config "$openclaw_mcp_connect_config_path" "$tmp/dirextalk-connect/data-openclaw-mcp" "openclaw-node" "acp" "$tmp/workspace" "https://ser - Network accessline 675
_write_connect_config "$openclaw_mcp_connect_config_path" "$tmp/dirextalk-connect/data-openclaw-mcp" "openclaw-node" "acp" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!agents-real:service.ex - Network accessline 676
args = ["acp", "--session", "agent:main:main"] display_name = "OpenClaw ACP"' "https://service.example.test/mcp" "dirextalk-service_example_test" "agent-token" "openclaw-node" host-managed grep -q 'cmd = "openclaw"' "$openclaw_mcp_connect_c - Network accessline 677
display_name = "OpenClaw ACP"' "https://service.example.test/mcp" "dirextalk-service_example_test" "agent-token" "openclaw-node" host-managed - Network accessline 682
! grep -q '^mcp_servers = ' "$openclaw_mcp_connect_config_path" printf 'preserved host config\n' > "$tmp/dirextalk-connect/host-managed-explicit-mcp.toml" if _write_connect_config "$tmp/dirextalk-connect/host-managed-explicit-mcp.toml" "$tm - Network accessline 683
printf 'preserved host config\n' > "$tmp/dirextalk-connect/host-managed-explicit-mcp.toml" if _write_connect_config "$tmp/dirextalk-connect/host-managed-explicit-mcp.toml" "$tmp/dirextalk-connect/data-host-managed-explicit" "openclaw-node" - Network accessline 684
if _write_connect_config "$tmp/dirextalk-connect/host-managed-explicit-mcp.toml" "$tmp/dirextalk-connect/data-host-managed-explicit" "openclaw-node" "acp" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.exampl - Network accessline 693
conditional_mcp_connect_config_path="$tmp/dirextalk-connect/config-with-conditional-mcp.toml" _write_connect_config "$conditional_mcp_connect_config_path" "$tmp/dirextalk-connect/data-conditional-mcp" "pi-node" "pi" "$tmp/workspace" "https: - Network accessline 694
_write_connect_config "$conditional_mcp_connect_config_path" "$tmp/dirextalk-connect/data-conditional-mcp" "pi-node" "pi" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!agents-real:service.exa - Network accessline 695
grep -q '^mcp_url = "https://service.example.test/mcp"' "$conditional_mcp_connect_config_path" - Network accessline 698
unsupported_mcp_connect_config_path="$tmp/dirextalk-connect/config-with-unsupported-mcp.toml" _write_connect_config "$unsupported_mcp_connect_config_path" "$tmp/dirextalk-connect/data-unsupported-mcp" "reasonix-node" "reasonix" "$tmp/worksp - Network accessline 699
_write_connect_config "$unsupported_mcp_connect_config_path" "$tmp/dirextalk-connect/data-unsupported-mcp" "reasonix-node" "reasonix" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!agents-real - Network accessline 700
grep -q '^mcp_url = "https://service.example.test/mcp"' "$unsupported_mcp_connect_config_path" - Network accessline 703
[Credential-related source omitted] - Network accessline 704
[Credential-related source omitted] - Access to secretsline 704
[Credential-related source omitted] - Network accessline 705
DIREXTALK_SPEECH_BASE_URL=https://stt.example.test/v1 \ - Network accessline 706
DIREXTALK_SPEECH_MODEL=whisper-test \ _write_connect_config "$speech_config_path" "$tmp/dirextalk-connect/data-speech" "codex-node" "codex" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!age - Network accessline 707
_write_connect_config "$speech_config_path" "$tmp/dirextalk-connect/data-speech" "codex-node" "codex" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!agents-real:service.example.test" "@owner:s - Network accessline 712
[Credential-related source omitted] - Network accessline 713
[Credential-related source omitted] - Access to secretsline 713
[Credential-related source omitted] - Network accessline 714
grep -q 'base_url = "https://stt.example.test/v1"' "$speech_config_path" - Network accessline 783
cmd_config_path="$tmp/dirextalk-connect/config-with-cmd.toml" _write_connect_config "$cmd_config_path" "$tmp/dirextalk-connect/data-cmd" "codex-node" "codex" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.exa - Network accessline 784
_write_connect_config "$cmd_config_path" "$tmp/dirextalk-connect/data-cmd" "codex-node" "codex" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!agents-real:service.example.test" "@owner:service - Network accessline 787
options_config_path="$tmp/dirextalk-connect/config-with-extra-options.toml" _write_connect_config "$options_config_path" "$tmp/dirextalk-connect/data-options" "reasonix-node" "reasonix" "$tmp/workspace" "https://service.example.test" "matri - Network accessline 788
_write_connect_config "$options_config_path" "$tmp/dirextalk-connect/data-options" "reasonix-node" "reasonix" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!agents-real:service.example.test" " - Network accessline 789
grep -q 'type = "reasonix"' "$options_config_path" grep -q 'serve_url = "http://127.0.0.1:8080"' "$options_config_path" grep -q 'mode = "yolo"' "$options_config_path" - Network accessline 790
grep -q 'serve_url = "http://127.0.0.1:8080"' "$options_config_path" - Network accessline 794
codex_options_config_path="$tmp/dirextalk-connect/config-with-codex-extra-options.toml" _write_connect_config "$codex_options_config_path" "$tmp/dirextalk-connect/data-codex-options" "codex-node" "codex" "$tmp/workspace" "https://service.ex - Network accessline 795
_write_connect_config "$codex_options_config_path" "$tmp/dirextalk-connect/data-codex-options" "codex-node" "codex" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!agents-real:service.example.t - Access to secretsline 878
[Credential-related source omitted] - Network accessline 998
openclaw_config_path="$tmp/dirextalk-connect/config-openclaw.toml" _write_connect_config "$openclaw_config_path" "$tmp/dirextalk-connect/data-openclaw" "openclaw-node" "$(_connect_agent_type openclaw)" "$tmp/workspace" "https://service.exam - Network accessline 999
_write_connect_config "$openclaw_config_path" "$tmp/dirextalk-connect/data-openclaw" "openclaw-node" "$(_connect_agent_type openclaw)" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!agents-rea - Network accessline 1005
hermes_config_path="$tmp/dirextalk-connect/config-hermes.toml" hermes_adapter_binary="$hermes_service_dir/dirextalk-connect/node_modules/dirextalk-connect/bin/dirextalk-connect" _write_connect_config "$hermes_config_path" "$tmp/dirextalk-co - Network accessline 1006
hermes_adapter_binary="$hermes_service_dir/dirextalk-connect/node_modules/dirextalk-connect/bin/dirextalk-connect" _write_connect_config "$hermes_config_path" "$tmp/dirextalk-connect/data-hermes" "hermes-node" "$(_connect_agent_type hermes) - Network accessline 1007
_write_connect_config "$hermes_config_path" "$tmp/dirextalk-connect/data-hermes" "hermes-node" "$(_connect_agent_type hermes)" "$tmp/workspace" "https://service.example.test" "matrix-token" "@agent:service.example.test" "!agents-real:servic - Network accessline 1014
guidance=$( _print_connect_guidance codex https://service.example.test "$HOME/.dirextalk/nodes/service.example.test/credentials.json" recommend dirextalk-connect "install command" codex-service "$config_path" "$HOME/.dirextalk/nodes/servi - Network accessline 1015
_print_connect_guidance codex https://service.example.test "$HOME/.dirextalk/nodes/service.example.test/credentials.json" recommend dirextalk-connect "install command" codex-service "$config_path" "$HOME/.dirextalk/nodes/service.example.tes - Network accessline 1032
[Credential-related source omitted] - Network accessline 1033
[Credential-related source omitted] - Network accessline 1034
[Credential-related source omitted] - Network accessline 1036
mcp_guidance=$( DIREXTALK_MCP_CONFIG_CONFLICT_PATHS="$stale_mcp_config" \ _print_mcp_guidance codex service.example.test dirextalk-service_example_test "$mcp_credentials" "$mcp_service_dir/mcp" none "" "$mcp_install_command" "$mcp_doc - Network accessline 1037
DIREXTALK_MCP_CONFIG_CONFLICT_PATHS="$stale_mcp_config" _print_mcp_guidance codex service.example.test dirextalk-service_example_test "$mcp_credentials" "$mcp_service_dir/mcp" none "" "$mcp_install_command" "$mcp_doctor_command" "$mcp_ - Network accessline 1038
_print_mcp_guidance codex service.example.test dirextalk-service_example_test "$mcp_credentials" "$mcp_service_dir/mcp" none "" "$mcp_install_command" "$mcp_doctor_command" "$mcp_service_dir" "https://service.example.test/mcp" 2>&1 >/dev/nu
tests/s7_http_mcp_acceptance_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 8
trap 'rm -rf "$tmp"' EXIT - Network accessline 42
cat > "$fakebin/curl" <<'EOF' - Network accessline 90
for arg in "$@"; do case "$arg" in https://*) url=$arg ;; - Network accessline 91
case "$arg" in https://*) url=$arg ;; esac - Network accessline 92
https://*) url=$arg ;; - Network accessline 97
code=200 case "$url" in https://s7-mcp.example.test/_p2p/health) - Network accessline 98
case "$url" in https://s7-mcp.example.test/_p2p/health) body='{"status":"ok"}' - Network accessline 99
https://s7-mcp.example.test/_p2p/health) - Network accessline 100
body='{"status":"ok"}' ;; https://s7-mcp.example.test/_matrix/client/versions) - Network accessline 101
;; https://s7-mcp.example.test/_matrix/client/versions) body='{"versions":["v1.0"]}' - Network accessline 102
https://s7-mcp.example.test/_matrix/client/versions) - Network accessline 103
body='{"versions":["v1.0"]}' ;; https://s7-mcp.example.test/.well-known/matrix/server) - Network accessline 104
;; https://s7-mcp.example.test/.well-known/matrix/server) body='{"m.server":"s7-mcp.example.test:443"}' - Network accessline 105
https://s7-mcp.example.test/.well-known/matrix/server) - Network accessline 106
body='{"m.server":"s7-mcp.example.test:443"}' ;; https://s7-mcp.example.test/.well-known/portal/owner.json) - Network accessline 107
;; https://s7-mcp.example.test/.well-known/portal/owner.json) body='{"ok":true}' - Network accessline 108
https://s7-mcp.example.test/.well-known/portal/owner.json) - Network accessline 109
body='{"ok":true}' [ -n "$header_path" ] && printf 'HTTP/1.1 200 OK\r\nAccess-Control-Allow-Origin: http://127.0.0.1:51820\r\n\r\n' > "$header_path" ;; - Network accessline 110
[ -n "$header_path" ] && printf 'HTTP/1.1 200 OK\r\nAccess-Control-Allow-Origin: http://127.0.0.1:51820\r\n\r\n' > "$header_path" - Network accessline 111
;; https://s7-mcp.example.test/_p2p/command) echo "S7 TURN acceptance must not rotate the owner portal session" >&2 - Network accessline 112
https://s7-mcp.example.test/_p2p/command) - Network accessline 114
exit 1 ;; https://s7-mcp.example.test/_matrix/client/v3/voip/turnServer) - Network accessline 115
;; https://s7-mcp.example.test/_matrix/client/v3/voip/turnServer) case "$secret_headers" in - Network accessline 116
https://s7-mcp.example.test/_matrix/client/v3/voip/turnServer) - Network accessline 121
[Credential-related source omitted] - Network accessline 122
;; https://s7-mcp.example.test/mcp) case " $secret_headers $request_body " in - Network accessline 123
https://s7-mcp.example.test/mcp) - Network accessline 139
;; *) echo "unexpected curl URL: $url" >&2 - Network accessline 140
*) echo "unexpected curl URL: $url" >&2 exit 1 - Network accessline 141
echo "unexpected curl URL: $url" >&2 - Network accessline 165
[Credential-related source omitted] - Access to secretsline 165
[Credential-related source omitted] - Network accessline 170
domain=s7-mcp.example.test \ domain_confirmed_irreversible=true \ as_url=https://s7-mcp.example.test \ - Network accessline 171
domain_confirmed_irreversible=true \ as_url=https://s7-mcp.example.test \ mcp_endpoint_url=https://s7-mcp.example.test/mcp \ - Network accessline 172
as_url=https://s7-mcp.example.test \ - Network accessline 173
mcp_endpoint_url=https://s7-mcp.example.test/mcp \ - Access to secretsline 175
[Credential-related source omitted] - Network accessline 195
exit 1 fi grep -q 'https://s7-mcp.example.test/mcp' "$calls" - Network accessline 196
fi grep -q 'https://s7-mcp.example.test/mcp' "$calls" if grep -q 'AGENT_TOKEN_S7\|OWNER_ACCESS\|12345678' "$calls"; then - Network accessline 197
grep -q 'https://s7-mcp.example.test/mcp' "$calls" - Network accessline 198
if grep -q 'AGENT_TOKEN_S7\|OWNER_ACCESS\|12345678' "$calls"; then echo "S7 secrets must not appear in curl argv" >&2 exit 1 - Network accessline 199
echo "S7 secrets must not appear in curl argv" >&2 - Network accessline 203
*MINGW*|*MSYS*|*CYGWIN*) if grep -Eq '(^|[[:space:]])(@?/tmp/|/dev/null([[:space:]]|$))' "$calls"; then echo "S7 must convert Git Bash temp/null arguments before invoking native curl" >&2 - Network accessline 204
if grep -Eq '(^|[[:space:]])(@?/tmp/|/dev/null([[:space:]]|$))' "$calls"; then echo "S7 must convert Git Bash temp/null arguments before invoking native curl" >&2 exit 1 - Network accessline 205
echo "S7 must convert Git Bash temp/null arguments before invoking native curl" >&2
tests/server_release_test.sh
tests/skill_structure_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 271
if grep -R -n -E '(^|[^[:alnum:]_])([a-z0-9-]+\.)*dirextalk\.ai([^[:alnum:]_]|$)' SKILL.md references scripts \ | sed 's#https://imadmin\.dirextalk\.ai#__DIREXTALK_RELEASE_CATALOG_ORIGIN__#g' \ - Network accessline 272
| sed 's#https://imadmin\.dirextalk\.ai#__DIREXTALK_RELEASE_CATALOG_ORIGIN__#g' \ - Network accessline 278
grep -Fqx 'DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai' scripts/cloud-init/split/release.env - Network accessline 284
grep -Fq 'https://deployer.dirextalk.ai/' README.md - Network accessline 285
grep -Fq 'https://github.com/YingSuiAI/dirextalk-deployer' README.md - Network accessline 286
grep -Fq 'https://dirextalk.ai/' README.md - Network accessline 440
grep -q 'AWS official real-time policy prevails' README.md grep -q 'AWS official real-time policy prevails' references/deployment-workflow.md grep -q 'Read https://github.com/YingSuiAI/dirextalk-deployer README and follow its npm install ru - Network accessline 441
grep -q 'AWS official real-time policy prevails' references/deployment-workflow.md grep -q 'Read https://github.com/YingSuiAI/dirextalk-deployer README and follow its npm install rule' README.md grep -q 'should run the npm install commands - Network accessline 442
grep -q 'Read https://github.com/YingSuiAI/dirextalk-deployer README and follow its npm install rule' README.md - Network accessline 443
grep -q 'should run the npm install commands below' README.md grep -q 'do not use a generic GitHub skill installer' SKILL.md grep -q 'Read https://github.com/YingSuiAI/dirextalk-deployer README and follow its npm install rule' references/ag - Network accessline 444
grep -q 'do not use a generic GitHub skill installer' SKILL.md grep -q 'Read https://github.com/YingSuiAI/dirextalk-deployer README and follow its npm install rule' references/agent-targets.md grep -q 'DIREXTALK_CLOUD_PROVIDER=lightsail' SK - Network accessline 445
grep -q 'Read https://github.com/YingSuiAI/dirextalk-deployer README and follow its npm install rule' references/agent-targets.md
tests/split-runtime/agent-runtime-local.test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 27
rm -rf -- "$tmp_dir" - Access to secretsline 57
[Credential-related source omitted] - Access to secretsline 60
[Credential-related source omitted] - Access to secretsline 61
[Credential-related source omitted] - Access to secretsline 62
[Credential-related source omitted] - Access to secretsline 71
[Credential-related source omitted] - Access to secretsline 72
[Credential-related source omitted] - Dangerous shell operationline 121
rm -f -- "$DIREXTALK_FAKE_STATE/restart-policy-race" - Access to secretsline 245
[Credential-related source omitted] - Access to secretsline 246
[Credential-related source omitted] - Access to secretsline 247
[Credential-related source omitted] - Access to secretsline 250
[Credential-related source omitted] - Dangerous shell operationline 280
rm -f -- "$fixture/state/restart-policy-race" - Dangerous shell operationline 298
rm -f -- "$fixture/state/restart-policy-race" "$fixture/state/settle-"* - Dangerous shell operationline 358
rm -f -- "$fixture/state/settle-"* - Dangerous shell operationline 373
rm -f -- "$fixture/state/settle-"* - Dangerous shell operationline 430
rm -f -- "$fixture/state/prepare-failed-once" "$fixture/state/start-"*-failed-once - Dangerous shell operationline 449
rm -f -- "$fixture/state/prepare-failed-once" "$fixture/state/start-"*-failed-once
tests/split-runtime/cleanup-local.test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 20
trap 'rm -rf -- "$tmp_dir"' EXIT - Network accessline 45
local fixture=$1 local tls_mode=${2:-edge-terminated} server_name=${3:-chat.example.test} local client_base_url=https://$server_name - Network accessline 46
local tls_mode=${2:-edge-terminated} server_name=${3:-chat.example.test} local client_base_url=https://$server_name local env_file manifest receipt master_key env_identity manifest_identity - Network accessline 47
local client_base_url=https://$server_name - Access to secretsline 48
[Credential-related source omitted] - Access to secretsline 54
[Credential-related source omitted] - Access to secretsline 55
[Credential-related source omitted] - Access to secretsline 56
[Credential-related source omitted] - Access to secretsline 67
[Credential-related source omitted] - Access to secretsline 68
[Credential-related source omitted] - Access to secretsline 80
[Credential-related source omitted] - Access to secretsline 106
[Credential-related source omitted] - Access to secretsline 108
[Credential-related source omitted] - Access to secretsline 113
[Credential-related source omitted] - Access to secretsline 114
[Credential-related source omitted] - Access to secretsline 115
[Credential-related source omitted] - Access to secretsline 116
[Credential-related source omitted] - Access to secretsline 173
[Credential-related source omitted] - Access to secretsline 308
[Credential-related source omitted] - Access to secretsline 315
[Credential-related source omitted] - Dangerous shell operationline 340
grep -Eq '^container rm -f [0-9a-f]{64}$' "$fixture/state/docker.log" - Dangerous shell operationline 341
grep -Eq '^network rm [0-9a-f]{64}$' "$fixture/state/docker.log" - Dangerous shell operationline 342
if grep -Eq '^volume rm ' "$fixture/state/docker.log"; then - Dangerous shell operationline 362
if grep -Fqx "network rm $missing_network_id" "$missing_fixture/state/docker.log" || grep -Fqx "volume rm $missing_volume_name" "$missing_fixture/state/docker.log"; then - Dangerous shell operationline 417
[ "$(grep -c '^volume rm ' "$purge_fixture/state/docker.log")" -eq "${#volume_suffixes[@]}" ] - Dangerous shell operationline 511
grep -Eq '^container rm -f [0-9a-f]{64}$' "$starting_wrapper_fixture/state/docker.log"
tests/split-runtime/cleanup-provision-failure.test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 12
trap 'rm -rf -- "$tmp"' EXIT - Access to secretsline 44
[Credential-related source omitted] - Access to secretsline 56
[Credential-related source omitted] - Access to secretsline 58
[Credential-related source omitted] - Access to secretsline 223
[Credential-related source omitted] - Access to secretsline 224
[Credential-related source omitted] - Access to secretsline 225
[Credential-related source omitted]
tests/split-runtime/compose-runner-limits.test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 10
rm -rf -- "$run_dir" - Network accessline 19
DIREXTALK_MESSAGE_TLS_MODE=edge-terminated DIREXTALK_MESSAGE_SERVER_NAME=message.example.com DIREXTALK_MESSAGE_CLIENT_BASE_URL=https://message.example.com - Network accessline 20
DIREXTALK_MESSAGE_SERVER_NAME=message.example.com DIREXTALK_MESSAGE_CLIENT_BASE_URL=https://message.example.com DIREXTALK_TURN_EXTERNAL_IP=203.0.113.10 - Network accessline 21
DIREXTALK_MESSAGE_CLIENT_BASE_URL=https://message.example.com - Network accessline 44
[ "$(grep -c '^core_cloud_worker_host_region:' "$run_dir/provision/agent-config.yaml")" -eq 1 ] grep -Fqx 'core_message_mcp_enabled: true' "$run_dir/provision/agent-config.yaml" grep -Fqx 'core_message_mcp_endpoint: http://message-server:80 - Network accessline 45
grep -Fqx 'core_message_mcp_enabled: true' "$run_dir/provision/agent-config.yaml" grep -Fqx 'core_message_mcp_endpoint: http://message-server:8008/mcp' "$run_dir/provision/agent-config.yaml" grep -Fqx 'core_message_mcp_token_file: /run/secr - Network accessline 46
grep -Fqx 'core_message_mcp_endpoint: http://message-server:8008/mcp' "$run_dir/provision/agent-config.yaml" - Access to secretsline 49
[Credential-related source omitted] - Access to secretsline 51
[Credential-related source omitted] - Access to secretsline 69
[Credential-related source omitted] - Access to secretsline 77
[Credential-related source omitted]
tests/split-runtime/ensure-host-null-device.test.sh
- Executable scriptline 1
#!/usr/bin/env bash
tests/split-runtime/initialize-capability-ca.test.sh
tests/split-runtime/initialize-message-server.test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 7
trap 'rm -rf -- "$tmp_dir"' EXIT - Network accessline 19
#!/bin/sh set -eu printf '%s\n' 'global:' ' database:' ' connection_string: __DIREXTALK_DB_DSN__' ' well_known_client_name: "http://invalid"' - Network accessline 20
set -eu printf '%s\n' 'global:' ' database:' ' connection_string: __DIREXTALK_DB_DSN__' ' well_known_client_name: "http://invalid"' printf '%s\n' 'client_api:' ' turn:' ' turn_user_lifetime: "5m"' ' turn_uris:' ' turn_shared_ - Network accessline 21
printf '%s\n' 'global:' ' database:' ' connection_string: __DIREXTALK_DB_DSN__' ' well_known_client_name: "http://invalid"' - Network accessline 35
MESSAGE_CONFIG_DIR=$root/config MESSAGE_DATA_DIR=$root/data MESSAGE_REGISTRATION_SECRET_FILE=$tmp_dir/registration-secret MESSAGE_TURN_SHARED_SECRET_FILE=$tmp_dir/turn-secret MESSAGE_GENERATE_KEYS_BINARY=$tmp_dir/bin/generate-ke - Network accessline 46
MESSAGE_DEPLOYMENT_MODE=$deployment \ MESSAGE_SERVER_NAME=message.example.com \ MESSAGE_CLIENT_BASE_URL=https://message.example.com \ - Network accessline 47
MESSAGE_SERVER_NAME=message.example.com \ MESSAGE_CLIENT_BASE_URL=https://message.example.com \ MESSAGE_LOCAL_BOOTSTRAP_ENABLED=false \ - Network accessline 48
MESSAGE_CLIENT_BASE_URL=https://message.example.com \ - Network accessline 55
[ ! -e "$edge_root/config/server.crt" ] [ ! -e "$edge_root/config/server.key" ] grep -Fq 'well_known_client_name: "https://message.example.com"' "$edge_root/config/message-server.yaml" - Network accessline 56
[ ! -e "$edge_root/config/server.key" ] grep -Fq 'well_known_client_name: "https://message.example.com"' "$edge_root/config/message-server.yaml" grep -Fq ' turn_user_lifetime: "24h"' "$edge_root/config/message-server.yaml" - Network accessline 57
grep -Fq 'well_known_client_name: "https://message.example.com"' "$edge_root/config/message-server.yaml"
tests/split-runtime/initialize-postgres.test.sh
tests/split-runtime/manage-runner-apparmor.test.sh
tests/split-runtime/message-server-entrypoint.test.sh
tests/split-runtime/message-server-healthcheck.test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 9
compose_file=$script_dir/../compose.yaml grep -Fqx ' init: true' <(sed -n '/^ message-server:/,/^ [a-zA-Z].*:/p' "$compose_file") grep -Fq 'test: ["CMD", "wget", "-Y", "off", "-q", "-O", "-", "http://127.0.0.1:8008/_p2p/health"]' "$com - Network accessline 11
grep -Fq 'test: ["CMD", "wget", "-Y", "off", "-q", "-O", "-", "http://127.0.0.1:8008/_p2p/health"]' "$compose_file" - Dangerous shell operationline 25
docker rm "$container_id" >/dev/null 2>&1 || true
tests/split-runtime/postgres-entrypoint.docker.test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 23
docker container rm -f "$container" >/dev/null 2>&1 || true - Dangerous shell operationline 31
docker volume rm "$volume" >/dev/null 2>&1 || true - Dangerous shell operationline 36
rm -rf -- "$tmp" - Possible obfuscationline 47
docker run -d --name "$container" --label "io.dirextalk.test-id=$test_id" --read-only --cap-drop ALL --cap-add CHOWN --cap-add FOWNER --cap-add DAC_OVERRIDE --cap-add SETUID --cap-add SETGID --security-opt no-n
tests/split-runtime/prepare-host-dependencies.test.sh
tests/split-runtime/prepare-runner-cgroups.test.sh
tests/split-runtime/refresh-message-mcp-token.test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 7
cleanup() { rm -rf -- "$tmp"; } - Access to secretsline 24
[Credential-related source omitted] - Access to secretsline 34
[Credential-related source omitted] - Access to secretsline 81
[Credential-related source omitted] - Access to secretsline 88
[Credential-related source omitted] - Access to secretsline 95
[Credential-related source omitted] - Access to secretsline 96
[Credential-related source omitted] - Access to secretsline 118
[Credential-related source omitted] - Access to secretsline 128
[Credential-related source omitted] - Access to secretsline 141
[Credential-related source omitted]
tests/split-runtime/update-agent-local.docker.test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 22
docker container rm -f "$server_container" >/dev/null 2>&1 || true - Dangerous shell operationline 23
docker volume rm "$extension_socket_volume" "$core_socket_volume" >/dev/null 2>&1 || true - Dangerous shell operationline 24
rm -rf "$tmp" - Network accessline 43
DIREXTALK_AGENT_INSTANCE_ID=11111111-1111-4111-8111-111111111111 DIREXTALK_MESSAGE_SERVER_INSTANCE_ID=22222222-2222-4222-8222-222222222222 DIREXTALK_MESSAGE_CLIENT_BASE_URL=https://localhost - Network accessline 44
DIREXTALK_MESSAGE_SERVER_INSTANCE_ID=22222222-2222-4222-8222-222222222222 DIREXTALK_MESSAGE_CLIENT_BASE_URL=https://localhost DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Network accessline 45
DIREXTALK_MESSAGE_CLIENT_BASE_URL=https://localhost - Network accessline 46
DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai
tests/split-runtime/update-agent-local.recovery.test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 7
cleanup() { rm -rf "$tmp"; } - Dangerous shell operationline 112
rm) log "image rm ${3:-}" ;; - Access to secretsline 158
[Credential-related source omitted] - Access to secretsline 159
[Credential-related source omitted] - Access to secretsline 160
[Credential-related source omitted] - Access to secretsline 165
[Credential-related source omitted] - Access to secretsline 166
[Credential-related source omitted] - Access to secretsline 228
[Credential-related source omitted] - Access to secretsline 242
[Credential-related source omitted] - Access to secretsline 243
[Credential-related source omitted] - Access to secretsline 244
[Credential-related source omitted] - Access to secretsline 355
[Credential-related source omitted] - Access to secretsline 361
[Credential-related source omitted] - Access to secretsline 362
[Credential-related source omitted] - Access to secretsline 363
[Credential-related source omitted] - Access to secretsline 364
[Credential-related source omitted] - Access to secretsline 370
[Credential-related source omitted] - Access to secretsline 371
[Credential-related source omitted] - Access to secretsline 374
[Credential-related source omitted] - Access to secretsline 375
[Credential-related source omitted] - Access to secretsline 414
[Credential-related source omitted] - Access to secretsline 423
[Credential-related source omitted] - Access to secretsline 424
[Credential-related source omitted] - Access to secretsline 425
[Credential-related source omitted] - Access to secretsline 440
[Credential-related source omitted] - Access to secretsline 469
[Credential-related source omitted] - Access to secretsline 481
[Credential-related source omitted] - Access to secretsline 487
[Credential-related source omitted] - Access to secretsline 497
[Credential-related source omitted] - Access to secretsline 504
[Credential-related source omitted] - Access to secretsline 528
[Credential-related source omitted] - Access to secretsline 537
[Credential-related source omitted] - Access to secretsline 560
[Credential-related source omitted] - Access to secretsline 566
[Credential-related source omitted] - Access to secretsline 571
[Credential-related source omitted] - Access to secretsline 578
[Credential-related source omitted]
tests/split-runtime/update-agent-local.test.sh
tests/split-runtime/update-message-server-local.rollback.test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 7
trap 'rm -rf -- "$tmp"' EXIT - Access to secretsline 19
[Credential-related source omitted] - Access to secretsline 42
[Credential-related source omitted] - Access to secretsline 43
[Credential-related source omitted] - Access to secretsline 99
[Credential-related source omitted]
tests/split-runtime/update-message-server-local.test.sh
- Executable scriptline 1
#!/usr/bin/env bash
tests/split-runtime/verify-production-images.test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 4
tmp=$(mktemp -d); trap 'rm -rf "$tmp"' EXIT - Access to secretsline 6
[Credential-related source omitted] - Access to secretsline 18
[Credential-related source omitted] - Access to secretsline 33
[Credential-related source omitted] - Access to secretsline 34
[Credential-related source omitted] - Access to secretsline 35
[Credential-related source omitted] - Access to secretsline 36
[Credential-related source omitted]
tests/split_agent_bundle_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 6
trap 'rm -rf "$TEST_TMP"' EXIT - Network accessline 117
fi grep -Fq 'P2P_PRODUCT_CAPABILITY_LISTEN_ADDR: :50053' "$repository_compose" grep -Fq 'P2P_AGENT_VERSION_URL: http://agent:8082/agent/v1/health' "$repository_compose" - Network accessline 118
grep -Fq 'P2P_PRODUCT_CAPABILITY_LISTEN_ADDR: :50053' "$repository_compose" grep -Fq 'P2P_AGENT_VERSION_URL: http://agent:8082/agent/v1/health' "$repository_compose" grep -Fq 'expose: ["50053"]' "$repository_compose" - Network accessline 119
grep -Fq 'P2P_AGENT_VERSION_URL: http://agent:8082/agent/v1/health' "$repository_compose" - Access to secretsline 173
[Credential-related source omitted] - Access to secretsline 273
[Credential-related source omitted] - Network accessline 284
AGENT_SOURCE_REVISION=bbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbb DIREXTALK_CLOUD_WORKER_HOST_REGION=ap-east-1 DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Network accessline 285
DIREXTALK_CLOUD_WORKER_HOST_REGION=ap-east-1 DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai EOF - Network accessline 286
DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Access to secretsline 288
[Credential-related source omitted] - Network accessline 351
grep -Fqx 'turn_external_ip=203.0.113.91' "$capture" grep -Fqx 'cloud_worker_host_region=ap-east-1' "$capture" grep -Fqx 'catalog_origin=https://imadmin.dirextalk.ai' "$capture" - Network accessline 352
grep -Fqx 'cloud_worker_host_region=ap-east-1' "$capture" grep -Fqx 'catalog_origin=https://imadmin.dirextalk.ai' "$capture" [ ! -e "$fresh/image-attestation" ] - Network accessline 353
grep -Fqx 'catalog_origin=https://imadmin.dirextalk.ai' "$capture" - Dangerous shell operationline 362
rm -f "$capture" "$fresh/runner-preparation.env" "$fresh/split-stack-name" "$fresh/.split-bootstrap-stage" - Access to secretsline 425
[Credential-related source omitted] - Network accessline 435
SPLIT_SOURCE_REVISION=cccccccccccccccccccccccccccccccccccccccc AGENT_SOURCE_REVISION=bbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbb DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Network accessline 436
AGENT_SOURCE_REVISION=bbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbbb DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai EOF - Network accessline 437
DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Access to secretsline 439
[Credential-related source omitted] - Access to secretsline 457
[Credential-related source omitted] - Access to secretsline 466
[Credential-related source omitted] - Access to secretsline 467
[Credential-related source omitted] - Access to secretsline 473
[Credential-related source omitted] - Access to secretsline 474
[Credential-related source omitted]
tests/split_runtime_contract_test.sh
tests/split_runtime_docker_test.sh
tests/split_source_revision_advance_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 7
trap 'rm -rf "$tmp"' EXIT - Network accessline 45
[ ! -e "$tmp/release.env" ] || chmod 0600 "$tmp/release.env" cat >"$tmp/release.env" <<EOF DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Network accessline 46
cat >"$tmp/release.env" <<EOF DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai DIREXTALK_MESSAGE_SERVER_IMAGE=$message_image - Network accessline 47
DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Network accessline 59
[Credential-related source omitted] - Access to secretsline 59
[Credential-related source omitted] - Network accessline 60
DOMAIN=service.example.test DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai MESSAGE_SERVER_IMAGE=$message_image - Network accessline 61
DIREXTALK_RELEASE_CATALOG_ORIGIN=https://imadmin.dirextalk.ai - Access to secretsline 71
[Credential-related source omitted] - Access to secretsline 77
[Credential-related source omitted] - Access to secretsline 78
[Credential-related source omitted] - Access to secretsline 79
[Credential-related source omitted] - Access to secretsline 80
[Credential-related source omitted] - Access to secretsline 81
[Credential-related source omitted] - Access to secretsline 82
[Credential-related source omitted] - Access to secretsline 86
[Credential-related source omitted] - Access to secretsline 87
[Credential-related source omitted] - Access to secretsline 88
[Credential-related source omitted] - Access to secretsline 89
[Credential-related source omitted] - Access to secretsline 90
[Credential-related source omitted] - Access to secretsline 94
[Credential-related source omitted] - Access to secretsline 97
[Credential-related source omitted] - Access to secretsline 98
[Credential-related source omitted] - Access to secretsline 119
[Credential-related source omitted] - Access to secretsline 120
[Credential-related source omitted] - Access to secretsline 150
[Credential-related source omitted]
tests/split_stack_fault_gate_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 48
docker container rm -f "$container" >/dev/null 2>&1 || true - Dangerous shell operationline 53
rm -rf -- "$tmp" - Dangerous shell operationline 79
rm -f "$tmp/message.ready" - Dangerous shell operationline 85
rm -f "$tmp/agent.ready" - Network accessline 102
start_agent sed \ -e "s#__DIREXTALK_PUBLIC_DOMAIN__#https://localhost:$edge_port#g" \ - Network accessline 103
sed -e "s#__DIREXTALK_PUBLIC_DOMAIN__#https://localhost:$edge_port#g" - Network accessline 104
-e "s#__DIREXTALK_PUBLIC_DOMAIN__#https://localhost:$edge_port#g" \ - Network accessline 135
done [ -s "$root_cert" ] || { docker logs "$container" >&2; echo 'Caddy test CA was not created' >&2; exit 1; } base=https://localhost:$edge_port - Network accessline 136
[ -s "$root_cert" ] || { docker logs "$container" >&2; echo 'Caddy test CA was not created' >&2; exit 1; } base=https://localhost:$edge_port curl_args=(--cacert "$root_cert" --silent --show-error --connect-timeout 2 --max-time 5) - Network accessline 137
base=https://localhost:$edge_port - Network accessline 138
curl_args=(--cacert "$root_cert" --silent --show-error --connect-timeout 2 --max-time 5) for _ in $(seq 1 100); do curl "${curl_args[@]}" --fail "$base/_p2p/health" >"$tmp/health.json" 2>/dev/null && break - Network accessline 139
for _ in $(seq 1 100); do curl "${curl_args[@]}" --fail "$base/_p2p/health" >"$tmp/health.json" 2>/dev/null && break sleep 0.05 - Network accessline 140
curl "${curl_args[@]}" --fail "$base/_p2p/health" >"$tmp/health.json" 2>/dev/null && break - Network accessline 142
done grep -Fq '"status":"ok"' "$tmp/health.json" || { docker logs "$container" >&2; exit 1; } curl "${curl_args[@]}" --fail "$base/_matrix/client/v3/sync?timeout=0" >"$tmp/sync.json" - Network accessline 143
grep -Fq '"status":"ok"' "$tmp/health.json" || { docker logs "$container" >&2; exit 1; } curl "${curl_args[@]}" --fail "$base/_matrix/client/v3/sync?timeout=0" >"$tmp/sync.json" grep -Fq '"next_batch":"fault-gate"' "$tmp/sync.json" - Network accessline 144
curl "${curl_args[@]}" --fail "$base/_matrix/client/v3/sync?timeout=0" >"$tmp/sync.json" - Network accessline 147
# The first frame must cross Caddy before the delayed frame exists. The request # remains open until curl times out, which must propagate a disconnect upstream. - Network accessline 148
# remains open until curl times out, which must propagate a disconnect upstream. - Network accessline 149
set +e curl --cacert "$root_cert" --silent --show-error --no-buffer --max-time 3.5 \ - Network accessline 150
curl --cacert "$root_cert" --silent --show-error --no-buffer --max-time 3.5 \ - Network accessline 151
[Credential-related source omitted] - Network accessline 168
sse_status=$? set -e [ "$sse_status" -eq 28 ] || { echo "SSE disconnect probe returned $sse_status, expected curl timeout 28" >&2; exit 1; } - Network accessline 169
set -e [ "$sse_status" -eq 28 ] || { echo "SSE disconnect probe returned $sse_status, expected curl timeout 28" >&2; exit 1; } grep -Fq 'data: delayed' "$tmp/sse.out" - Network accessline 170
[ "$sse_status" -eq 28 ] || { echo "SSE disconnect probe returned $sse_status, expected curl timeout 28" >&2; exit 1; } - Network accessline 177
stop_message message_failure=$(curl "${curl_args[@]}" -o /dev/null -w '%{http_code}' "$base/_p2p/health" || true) - Network accessline 178
message_failure=$(curl "${curl_args[@]}" -o /dev/null -w '%{http_code}' "$base/_p2p/health" || true) - Network accessline 179
[ "$message_failure" = 502 ] || { echo "Message Server outage returned HTTP $message_failure, expected 502" >&2; exit 1; } start_message curl "${curl_args[@]}" --fail "$base/_p2p/health" >"$tmp/recovered-health.json" - Network accessline 180
start_message curl "${curl_args[@]}" --fail "$base/_p2p/health" >"$tmp/recovered-health.json" curl "${curl_args[@]}" --fail "$base/_matrix/client/v3/sync?timeout=0" >"$tmp/recovered-sync.json" - Network accessline 181
curl "${curl_args[@]}" --fail "$base/_p2p/health" >"$tmp/recovered-health.json" - Network accessline 182
curl "${curl_args[@]}" --fail "$base/_matrix/client/v3/sync?timeout=0" >"$tmp/recovered-sync.json" - Network accessline 188
[Credential-related source omitted] - Network accessline 189
[Credential-related source omitted] - Network accessline 190
[ "$agent_failure" = 502 ] || { echo "Agent outage returned HTTP $agent_failure, expected 502" >&2; exit 1; } curl "${curl_args[@]}" --fail "$base/_p2p/health" >/dev/null curl "${curl_args[@]}" --fail "$base/_matrix/client/v3/sync?timeout=0 - Network accessline 191
curl "${curl_args[@]}" --fail "$base/_p2p/health" >/dev/null - Network accessline 192
curl "${curl_args[@]}" --fail "$base/_matrix/client/v3/sync?timeout=0" >"$tmp/agent-down-sync.json" - Network accessline 195
start_message start_agent curl "${curl_args[@]}" --fail "$base/_p2p/health" >/dev/null - Network accessline 196
[Credential-related source omitted] - Network accessline 197
curl "${curl_args[@]}" --fail "$base/_p2p/health" >/dev/null - Network accessline 198
[Credential-related source omitted]
tests/static_sites_edge_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 10
[ -z "$container" ] || docker rm -f "$container" >/dev/null 2>&1 || true - Dangerous shell operationline 11
rm -rf "$tmp" - Network accessline 57
rendered=$tmp/Caddyfile sed 's#__DIREXTALK_PUBLIC_DOMAIN__#http://:8080#g' "$caddy_source" >"$rendered" - Network accessline 58
sed 's#__DIREXTALK_PUBLIC_DOMAIN__#http://:8080#g' "$caddy_source" >"$rendered" - Network accessline 73
address=$(docker port "$container" 8080/tcp | head -n1) base_url=http://$address - Network accessline 74
base_url=http://$address - Network accessline 77
status= for _ in $(seq 1 100); do status=$(curl --silent --show-error --output "$body" --dump-header "$headers" \ - Network accessline 78
for _ in $(seq 1 100); do status=$(curl --silent --show-error --output "$body" --dump-header "$headers" \ --write-out '%{http_code}' "$base_url$public_path" || true) - Network accessline 79
status=$(curl --silent --show-error --output "$body" --dump-header "$headers" \ - Network accessline 80
--write-out '%{http_code}' "$base_url$public_path" || true)
tests/test_runner_entry_test.mjs
- Executable scriptline 1
Executable file
tests/tracked_text_lf_test.sh
tests/update_reset_ops_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 8
trap 'rm -rf "$tmp"' EXIT - Dangerous shell operationline 34
grep -Fq 'docker container rm -f "$production_edge_id"' "$reset_helper" - Access to secretsline 102
[Credential-related source omitted] - Access to secretsline 107
[Credential-related source omitted] - Dangerous shell operationline 117
rm -f "$reconcile_fixture/base/p2p/bootstrap.json" - Access to secretsline 118
[Credential-related source omitted] - Access to secretsline 140
[Credential-related source omitted] - Dangerous shell operationline 235
legacy_prelude=${legacy_prelude//sudo /} - Dangerous shell operationline 236
bash -c "$legacy_prelude" - Network accessline 276
[Credential-related source omitted] - Possible obfuscationline 276
[Credential-related source omitted] - Access to secretsline 276
[Credential-related source omitted] - Network accessline 279
domain_mode=user \ domain=ops.example.test \ as_url=https://ops.example.test \ - Network accessline 280
domain=ops.example.test \ as_url=https://ops.example.test \ instance_type=t3.small \ - Network accessline 281
as_url=https://ops.example.test \ - Access to secretsline 284
[Credential-related source omitted] - Network accessline 302
'mcp_daemon_install_command=legacy local MCP daemon install command' \ 'mcp_daemon_status_command=legacy local MCP daemon status command' \ mcp_daemon_url=http://127.0.0.1:19757/mcp \ - Network accessline 303
'mcp_daemon_status_command=legacy local MCP daemon status command' \ mcp_daemon_url=http://127.0.0.1:19757/mcp \ 'mcp_daemon_proxy_command=legacy local MCP proxy command' \ - Network accessline 304
mcp_daemon_url=http://127.0.0.1:19757/mcp \ - Access to secretsline 351
[Credential-related source omitted] - Dangerous shell operationline 367
assert_contains "$reset_calls" 'sudo sh -lc' - Access to secretsline 380
[Credential-related source omitted]
tests/updater_atomic_install_test.sh
tests/updater_bootstrap_resume_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 6
trap 'rm -rf "$tmp"' EXIT - Access to secretsline 13
[Credential-related source omitted] - Access to secretsline 14
[Credential-related source omitted] - Access to secretsline 166
[Credential-related source omitted] - Access to secretsline 170
[Credential-related source omitted]
tests/updater_bundle_test.sh
tests/updater_desired_state_transition_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 13
rm -rf "$tmp" - Network accessline 25
python3 - "$test_root/run/dirextalk-updater/http.sock" <<'PY' & import socket, sys, time s = socket.socket(socket.AF_UNIX) - Network accessline 26
import socket, sys, time s = socket.socket(socket.AF_UNIX) s.bind(sys.argv[1]) - Network accessline 27
s = socket.socket(socket.AF_UNIX) - Network accessline 57
fi EOF cat >"$test_bin/curl" <<'EOF' - Network accessline 58
EOF cat >"$test_bin/curl" <<'EOF' #!/usr/bin/env bash - Network accessline 59
cat >"$test_bin/curl" <<'EOF'
tests/updater_existing_state_transition_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 13
rm -rf "$tmp" - Dangerous shell operationline 21
rm -f "$tmp/socket.pid" - Network accessline 79
UPDATER_PIN_VERSION=v2.0.0 UPDATER_PIN_COMMIT=2222222222222222222222222222222222222222 UPDATER_PIN_URL=https://example.invalid/updater - Network accessline 80
UPDATER_PIN_COMMIT=2222222222222222222222222222222222222222 UPDATER_PIN_URL=https://example.invalid/updater UPDATER_PIN_ASSET=dirextalk-updater-linux-amd64 - Network accessline 81
UPDATER_PIN_URL=https://example.invalid/updater - Dangerous shell operationline 123
rm -f "$TEST_ROOT/run/dirextalk-updater/http.sock" - Network accessline 124
python3 - "$TEST_ROOT/run/dirextalk-updater/http.sock" <<'PY' & import socket, sys, time s = socket.socket(socket.AF_UNIX) - Network accessline 125
import socket, sys, time s = socket.socket(socket.AF_UNIX) s.bind(sys.argv[1]) - Network accessline 126
s = socket.socket(socket.AF_UNIX) - Dangerous shell operationline 165
if [ -f "$TEST_SOCKET_PID" ]; then kill "$(cat "$TEST_SOCKET_PID")" >/dev/null 2>&1 || true; rm -f "$TEST_SOCKET_PID"; fi - Dangerous shell operationline 166
rm -f "$TEST_ROOT/run/dirextalk-updater/http.sock" - Network accessline 179
esac EOF cat >"$TEST_BIN/curl" <<'EOF' - Network accessline 180
EOF cat >"$TEST_BIN/curl" <<'EOF' #!/usr/bin/env bash - Network accessline 181
cat >"$TEST_BIN/curl" <<'EOF' - Network accessline 187
--data) data=$2; shift 2 ;; --output) output=$2; shift 2 ;; http://*) url=$1; shift ;; - Network accessline 188
--output) output=$2; shift 2 ;; http://*) url=$1; shift ;; --unix-socket|--header|--write-out|--config) shift 2 ;; - Network accessline 189
http://*) url=$1; shift ;; --unix-socket|--header|--write-out|--config) shift 2 ;; --silent|--show-error) shift ;;
tests/updater_platform_contract_test.sh
tests/updater_release_download_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Dangerous shell operationline 12
trap 'rm -rf "$tmp"' EXIT - Access to secretsline 23
[Credential-related source omitted] - Network accessline 39
printf 'systemd %s\n' "$SYSTEMD_VERSION" EOF cat > "$tmp/bin/curl" <<'EOF' - Network accessline 40
EOF cat > "$tmp/bin/curl" <<'EOF' #!/usr/bin/env bash - Network accessline 41
cat > "$tmp/bin/curl" <<'EOF' - Network accessline 42
#!/usr/bin/env bash set -euo pipefail printf 'curl' >> "$BOOTSTRAP_CALLS"; printf ' %q' "$@" >> "$BOOTSTRAP_CALLS"; printf '\n' >> "$BOOTSTRAP_CALLS" - Network accessline 43
set -euo pipefail printf 'curl' >> "$BOOTSTRAP_CALLS"; printf ' %q' "$@" >> "$BOOTSTRAP_CALLS"; printf '\n' >> "$BOOTSTRAP_CALLS" output="" - Network accessline 44
printf 'curl' >> "$BOOTSTRAP_CALLS"; printf ' %q' "$@" >> "$BOOTSTRAP_CALLS"; printf '\n' >> "$BOOTSTRAP_CALLS" - Network accessline 112
assert_linux_mode 755 "$base/dirextalk-updater" grep -F -q "$UPDATER_PIN_URL" "$calls" if grep '^curl ' "$calls" | grep -qi latest; then - Network accessline 113
grep -F -q "$UPDATER_PIN_URL" "$calls" if grep '^curl ' "$calls" | grep -qi latest; then echo "bootstrap downloaded a mutable updater URL" >&2 - Network accessline 114
if grep '^curl ' "$calls" | grep -qi latest; then - Network accessline 126
before=$(grep -c '^curl' "$calls") - Dangerous shell operationline 128
rm -f "$base/.deploy-done" - Network accessline 128
rm -f "$base/.deploy-done" bash "$script" 203.0.113.20 after=$(grep -c '^curl' "$calls") - Network accessline 129
bash "$script" 203.0.113.20 after=$(grep -c '^curl' "$calls") [ "$before" = "$after" ] || { echo "matching updater binary should be reused" >&2; exit 1; } - Network accessline 130
after=$(grep -c '^curl' "$calls") - Dangerous shell operationline 135
rm -f "$base/.deploy-done" - Dangerous shell operationline 144
rm -f "$base/.deploy-done" - Dangerous shell operationline 154
rm -f "$base/.deploy-done" - Dangerous shell operationline 160
rm -f "$base/.deploy-done" - Dangerous shell operationline 166
rm -f "$base/.deploy-done"
tests/updater_release_pin_test.sh
- Executable scriptline 1
#!/usr/bin/env bash - Network accessline 15
[ "$UPDATER_PIN_VERSION" = v1.0.19 ] [ "$UPDATER_PIN_COMMIT" = 1e71b9d53c599e8fb9227050b8c9643ce723acc5 ] [ "$UPDATER_PIN_URL" = https://github.com/YingSuiAI/dirextalk-updater/releases/download/v1.0.19/dirextalk-updater-linux-amd64 ] - Network accessline 16
[ "$UPDATER_PIN_COMMIT" = 1e71b9d53c599e8fb9227050b8c9643ce723acc5 ] [ "$UPDATER_PIN_URL" = https://github.com/YingSuiAI/dirextalk-updater/releases/download/v1.0.19/dirextalk-updater-linux-amd64 ] [ "$UPDATER_PIN_ASSET" = dirextalk-updater- - Network accessline 17
[ "$UPDATER_PIN_URL" = https://github.com/YingSuiAI/dirextalk-updater/releases/download/v1.0.19/dirextalk-updater-linux-amd64 ] - Dangerous shell operationline 29
trap 'rm -rf "$tmp"' EXIT
How the signals fit together
Facts from a static read of the files at the pinned commit. They describe what the code does, not why.
Some files could not be read; the facts below still hold.
Combined signals: 1 fact
- Reads cloud credentials; another file of the same skill sends data over the network or runs a command (bin/dirextalk-deployer.mjs, line 76)scripts/aws-credentials.sh:25Low confidence
Signal confidence: 499 facts
- Network access in the frontmatter of the SKILL.mddirextalk-deployer/SKILL.md:13Low confidence
- Network access in the frontmatter of the SKILL.mddirextalk-deployer/SKILL.md:14Low confidence
- Network access in the frontmatter of the SKILL.mddirextalk-deployer/SKILL.md:15Low confidence
- Network access in code of the SKILL.mddirextalk-deployer/SKILL.md:62High confidence
- Network access in prose of documentationAGENTS.md:60Low confidence
- Network access in prose of documentationAGENTS.md:61Low confidence
- Network access in prose of documentationAGENTS.md:62Low confidence
- Access to secrets in prose of documentation: a variable, placeholder or call, not a stored valueAGENTS.md:69Low confidence
- Access to secrets in prose of documentationAGENTS.md:81Low confidence
- Network access in prose of documentationREADME.md:7Low confidence
- Network access in prose of documentationREADME.md:19Low confidence
- Network access in prose of documentationREADME.md:21Low confidence
- Network access in prose of documentationREADME.md:44Low confidence
- Network access in code of documentationREADME.md:57Low confidence
- Network access in prose of documentationREADME.md:142Low confidence
- Network access in prose of documentationREADME.md:143Low confidence
- Network access in prose of documentationREADME.md:144Low confidence
- Network access in prose of documentationREADME.md:157Low confidence
- Access to secrets in prose of documentationREADME.md:312Low confidence
- Network access in code of documentationREADME.md:317Low confidence
- Network access in prose of the SKILL.mdSKILL.md:36Low confidence
- Network access in prose of the SKILL.mdSKILL.md:37Low confidence
- Network access in prose of the SKILL.mdSKILL.md:38Low confidence
- Network access in prose of the SKILL.mdSKILL.md:77Low confidence
- Network access in prose of the SKILL.mdSKILL.md:78Low confidence
- Network access in prose of the SKILL.mdSKILL.md:79Low confidence
- Network access in prose of the SKILL.mdSKILL.md:128Low confidence
- Network access in prose of the SKILL.mdSKILL.md:129Low confidence
- Network access in prose of the SKILL.mdSKILL.md:130Low confidence
- Network access in prose of the SKILL.mdSKILL.md:309Low confidence
- Network access in prose of the SKILL.mdSKILL.md:310Low confidence
- Network access in prose of the SKILL.mdSKILL.md:311Low confidence
- Executable script in code of a file that runsbin/dirextalk-deployer.mjs:1High confidence
- Network access in code of a file that runsbin/dirextalk-deployer.mjs:76High confidence
- Executable script in code of a file that runspackage.json:1High confidence
- Network access in prose of documentationreferences/agent-targets.md:20Low confidence
- Network access in code of documentationreferences/agent-targets.md:27Low confidence
- Access to secrets in code of documentation: a variable, placeholder or call, not a stored valuereferences/agent-targets.md:96Low confidence
- Network access in prose of documentationreferences/architecture.md:20Low confidence
- Network access in prose of documentationreferences/architecture.md:21Low confidence
- Access to secrets in prose of documentationreferences/architecture.md:44Low confidence
- Access to secrets in prose of documentation: a variable, placeholder or call, not a stored valuereferences/bug-history.md:44Low confidence
- Access to secrets in prose of documentationreferences/bug-history.md:50Low confidence
- Dangerous shell operation in prose of documentationreferences/bug-history.md:66Low confidence
- Network access in prose of documentationreferences/bug-history.md:66Low confidence
- Network access in prose of documentationreferences/bug-history.md:68Low confidence
- Network access in prose of documentationreferences/deployment-lessons.md:54Low confidence
- Network access in prose of documentationreferences/deployment-lessons.md:55Low confidence
- Network access in prose of documentationreferences/deployment-lessons.md:72Low confidence
- Network access in prose of documentationreferences/deployment-lessons.md:73Low confidence
and 449 more
Only the first 500 facts are listed.
Works with
| Agent | Status | Evidence | Install to |
|---|---|---|---|
| Claude Code | Compatible | Standard SKILL.md SKILL.md | .claude/skills/<skill-name>/ |
| Codex | Native | Manifest AGENTS.md | .agents/skills/<skill-name>/ |
| Cursor | Compatible | Standard SKILL.md SKILL.md | .cursor/skills/<skill-name>/ |
| Gemini CLI | Compatible | Standard SKILL.md SKILL.md | .gemini/skills/<skill-name>/ |
| GitHub Copilot | Compatible | Standard SKILL.md SKILL.md | .github/skills/<skill-name>/ |
| OpenCode | Compatible | Standard SKILL.md SKILL.md | .opencode/skills/<skill-name>/ |
- Native The repository ships a manifest, folder or frontmatter field for this agent.
- Compatible A standard SKILL.md that this agent can read.
- Unknown No evidence either way.
Derived automatically from paths, manifests and frontmatter. Not tested on each agent.
